 Do Son
Microsoft explains why deleting Windows 11 Prefetch files degrades application startup performance while highlighting their crucial digital forensics role.
Incident Response

The Hugging Face breach was driven end-to-end by an autonomous AI agent attack. Internal datasets and service credentials were exposed.
Discover how nation-state hackers leverage the ROADtools cloud attack toolkit to compromise Entra ID environments and bypass MFA controls.
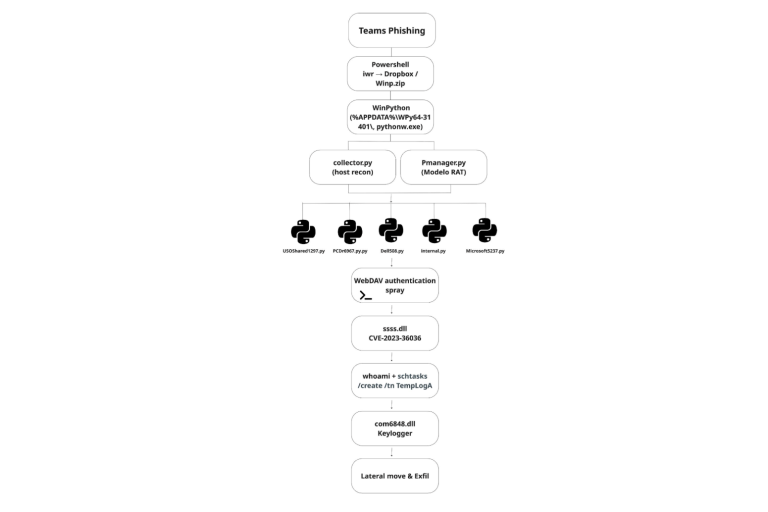
Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.

In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...
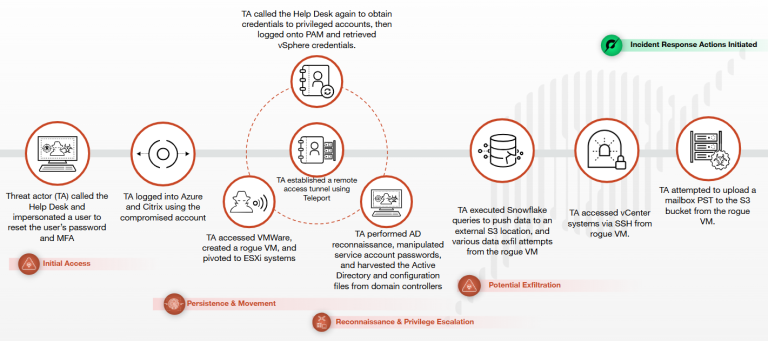
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

A new report reveals that an exposed Oracle Database was the entry point for a ransomware attack. Hackers used a scheduler function to gain access and deploy malware.

The DOJ is criminally investigating a former DigitalMint ransomware negotiator for allegedly colluding with hackers and taking a cut of ransom payments, a betrayal of client trust.

Kaspersky warns organizations are overestimating container isolation. New analysis reveals hidden attack surfaces and crucial detection blind spots.

Learn how interactive sandboxes like ANY.RUN can detect and analyze Microsoft 365 phishing attacks in real-time, preventing silent breaches and data exfiltration.

Commvault updates its March advisory after detecting nation-state threat activity in Azure; no data breach confirmed, advanced defenses deployed.