 Do Son
The UK NCSC warns of rising cyberattacks on operational technology, urging organizations to secure internet-exposed industrial systems against physical disruptions.
industrial control systems

ABB addresses critical ABB T-MAC Plus vulnerabilities. Learn how these terminal system flaws allow authentication bypass and file disclosure.
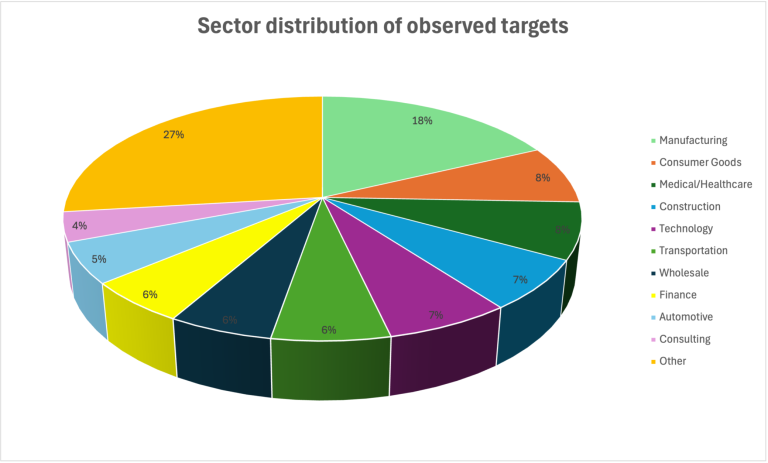
Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.

Critical 9.1 CVSS flaw in Horner Automation PLCs allows unauthenticated brute force attacks. Secure your industrial systems—patch XL4, XL7, and Cscape now!

Apache IoTDB issues an urgent fix for a critical JEXL injection flaw (CVE-2026-24713) and insecure defaults. Upgrade to 1.3.7 or 2.0.7 to secure your IIoT data.

CISA issues an urgent ICS advisory (ICSA-26-057-04) for the EV2GO charging platform. Critical 9.4 severity flaws allow for session hijacking and station impersonation.

CISA warns of critical Airleader Master vulnerability CVE-2026-1358. Unauthenticated attackers can upload files and gain RCE. Update to 6.386 now.

CISA warns of critical vulnerabilities in ProGauge MagLink fuel monitors, leaving fuel stations and industrial sites at risk of denial-of-service and unauthorized access.
A set of ten critical flaws, dubbed "Frostbyte10," were found in industrial controllers. These bugs could allow attackers to tamper with global food and medicine supply chains.

A critical flaw (CVE-2025-41702) in Welotec egOS allows unauthenticated attackers to impersonate administrators, gain full control, and disrupt industrial systems.

Siemens has issued a high-severity alert for a critical vulnerability in its SIMATIC RTLS Locating Manager. The flaw could allow remote code execution with high privileges.

A critical vulnerability (CVE-2025-32433, CVSS 10.0) in Erlang/OTP’s SSH daemon allows unauthenticated RCE and is actively exploited, with a focus on operational technology (OT) networks.
Weidmueller IE-SR-2TX series security routers have critical flaws (CVSS 9.8) allowing unauthenticated RCE and buffer overflows, risking industrial automation and critical infrastructure.

Two flaws (CVE-2025-6376/6377 in Rockwell Arena Simulation allow RCE via crafted DOE files. Update to 16.20.09 immediately; avoid untrusted files.

CISA warns of critical flaws in Emerson ValveLink software, exposing cleartext data, allowing code execution, and compromising industrial systems. Update to v14.0 now.

Siemens warns of critical flaws (CVE-2025-40736 CVSS 9.8 Auth Bypass, SQLi, Path Traversal) in SINEC NMS, allowing unauthenticated remote root access and RCE.

CERT@VDE warns of critical OS command injection flaws (CVE-2025-3626, CVE-2025-3705) in Frauscher railway systems, allowing remote admin compromise or physical attack via USB.

Over 143,000 ICS devices in the power sector are publicly exposed to the internet, facing high/critical vulnerabilities. Urgent action is needed to secure global energy infrastructure.

Pro-Russian hacktivists intensify 2025 digital assaults on Ukraine, NATO, and Western critical infrastructure, using DDoS, defacements, and targeting ICS.
CISA warns of critical flaws in ControlID iDSecure On-premises, including SQL Injection, auth bypass, and SSRF, risking vehicle access control systems.

Hitachi Energy warns of 5 flaws in MicroSCADA X SYS600 (v10.0-10.6), including remote DoS, data leaks, and TLS MITM, risking power system control.

Moxa warns of a high-severity DoS flaw (CVE-2024-9404) in PT-G7728/7828 industrial switches, allowing remote crashes. Update firmware or disable affected services.