
 Do Son
Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!
infosec

Apache Polaris 1.4.1 fixes critical flaws allowing attackers to bypass S3/GCS boundaries and seize cloud credentials. Patch your Iceberg catalog now!

Google warns of CVE-2026-0073: a critical zero-click Android vulnerability allowing remote code execution via Wireless ADB. Patch to May 2026 level now!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.
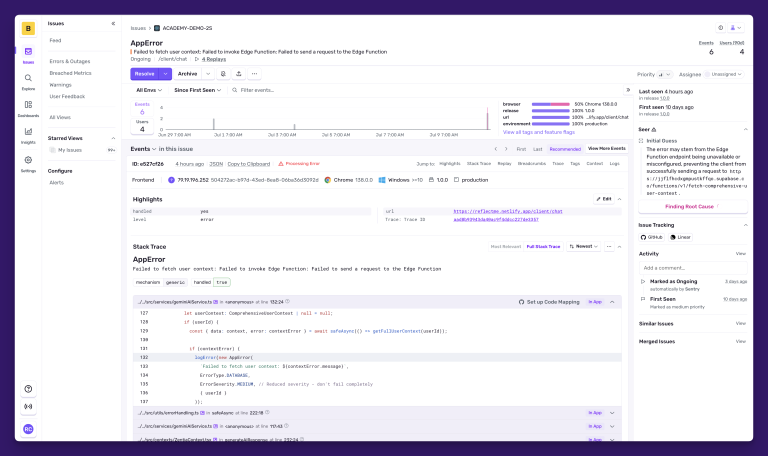
Sentry reveals a critical 9.1 CVSS flaw (CVE-2026-42354) in SAML SSO. Multi-org instances are at risk of account takeover via identity linking. Patch now!

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!
OpenAI launches Advanced Account Security for high-risk users. Features include mandatory passkeys, disabled SMS recovery, and automatic training exclusion.
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!
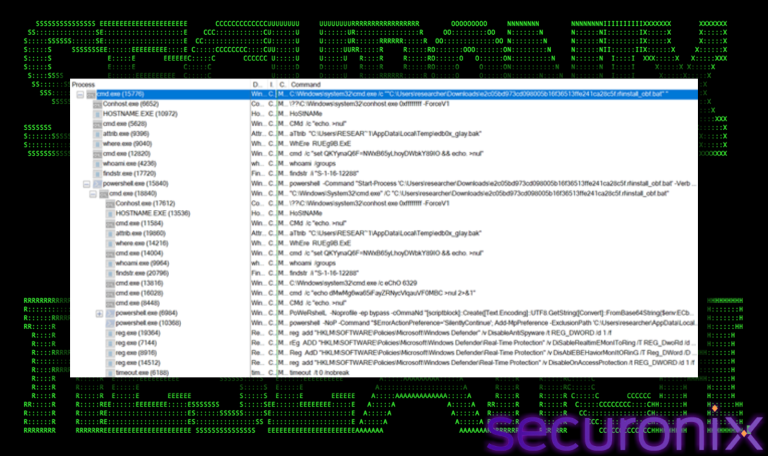
Meta Description (152 Characters)Securonix uncovers Deep#Door: a self-contained Python RAT that uses TCP tunneling and obfuscated scripts to bypass traditional defense. Secure your systems now.
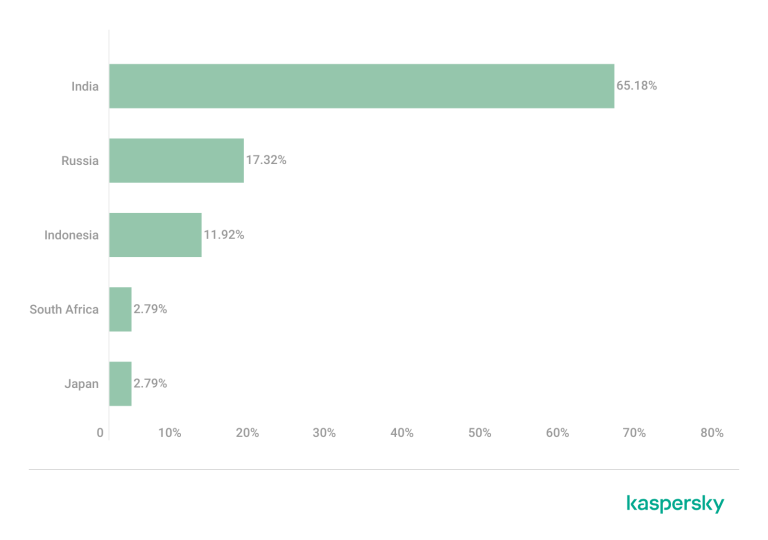
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.

Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.

Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

Snyk warns of active in-the-wild exploitation of the Qinglong platform. Two authentication bypass flaws grant attackers RCE to deploy .fullgc cryptominers.
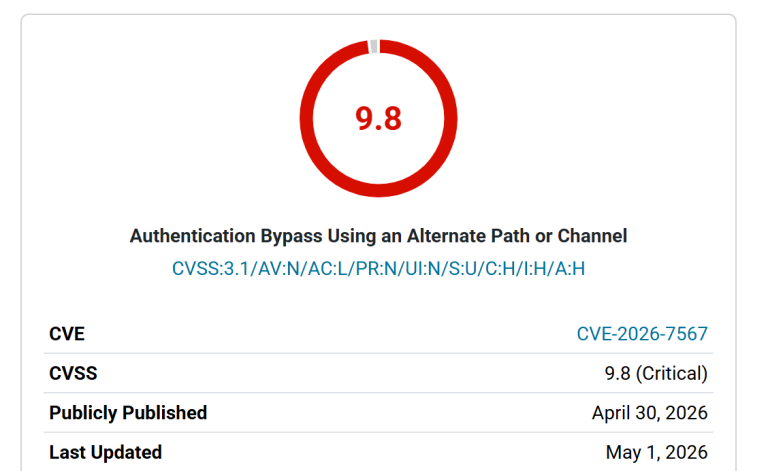
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
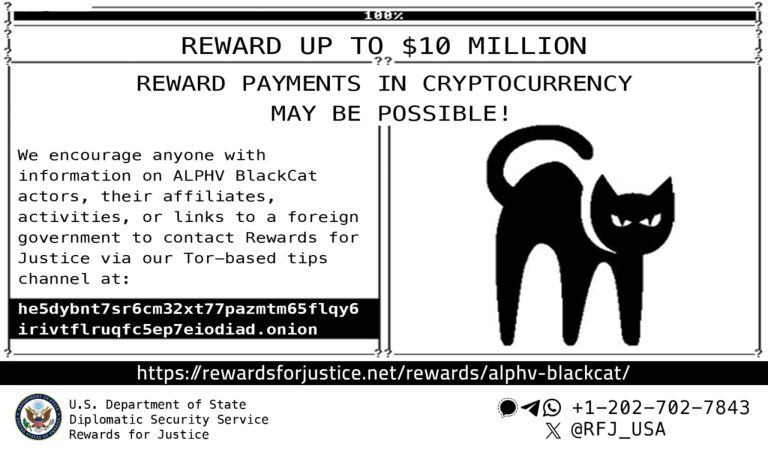
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
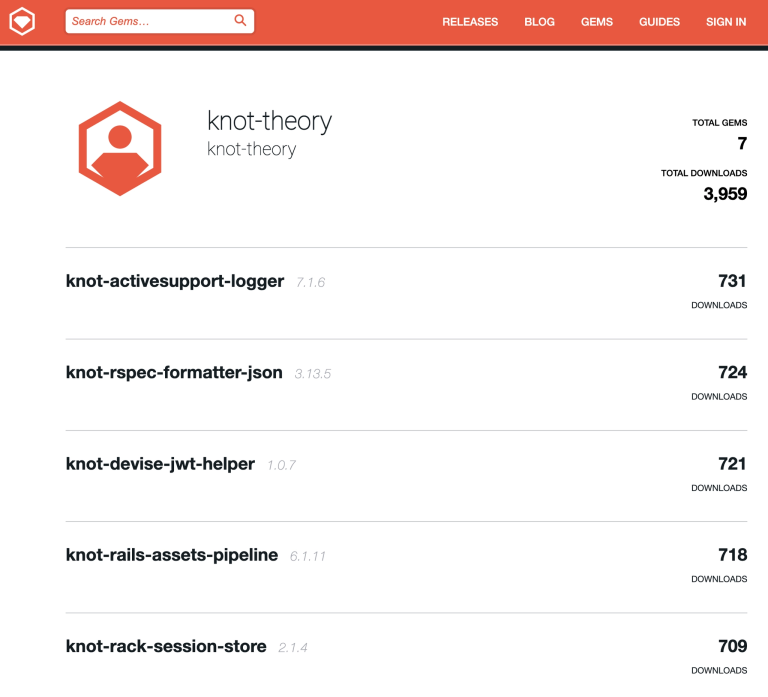
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.