 Do Son
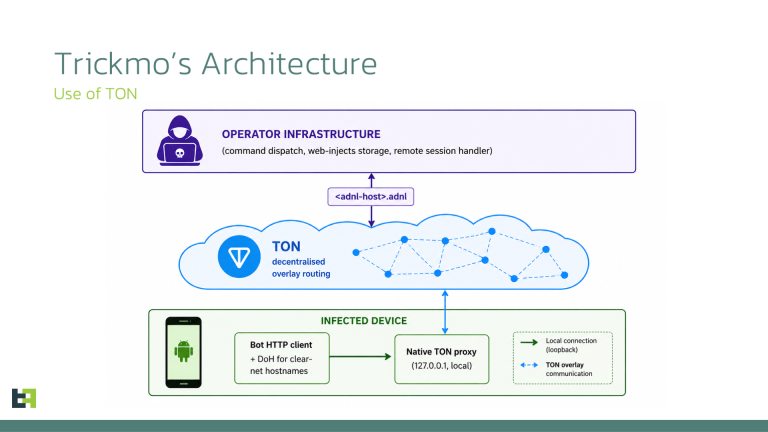
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
infosec
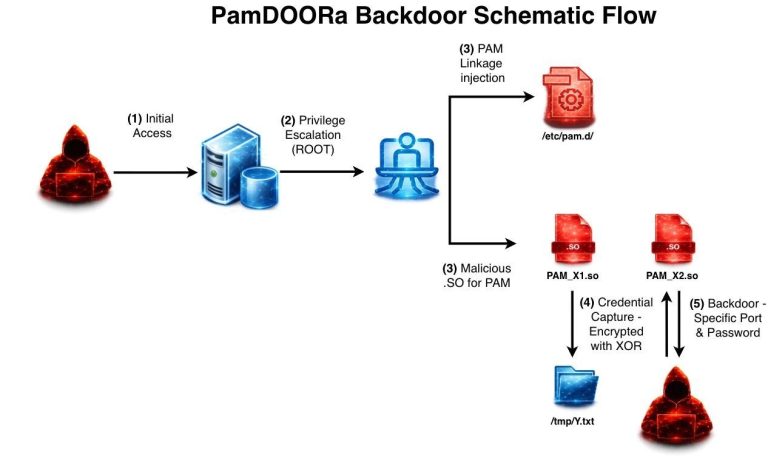
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.

Urgent: Dell patches a 9.8 severity credential flaw (CVE-2026-40636) in ECS and ObjectScale. Secure your enterprise storage by upgrading to version 4.3.0.0.
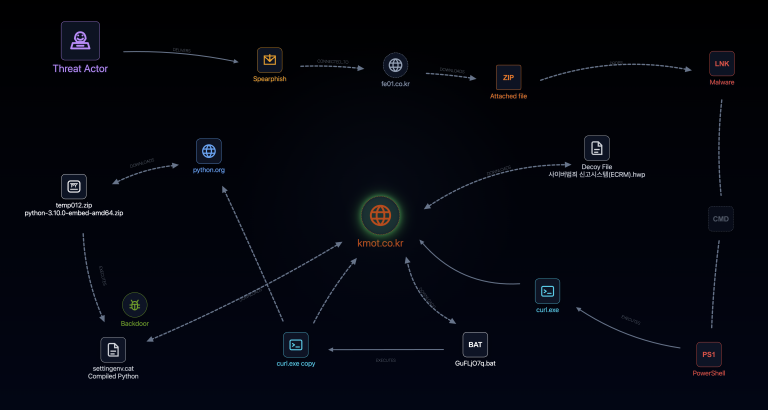
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.

SAP’s May 2026 Patch Day fixes two 9.6 severity flaws in S/4HANA and Commerce Cloud. Prevent SQL injection and RCE by updating your SAP landscape today.
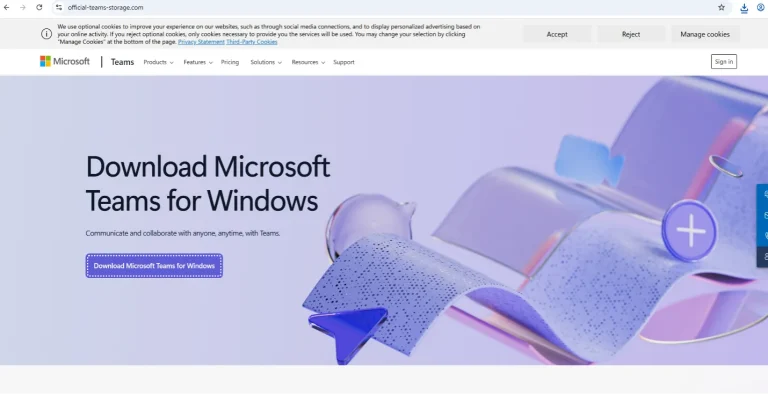
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
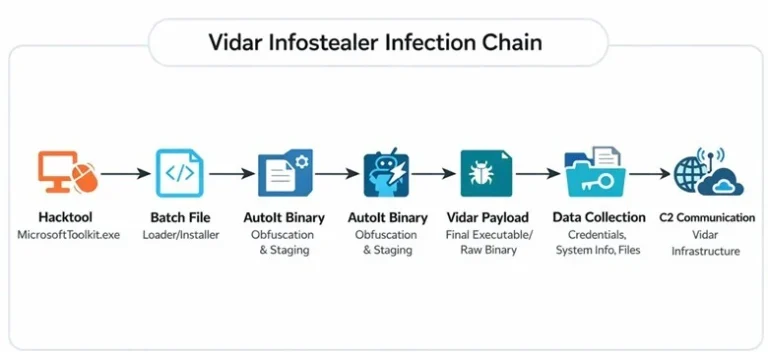
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
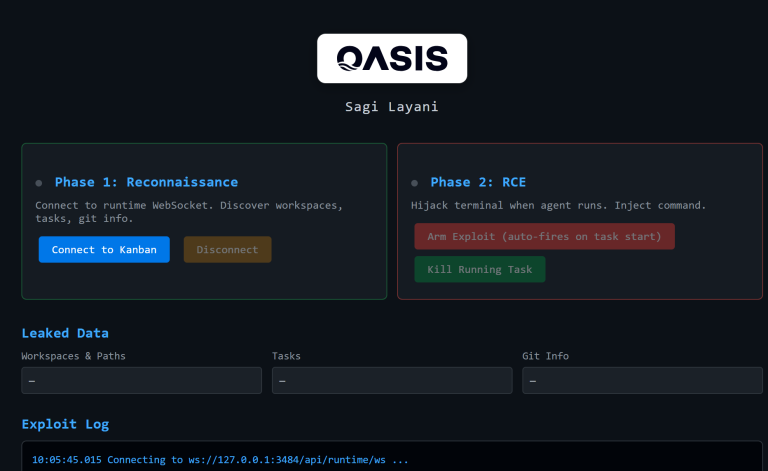
Critical Alert: CVE-2026-44211 (CVSS 9.6) in Cline AI allows malicious sites to hijack your terminal and steal data via WebSockets. Update your CLI tools now.
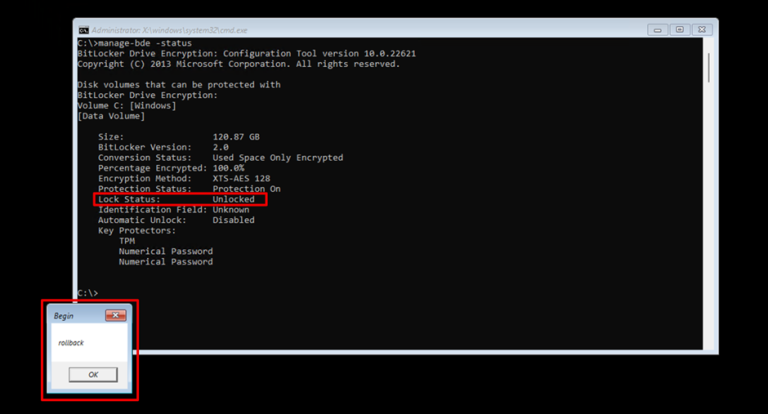
Public PoC Alert: The BitUnlocker Downgrade Attack bypasses BitLocker on patched Windows 11 machines in under 5 minutes. Learn how to secure your TPM with a PIN.
Netskope exposes Hologram: a red-team-grade malware framework targeting OpenClaw AI users with CLR injection and WinLogon hijacking to steal crypto wallets.
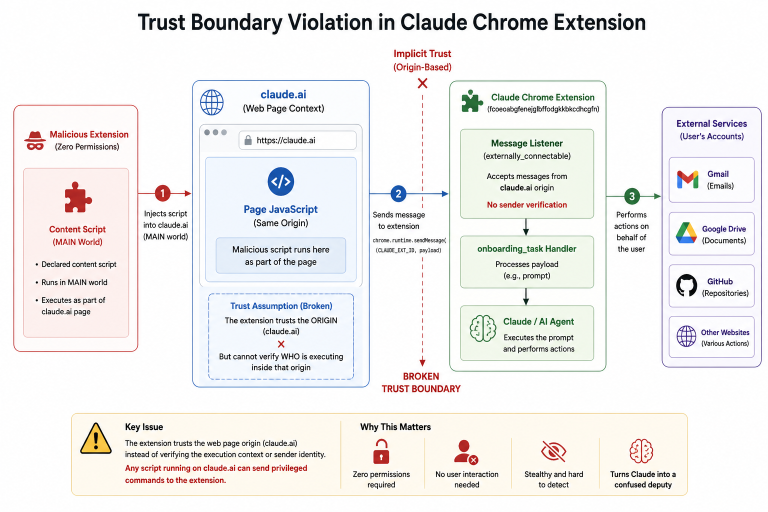
LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.
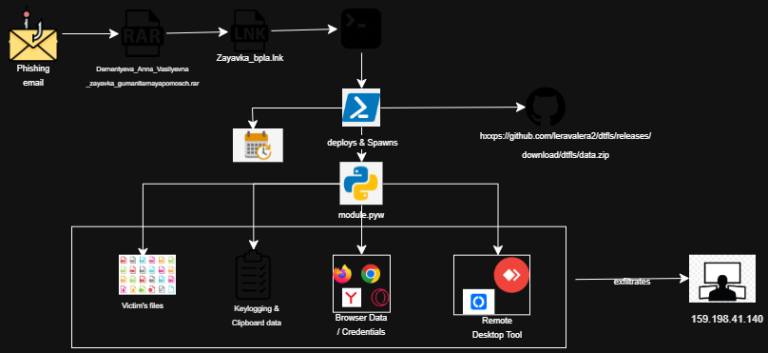
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.

Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.
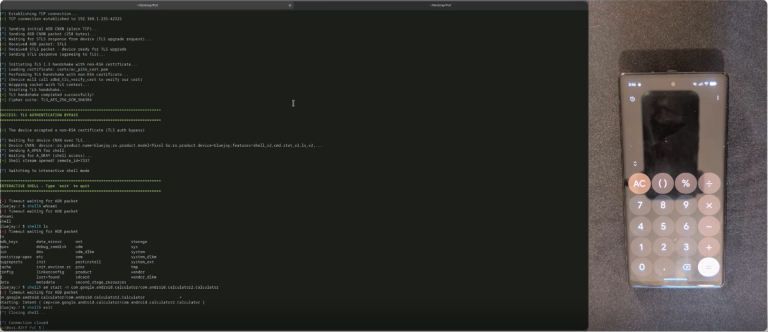
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!

Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!

JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.

The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.