 Do Son
New research by Intezer reveals the OrBit Linux rootkit is actually a fork of the open-source Medusa kit, actively weaponized across multiple APTs.
infosec

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.
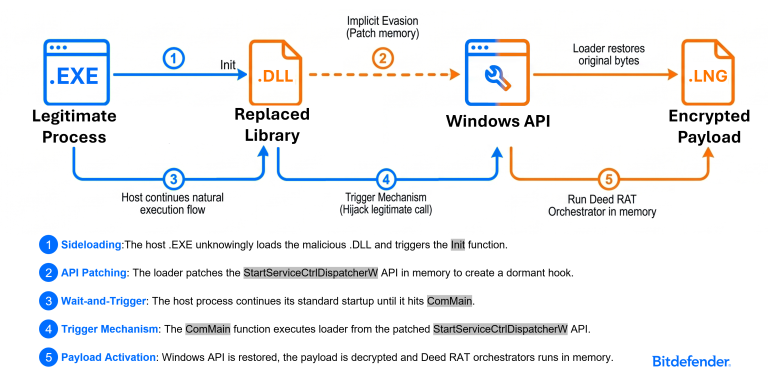
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!
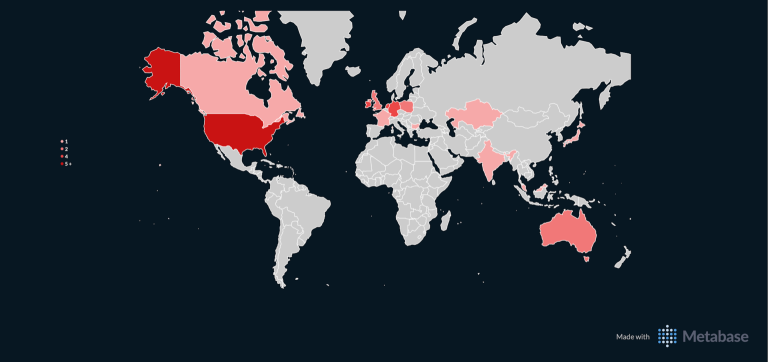
Urgent: CrowdSec warns CVE-2024-9643 in Four-Faith routers has hit mass exploitation phase. Attackers abuse hardcoded logins to build botnets. Patch now!

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.

Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!
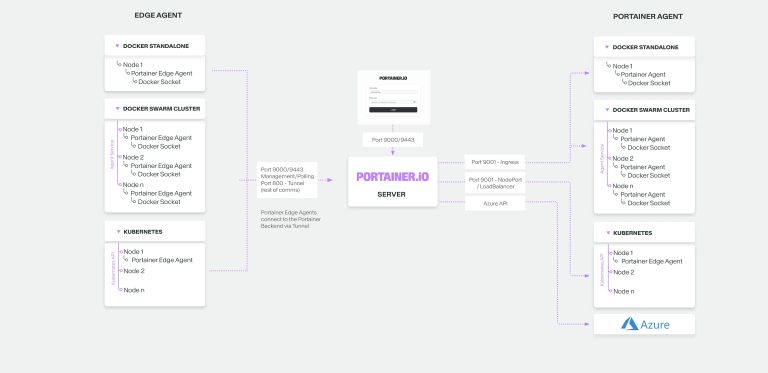
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!
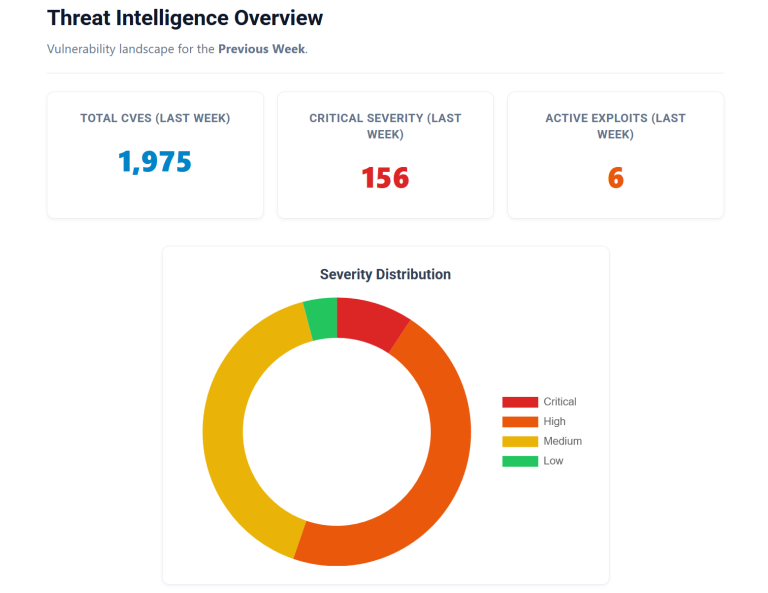
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.

n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!

The GhostLock whitepaper exposes a critical blind spot in ransomware defense. Low-privilege users can freeze SMB shares with zero data encryption.