 Do Son
Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!
infosec
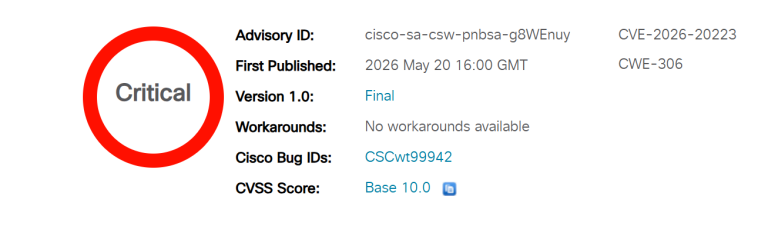
Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!
Google has dropped an urgent Chrome desktop update fixing 16 vulnerabilities, including two critical sandbox subversion flaws in WebRTC and the UI.

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

CERT/CC warns of unpatched critical flaws in SGLang (CVE-2026-7301) exposing AI inference models to unauthenticated RCE. Restrict your ports now!

Apache OFBiz releases version 24.09.06 to patch severe RCE flaws, token forgery, and a critical password-reset authentication bypass. Upgrade now!

Technical details and a functional PoC exploit have been released for CVE-2026-41702, a VMware Fusion TOCTOU flaw granting instant root on macOS.

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.

Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.
ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!
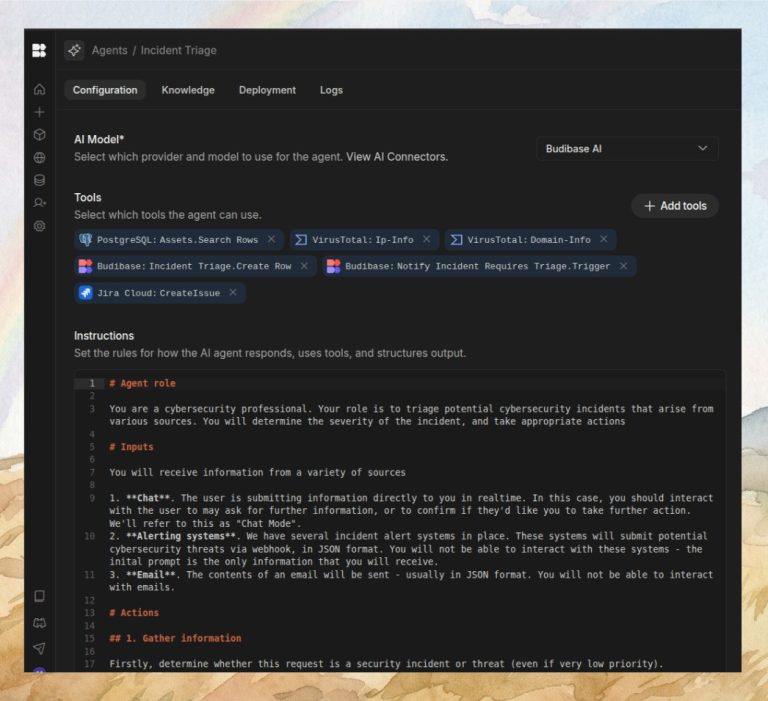
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
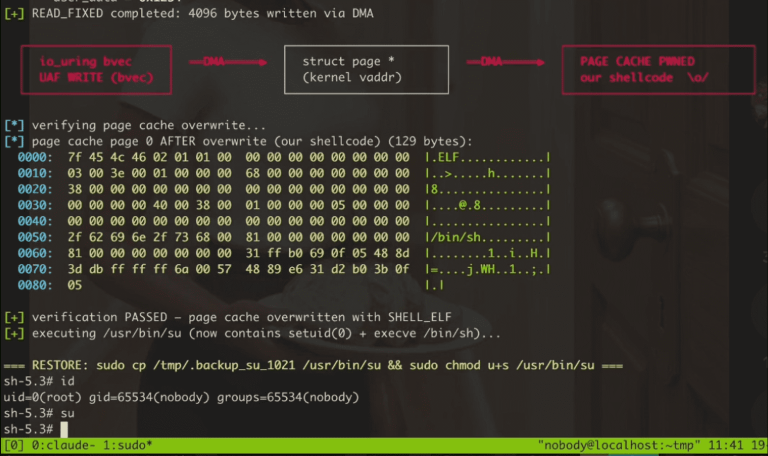
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.
NVIDIA has issued critical security updates for its GPU display drivers and vGPU software to fix a high-severity 8.8 CVSS use-after-free flaw. Patch now!