 Do Son
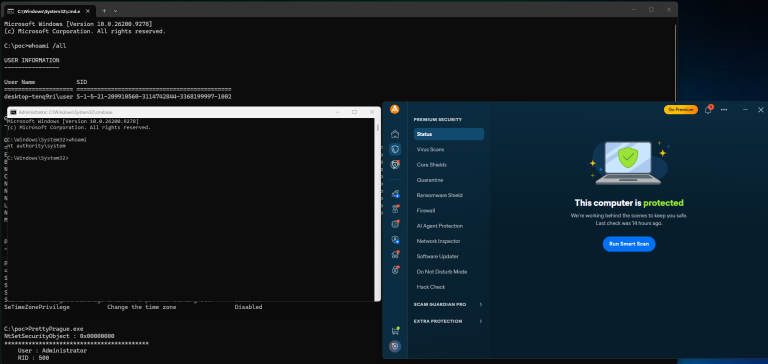
Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
infosec
Anthropic is sending security warnings and deleting payment methods as info-stealing malware compromises Claude user sessions. Protect your account now.
The UK NCSC warns of rising cyberattacks on operational technology, urging organizations to secure internet-exposed industrial systems against physical disruptions.
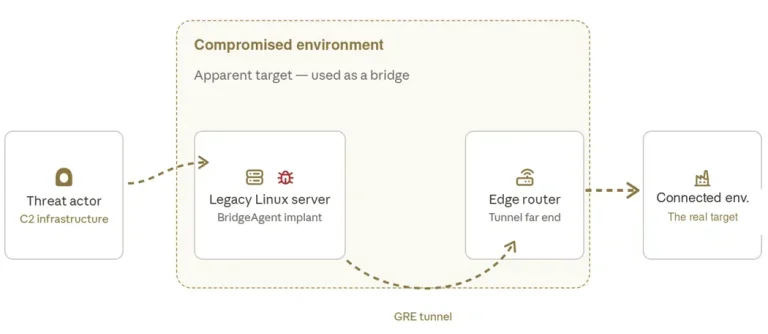
The Fire Ant threat actor uses trusted infrastructure compromise to breach high-value targets. Discover how this group evades detection in networks.
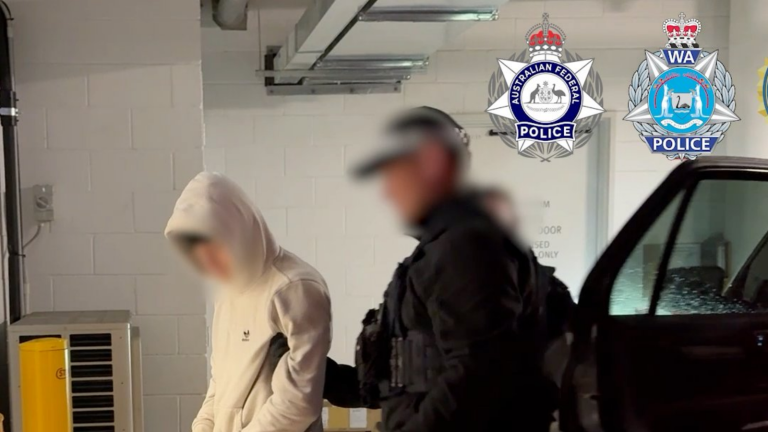
Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
Discover the details of the massive Mercor data breach exposing 4TB of recruiting data for OpenAI, Google, Meta, and Microsoft.
The Jewelbug APT group runs espionage alongside cryptocurrency scams. Read our report on Jewelbug APT group operations.

Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.

Kaspersky uncovered the Armored Likho Still Toolkit. Read our Armored Likho Still Toolkit analysis to explore the Telegram stealer and audio spying tools.

Zscaler ThreatLabz analysts discovered the Abyssos modular RAT. This Abyssos RAT gives attackers total remote control, stealing data and credentials.
Palo Alto Networks analyzed Kimwolf botnet malware. Read our Kimwolf botnet malware analysis to learn how it attacks Android TV boxes.

Kaspersky analyzed the Project CAV3RN framework. Read our Project CAV3RN framework analysis to see how attackers abuse DNS and Google Apps Script.
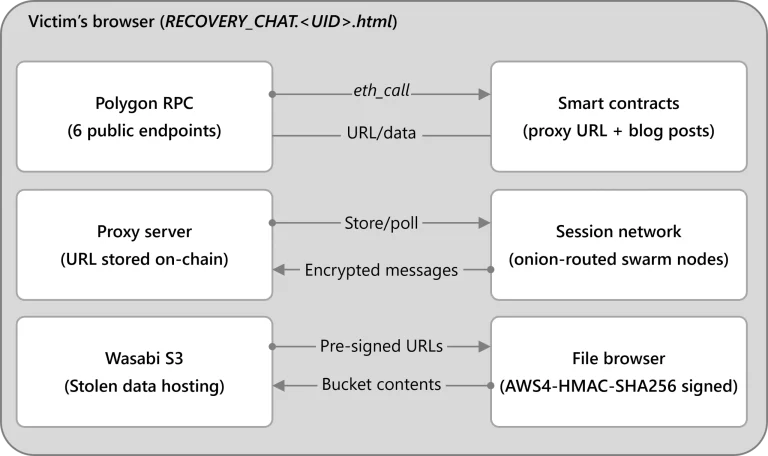
DeadLock ransomware uses blockchain nodes and Session chat. Learn how the DeadLock ransomware encryptor targets networks worldwide.

Discover how AI driven cyberattacks have become the most lethal weapon for hackers in 2026, increasing breach costs and targeting critical infrastructure.

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.

New Axios proxy vulnerabilities expose apps. A critical prototype pollution gadget allows full traffic interception. Secure patches are now available.
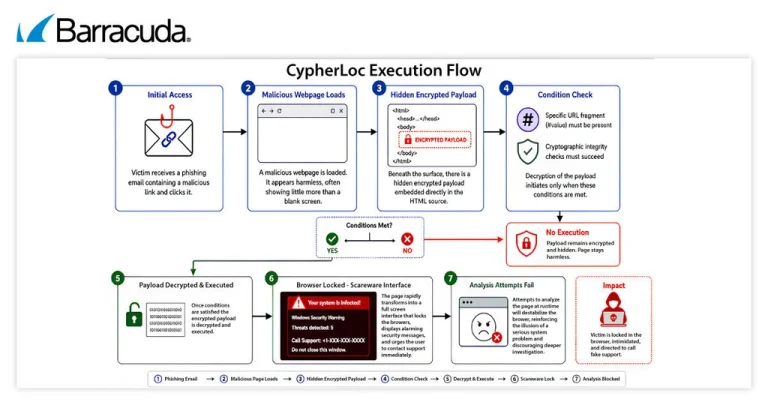
Barracuda Research warns of the CypherLoc scareware kit. Learn how this browser-locking threat uses psychological manipulation to scam users.

HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
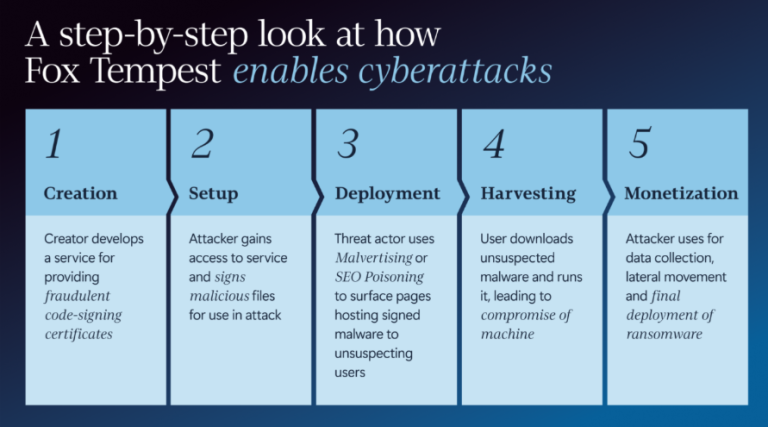
Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.