 Do Son
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.
infosec
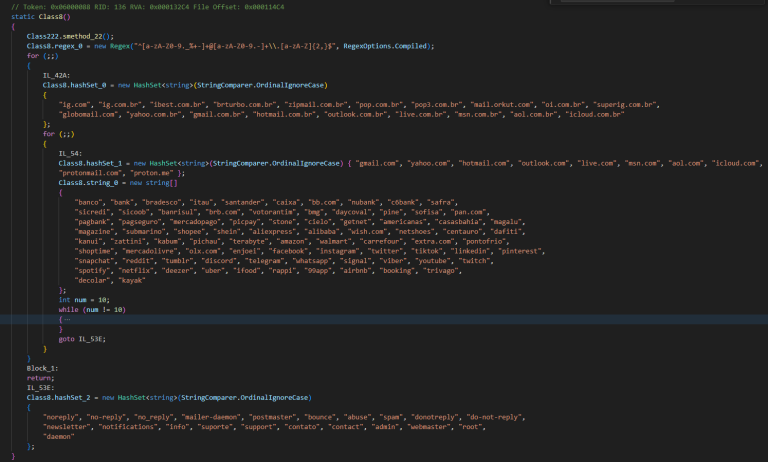
Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.
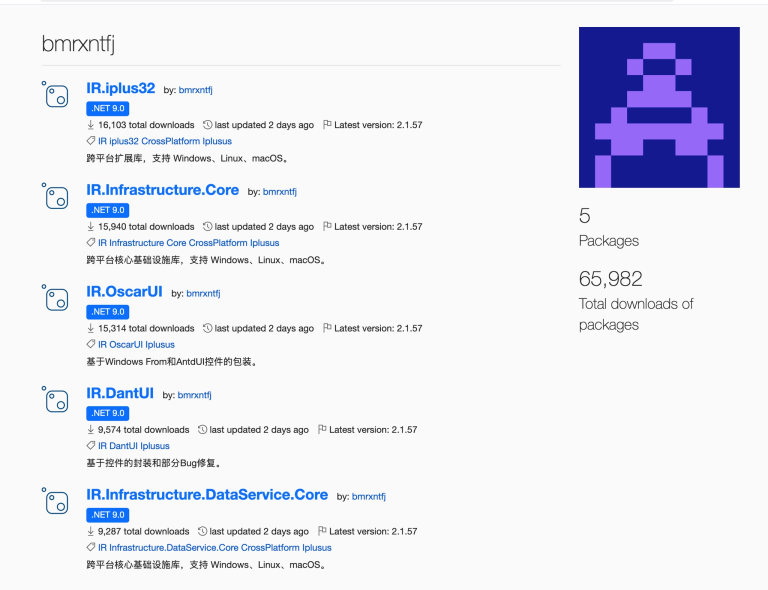
Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
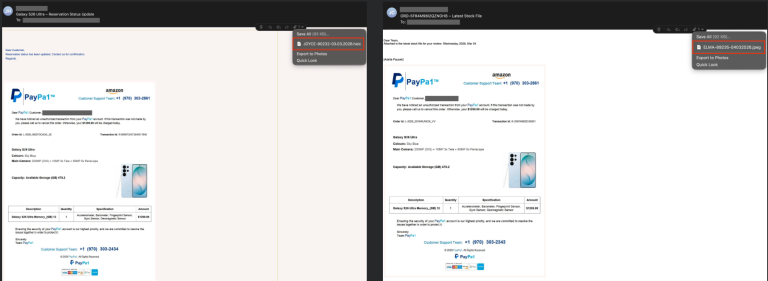
Cisco Talos reveals the rise of TOAD attacks. 55% of scam campaigns now use VoIP "anchors" to bypass email filters and trick victims into calling fraud centers.
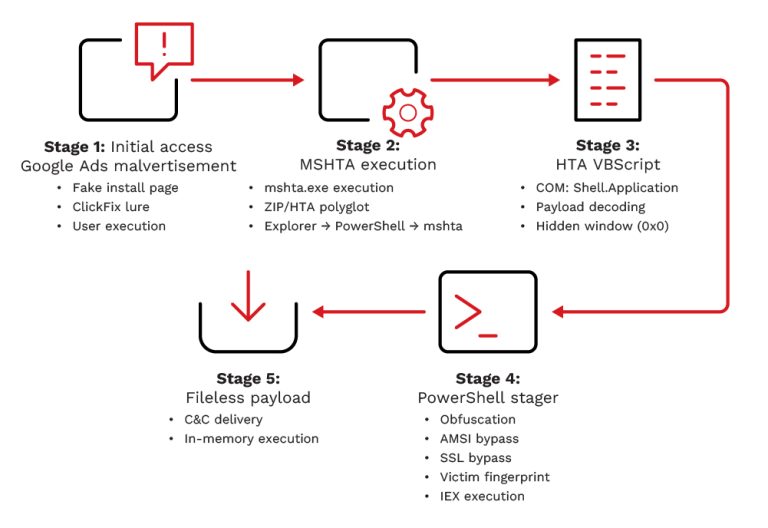
Beware of InstallFix: Fake Claude AI Google Ads trick users into running fileless scripts that deploy RedLine Stealer to steal passwords and crypto.
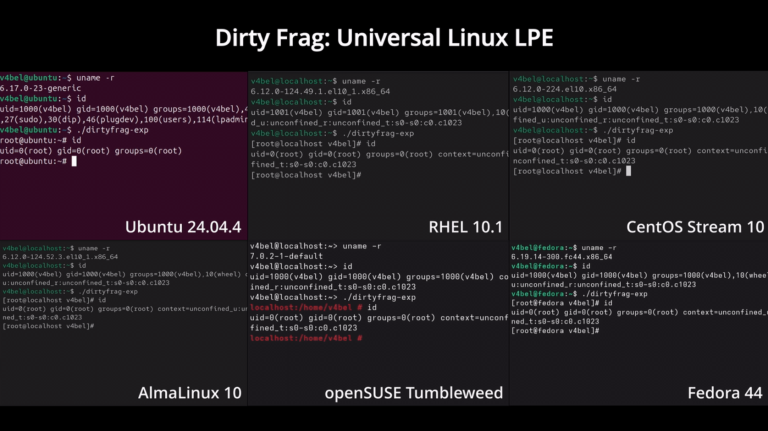
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!

Rancher Fleet fixes a 9.9 CVSS flaw (CVE-2026-41050) allowing tenants to bypass ServiceAccount isolation and steal secrets. Upgrade your GitOps engine now!

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
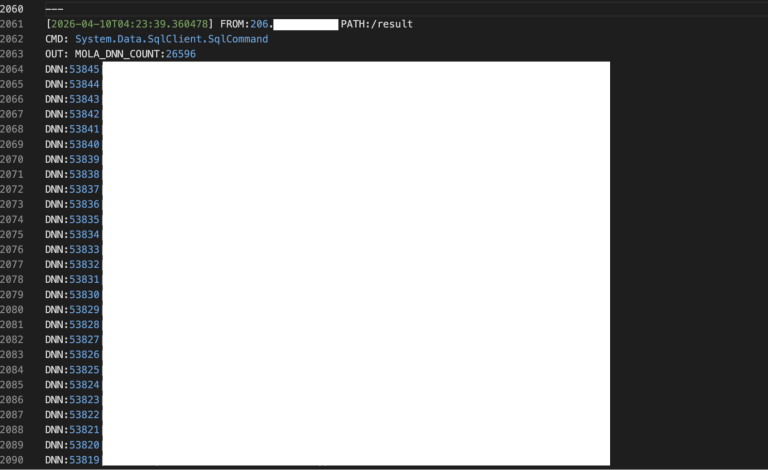
Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.
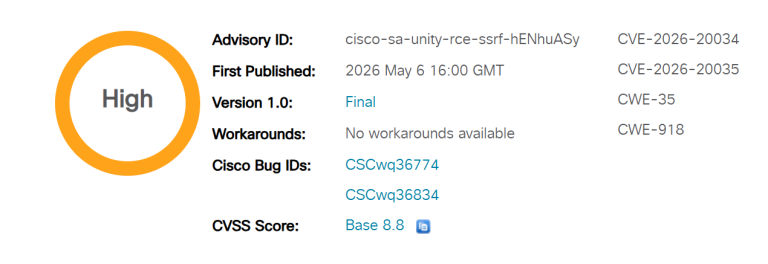
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
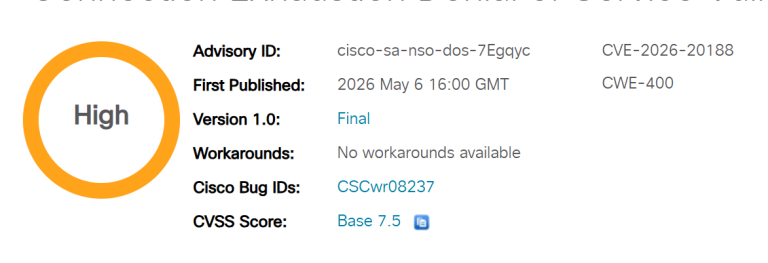
Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!
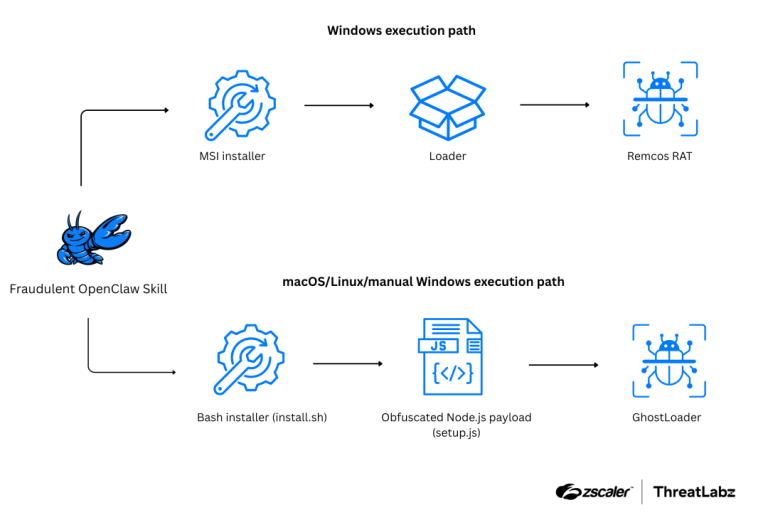
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!

Cisco Talos exposes Pheno, a malware plugin that hijacks Microsoft Phone Link to steal SMS and 2FA codes without touching your phone. Secure your PC today!

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!
Spring Cloud Config fixes a 9.1 CVSS directory traversal (CVE-2026-40982) and a GCP secret leak. Secure your distributed system—upgrade to the latest patches!

Bitcoin Core v29.0 fixes a high-severity use-after-free bug (CVE-2024-52911) that could allow attackers to remotely crash nodes. Upgrade your node today.

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!