
 Do Son
A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.
Infostealer

DarkCloud Stealer resurfaces in 2025 with AutoIt scripting and multi-stage obfuscation, targeting sensitive browser, email, and FTP credentials.

Chihuahua Stealer uses stealthy PowerShell loaders, CNG AES-GCM encryption, and .NET memory injection to exfiltrate browser and crypto wallet data.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

Unit 42 uncovers a sophisticated Lampion malware campaign using ClickFix social engineering tactics to target government and financial sectors in Portugal.
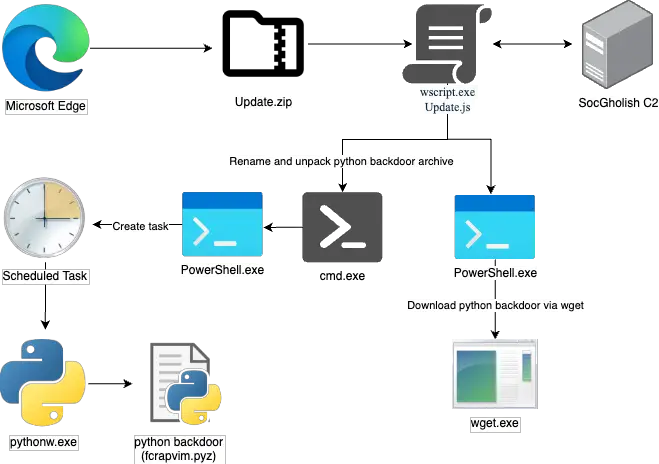
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

Trellix analysis reveals Lumma Stealer's latest tactics: code obfuscation, API hashing, ETW evasion, anti-VM. Learn how this InfoStealer avoids detection.

A new phishing campaign delivers FormBook malware via Word docs, exploiting CVE-2017-11882. The fileless attack uses process hollowing to evade detection.

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.
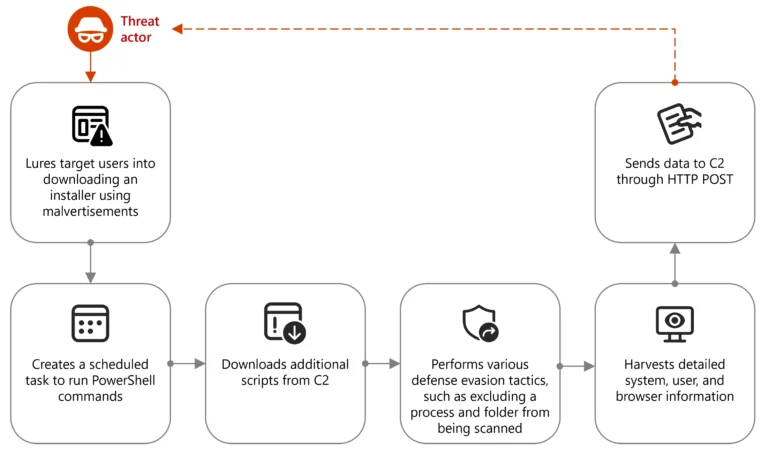
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

TROX Stealer exploits urgency via phishing emails to deliver obfuscated MaaS malware that steals credit cards, browser data, and crypto wallets
Uncover the details of a sophisticated phishing campaign distributing AsyncRAT and the Infostealer plugin. Learn how cybercriminals bypass security defenses and infiltrate victim systems.
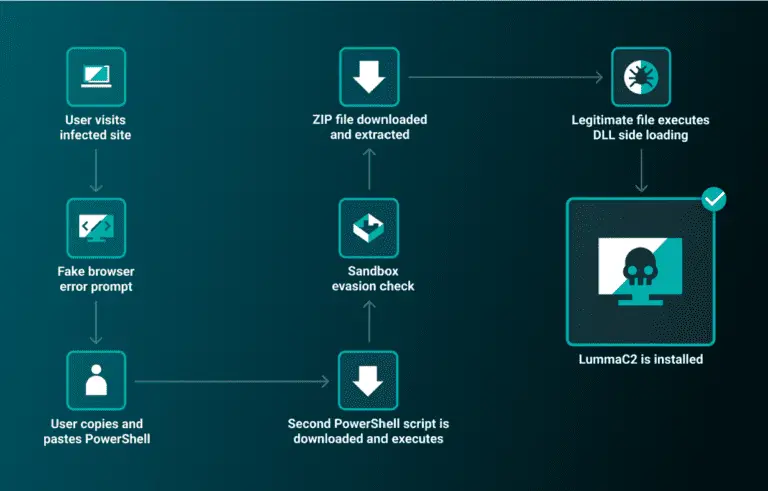
The ReliaQuest Threat Research Team has unveiled a new execution technique used in the ongoing ClearFake campaign

A report by CyberArk reveals a sinister trend: the rise of 'infostealer' malware specifically designed to steal web session cookies.

Central to Kimsuky's operations is AppleSeed, a backdoor malware that facilitates remote system control. It can execute commands