 Do Son
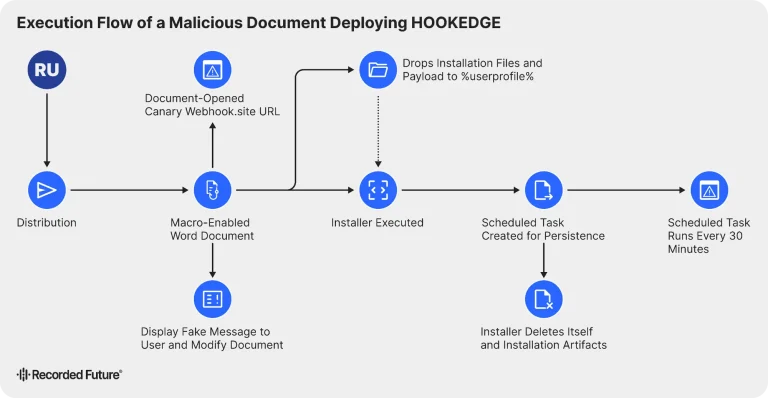
Insikt Group ties HOOKEDGE malware to Russian group BlueDelta (APT28), hitting EU diplomatic targets via webhook abuse and macro-enabled Word lures.
Insikt Group

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

Dabai Guarantee emerges as the new hub for Chinese cybercrime, using Telegram and "ghost-tapping" to coordinate global retail fraud and USDT money laundering.

Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.
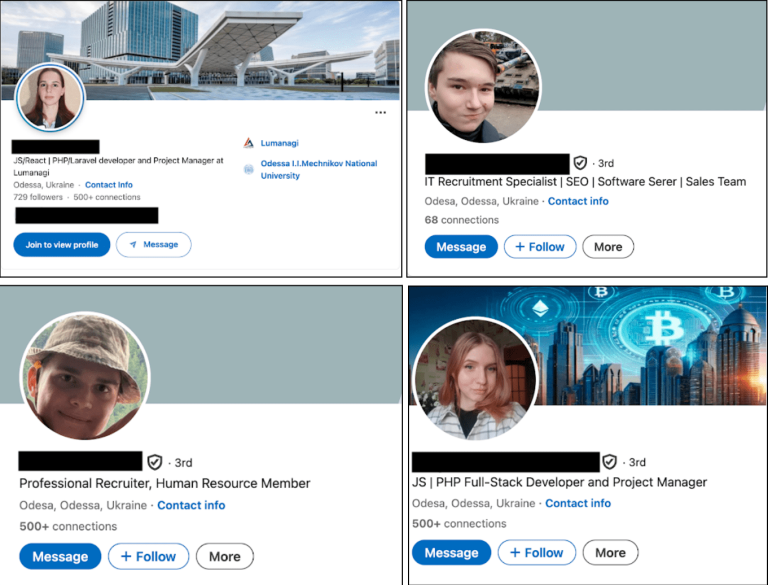
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

A new report reveals TAG-150, a sophisticated new threat actor with evolving malware and a resilient multi-tiered infrastructure, including a new RAT called CastleRAT.
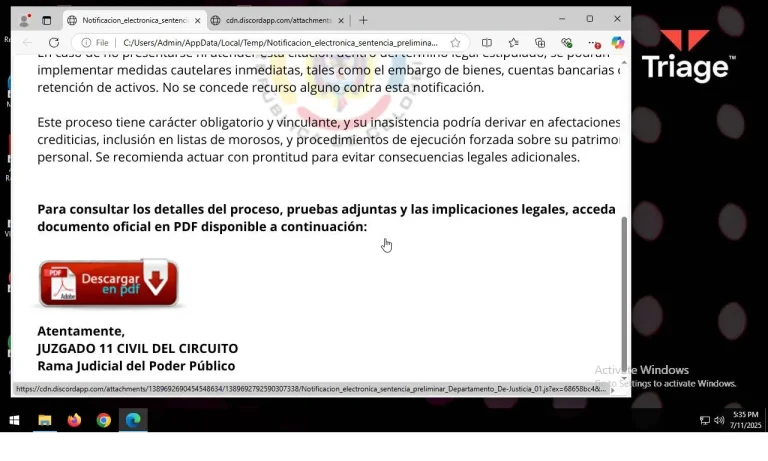
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.
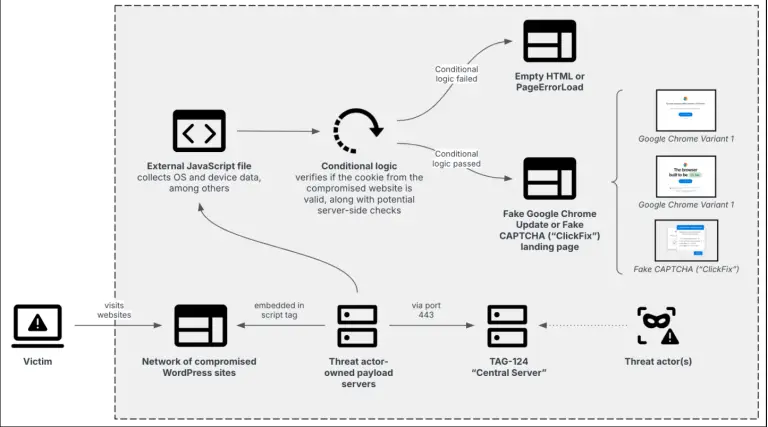
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Insikt Group reveals Predator spyware's resurgence, with new infrastructure, obfuscation, and a previously unreported customer in Mozambique, despite sanctions.