 Do Son
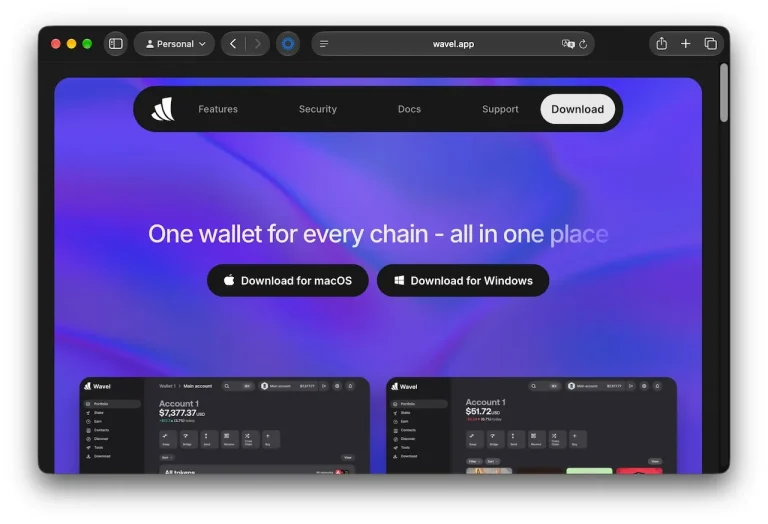
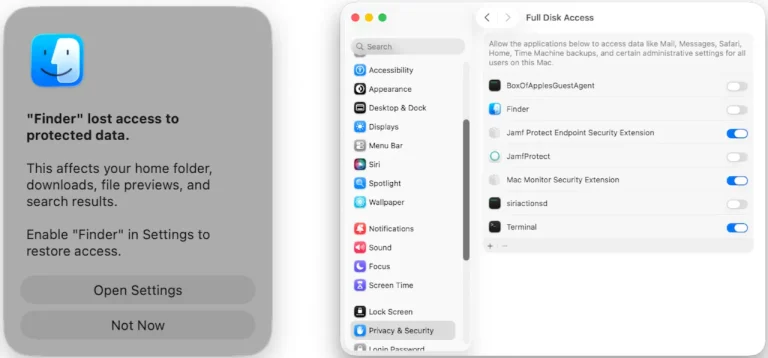
A new PamStealer macOS infostealer spreads via fake Wavel apps. Learn how the PamStealer macOS infostealer steals system passwords and browser data.
Jamf Threat Labs
Security teams uncovered trojanized fake macOS installers tied to North Korean campaigns that deploy OtterCookie malware on Apple devices.

A fake Zoom installer delivers Overlord RAT on macOS via a .NET downloader. Jamf Threat Labs details the infection chain and defenses.

CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.
PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.

Jamf reveals Predator spyware's advanced anti-analysis tactics. It now detects Corellium, hides recording icons, and tracks why infections fail.
Jamf uncovers a new MacSync Stealer variant that was notarized by Apple, allowing it to bypass Gatekeeper and infect Macs without terminal commands.
A new macOS backdoor, ChillyHell, bypassed Apple's notarization process for years, remaining undetected while being used for espionage and brute-force attacks.

Jamf Threat Labs has uncovered a sophisticated new macOS infostealer variant that managed to bypass Apple’s security defenses by leveraging valid code signing and notarization