
 Do Son
North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.
Kimsuky

Kimsuky APT is using HWP documents and stealthy AnyDesk backdoors in a new phishing campaign to infiltrate systems under the guise of academic collaboration.

Kimsuky's AppleSeed campaign targets Korean Facebook, email, and Telegram users with evolved social engineering and stealthy malware.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.

ASEC report details Kimsuky's Larva-24005 campaign targeting South Korea and globally with RDP exploits, MySpy malware, and keyloggers.

Explore the tactics of the North Korean APT group Kimsuky, also known as Black Banshee. Discover their latest attack strategies.
Uncover the dangers of DocSwap malware, a new threat from a North Korean APT group targeting mobile devices.
Explore the Kimsuky Watering Hole Attack targeting a South Korean university website. Learn about this new cybersecurity threat.

Explore the impact of South Korean cyberattack threats on civil society organizations and their defenders in a detailed study.
Uncover the tactics used by the North Korean APT group Kimsuky in their cyber espionage operations, including the use of the RDP Wrapper for persistent access.

Learn about the surge in sophisticated APT attacks targeting various sectors. ESET's report sheds light on tactics and VPN reliance.

Learn about the risks of DMARC misconfigurations and how they can be exploited by cybercriminals in spear-phishing campaigns.

Discover the growing threat of cybercriminals exploiting Extended Validation code signing certificates to deceive users and bypass security measures.

A key component of their infrastructure is a webshell dubbed “Green Dinosaur,” a modified version of the Indrajith Mini Shell 2.0

Learn about the escalating cyberattacks on South Korea's construction and engineering sectors and how cybercriminal groups are exploiting VPN vulnerabilities.

Discover how APT45 Andariel, a notorious North Korean hacker group, stole confidential information on weapon systems and technologies.

Rapid7 has released a comprehensive report detailing the evolving TTPs of the Kimsuky advanced persistent threat (APT) group

Japanese organizations are being targeted by the notorious North Korean advanced persistent threat (APT) group, Kimsuky
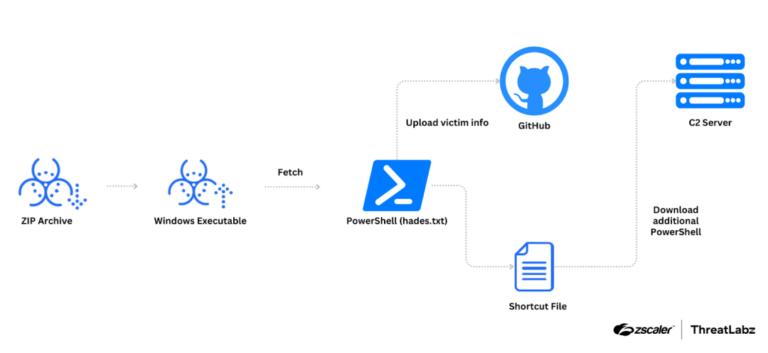
The group is deploying a malicious Google Chrome extension called "TRANSLATEXT" to steal sensitive information from South Korean academics

ASEC has disclosed a new cyberespionage campaign attributed to the North Korean state-sponsored group Kimsuky

Security researchers at QiAnXin Threat Intelligence Center have uncovered a sophisticated malware campaign waged by the Kimsuky APT group

Armed with a diverse arsenal of malware, including the notorious AppleSeed and AlphaSeed strains, Kimsuky's tactics have evolved