 Do Son
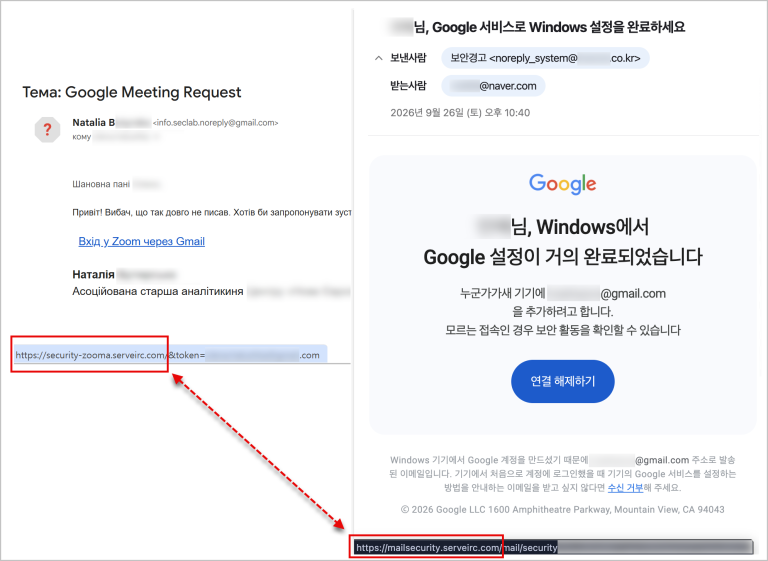
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
Kimsuky
Threat analysts reveal Kimsuky uses AI agent opencode to mass-produce phishing decoys. Discover how the group leverages AI to enhance its LNK attacks.
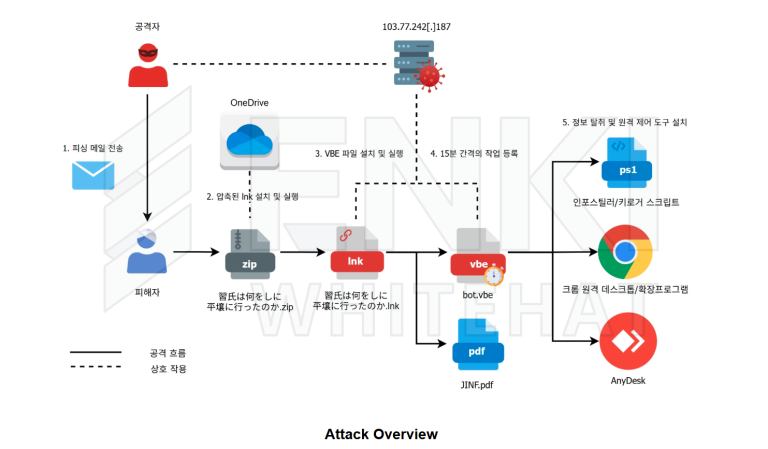
Recent Kimsuky spear phishing campaigns abuse remote control tools and AI extensions to target victims in Japan and South Korea. Read the full analysis.

Kimsuky AI operations reveal a North Korea threat actor testing local LLMs. Suspected state hackers are building new capabilities to automate phishing.

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.

Learn how the Kimsuky HttpSpy malware campaign leverages a novel JSONPing execution check to target South Korean networks and evade modern security.

Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.

A joint Hunt.io and Acronis report exposes the shared infrastructure behind Lazarus and Kimsuky, revealing the unified web of North Korean hacking.

Kimsuky is deploying a new DOCSWAP RAT via QR codes and smishing. The DPRK-linked malware turns phones into surveillance tools for data theft.

ENKI exposed a Kimsuky APT campaign using a dual PE/PowerShell payload that switches based on Windows Defender status to deploy KimJongRAT. The malware steals Chrome AppBound keys via GitHub Releases C2.

Kimsuky APT is using a Themes.js JavaScript loader and certutil LOLBIN to gain minute-by-minute persistence via a Windows Scheduled Task. The APT is targeting think tanks for espionage.

Gen Labs exposed Kimsuky deploying HttpTroy via fake VPN lures and Lazarus using an upgraded BLINDINGCAN RAT. Both North Korean APTs use DLL sideloading and custom crypto to evade analysis.

North Korean threat group Kimsuky is using AI-generated deepfakes in a new spear-phishing campaign, signaling a new frontier in cyber warfare.

A new report reveals that the North Korean Kimsuky APT is using social engineering on Facebook and Telegram to deliver AppleSeed malware to targets in South Korea.

A data leak from an alleged North Korean APT group's workstation has revealed its use of a commercial proxy service, offering a rare look into its anonymizing infrastructure.
A new report reveals a North Korean espionage campaign targeting embassies with spear phishing and a sophisticated C2 channel hidden on GitHub.
A state-sponsored North Korean hacking group was breached by "ethical" hackers. An 8.9GB archive of tools and stolen data has been leaked online.

A new report reveals Kimsuky, a North Korea-linked APT, is using sophisticated LNK files and reflective payloads to infiltrate systems and conduct cyberespionage against South Korean targets.

North Korean APT Kimsuky is evolving its ClickFix tactics, using deceptive social engineering, fake job portals, and obfuscated PowerShell to compromise targets via spear-phishing campaigns.