 Do Son
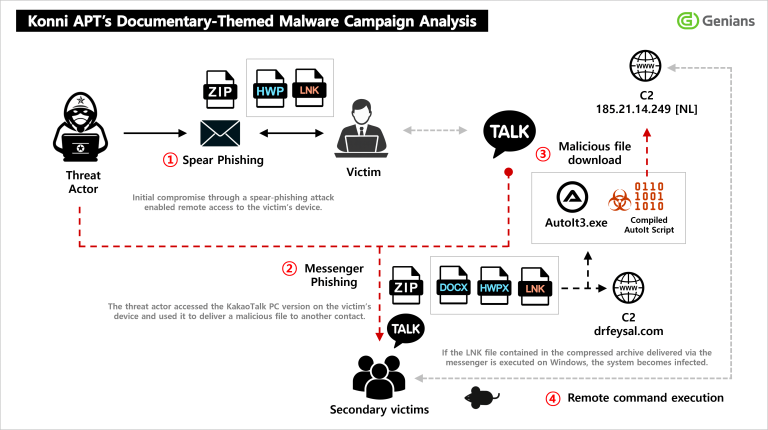
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.
KONNI APT

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

North Korea's KONNI APT is exploiting stolen Google accounts and the Find Hub service to remotely wipe South Korean Android devices for data destruction and surveillance, then spreading malware via KakaoTalk.