 Do Son
A critical Rancher XSS vulnerability tracked as CVE-2026-88804 exposes admin sessions. Update your clusters immediately to prevent system compromise.
Kubernetes Security

A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.

Read about new Jupyter Gateway vulnerabilities and critical CVSS 10 flaws that allow remote code execution and full Kubernetes cluster takeover.

Multiple Fleet security vulnerabilities expose private environments to cross namespace secret disclosure and SSRF attacks. Patch your systems now.

Multiple critical Rancher security flaws allow widespread cluster privilege escalation. Patch your Kubernetes container environments immediately.
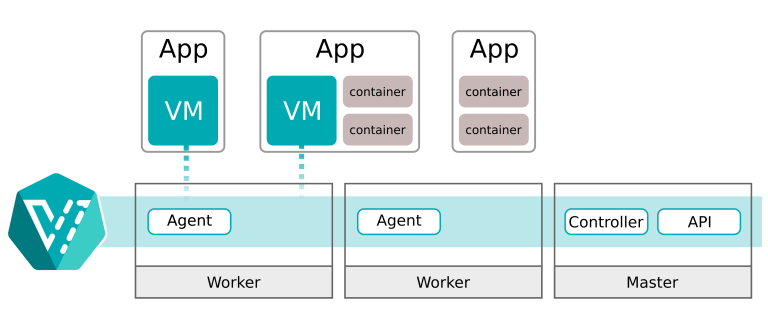
Discover how the critical KubeVirt privilege escalation flaw (CVE-2026-7374) allows container runtime hijacking and creates a cluster takeover risk.

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.

CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
Rancher Fleet fixes a 9.9 CVSS flaw (CVE-2026-41050) allowing tenants to bypass ServiceAccount isolation and steal secrets. Upgrade your GitOps engine now!
SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.

Cisco Talos reveals VoidLink, a modular Linux malware framework by UAT-9921. Features "compile-on-demand" tools to target IoT & cloud infrastructure.

Critical Kyverno flaw CVE-2026-22039 (CVSS 10) allows policy creators to gain cluster admin rights. Update to v1.16.3 to fix privilege escalation & DoS.

Critical External Secrets Operator flaw CVE-2026-22822 (CVSS 9.3) allows cross-namespace secret theft. Update to v1.2.0 now to secure your cluster.

New "cloud-first" malware VoidLink targets Linux & containers with advanced stealth. Written in Zig, it mimics Cobalt Strike to evade EDR. Check your cloud.

A critical chain of Fluent Bit vulnerabilities allows RCE, path traversal, and log tampering by exploiting tag handling and an auth bypass. Update to v4.1.1 now.

Rancher patches CVE-2024-22031, a privilege escalation flaw allowing cross-cluster access. Update to v2.11.1, v2.10.5, or v2.9.9 to stay protected.