
 Do Son
SentinelOne discovered how new TraderTraitor macOS backdoors hit IT firms. Learn how TraderTraitor macOS backdoors use weaponized Terraform files.
Lazarus
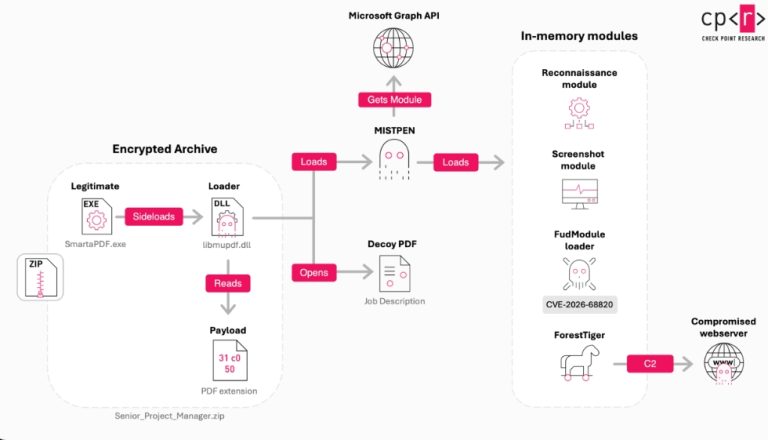
Lazarus exploited a Windows zero-day (CVE-2026-68820) in Operation Dream Job to hit defense firms with fake job offers and a new backdoor.
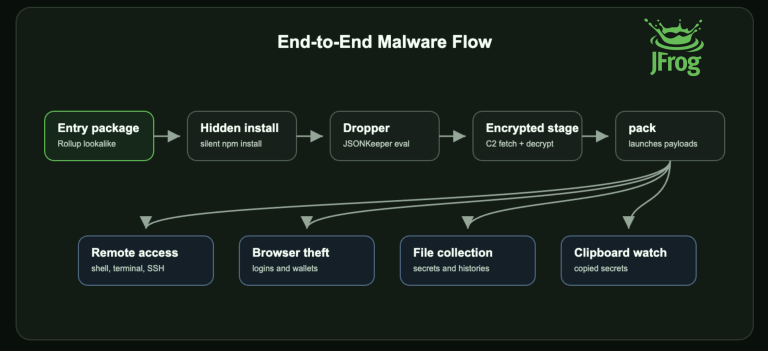
New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.

Learn about Lazarus Group's latest attack targeting cryptocurrency professionals. Discover how they weaponized a legitimate open-source project to steal sensitive information.

Stay informed about the latest cyber espionage tactics. Learn how the Lazarus group is targeting financial institutions with a weaponized IPMsg installer.

Discover how Kernel Callback Tables can be manipulated for process injection on Windows systems. Learn about the stealthy method employed by high-profile threat actors.

LilacSquid deploys a series of malicious tools, including MeshAgent, a customized version of QuasarRAT, dubbed "PurpleInk,"

CISA has added a critical Windows Kernel vulnerability (CVE-2024-21338) to its Known Exploited Vulnerabilities catalog

QiAnXin Threat Intelligence Center's detailed analysis linked the binary involved in this operation to a North Korean APT

Kaspersky Lab has unveiled a comprehensive analysis of the operations of Asian cyber espionage groups conducting espionage activities globally

Lazarus group, with its sophisticated methods and unwavering motivations, continues to be a formidable adversary in the digital realm

In mid-October 2019, security researchers discovered a significantly modified piece of malware, named the active cluster DeathNote