
 Do Son
LockBit 5.0 emerges with new "premium" criminal services. AhnLab analysis reveals how the top RaaS gang targets IT firms and churches alike.
LockBit

Yarix exposes the new Qilin-LockBit-DragonForce cartel. Is it a powerful merger or a desperate PR stunt for a "dead" LockBit? Find out.

GOLD SALEM (Storm-2603) is exploiting SharePoint via ToolShell then abusing the Velociraptor DFIR tool as a ransomware precursor. The group deploys Warlock and LockBit 3.0 variants, often targeting critical infra.

New 01flip ransomware (written in Rust) targets APAC critical infra across Windows/Linux. The attackers use Sliver for C2 and older exploits for access. A curious "lockbit" ignore list was found in the code.

Cisco Talos confirms Storm-2603 is abusing the DFIR tool Velociraptor for persistence and arbitrary code execution, deploying LockBit and Babuk ransomware against VMware and Windows servers.

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

Unit 42 reveals Project AK47, a toolkit used by Storm-2603 to exploit SharePoint. It includes a custom AK47C2 framework and links to both LockBit and Warlock ransomware.

Check Point Research uncovers Storm-2603, a China-linked APT using a custom AK47C2 framework and BYOVD tactics to deploy multiple ransomware strains simultaneously.

Symantec's report reveals LockBit is using evolved tactics, including DLL sideloading and process masquerading with legitimate executables, to evade detection and deploy payloads.

Splunk uncovers XWorm's evolution: a modular RAT now delivering LockBit ransomware. It uses flexible delivery, AMSI/ETW bypasses, and process injection to evade detection.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."
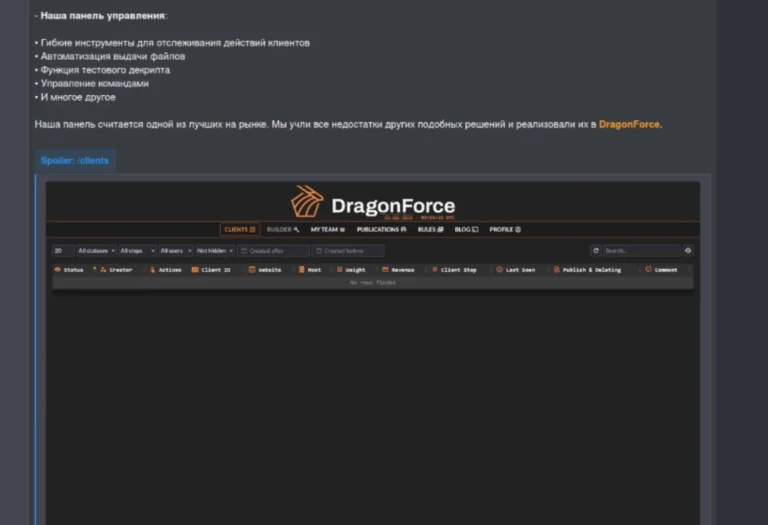
DragonForce ransomware cartel targets UK retailers with Conti-based payloads, RansomBay leaks, and phishing attacks, warns SentinelOne report.

Explore the features and threats of LockBit 4.0, the latest evolution in ransomware that impacts organizations globally.
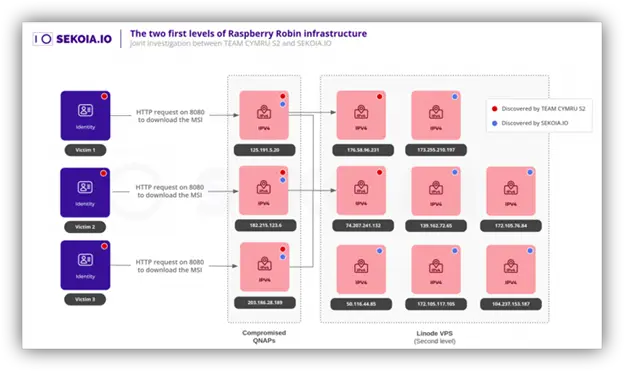
Explore the evolution of Copy Shop Worm into a sophisticated threat linked to cybercriminals and state-sponsored actors.
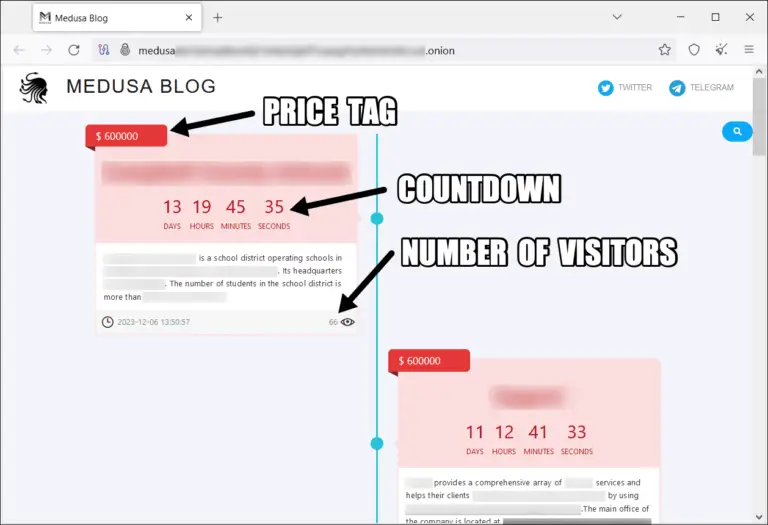
Explore the rise of Medusa ransomware attacks, increasing by 42%. Understand the threat and protective measures you can take.

Uncover the details about SafePay ransomware: a stealthy and sophisticated strain with ties to known families like LockBit.

Discover the hidden threats of ransomware abusing AWS S3 infrastructure. Explore the tactics used by this sophisticated operation to steal sensitive data.

Europol's landmark operation against LockBit ransomware: key individuals arrested, critical servers seized in a coordinated crackdown.
Learn how the United Kingdom is taking action against Evil Corp, a notorious cybercrime group linked to the Russian state and other ransomware groups.

Uncover the latest cyber threats targeting the European Union. From DDoS attacks to ransomware, gain insights into the challenges faced by the EU.
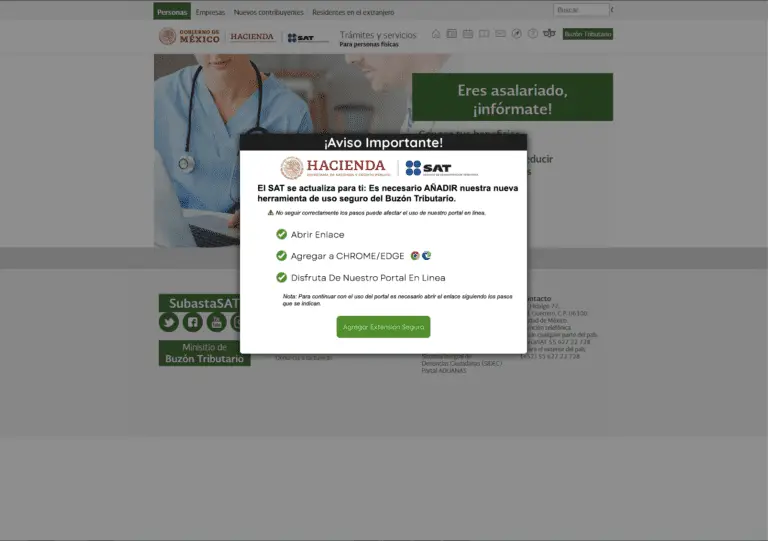
Uncover the growing cyber threats faced by Mexico: a targeted mix of global espionage and local cybercrime affecting both users and enterprises.

Dark Angels group sets record ransom payment of $75 million, causing concern for cybersecurity experts and organizations worldwide.