
 Do Son
A High-severity flaw in macOS PackageKit bypasses a previous fix. Exploiting the user's .zprofile file allows a local attacker to easily gain root privileges.
LPE

A Critical (CVSS 9.3) LPE flaw in cPanel's Team Manager API allows a standard user to break out of their directory via path traversal and compromise the shared hosting server. Update immediately.

ASUS urges users to patch a high-severity LPE flaw (CVE-2025-59373) in its System Control Interface Service, which allows low-privileged users to escalate to full SYSTEM control.

Elastic patched two local privilege escalation flaws (CVE-2025-0712, CVE-2025-25011) in APM Server and Beats for Windows, allowing local attackers to gain SYSTEM privileges.

A critical privilege escalation flaw (CVE-2025-6241) in Lakeside Software's SysTrack allows low-privileged local users to gain SYSTEM access via DLL hijacking. Patch immediately.

Sophos has patched three high-severity LPE vulnerabilities in Intercept X for Windows (CVE-2024-13972, CVE-2025-7433, CVE-2025-7472), allowing local users to gain SYSTEM privileges.

A Windows Update flaw (CVE-2025-48799) allows SYSTEM privilege escalation via arbitrary folder deletion using symlinks on multi-drive systems. PoC available. Patch now!

A high-severity flaw (CVE-2025-6020) in Linux PAM's pam_namespace allows unprivileged users to gain root via symlink attacks and race conditions.
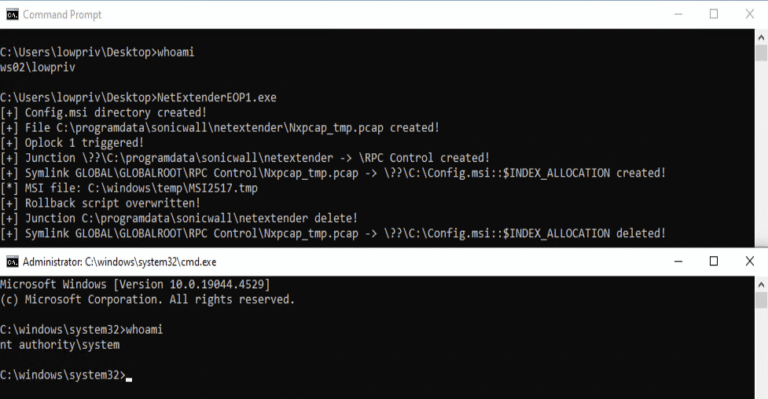
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.