 Do Son
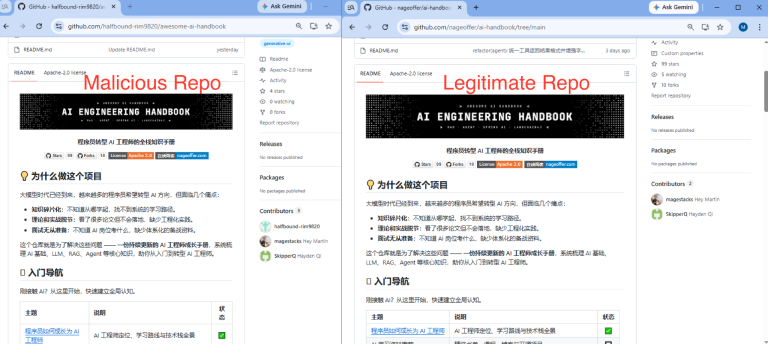
Fake AI tools malware targets developers in a GitHub infostealer campaign using SmartLoader and blockchain C2. See how it works.
MaaS
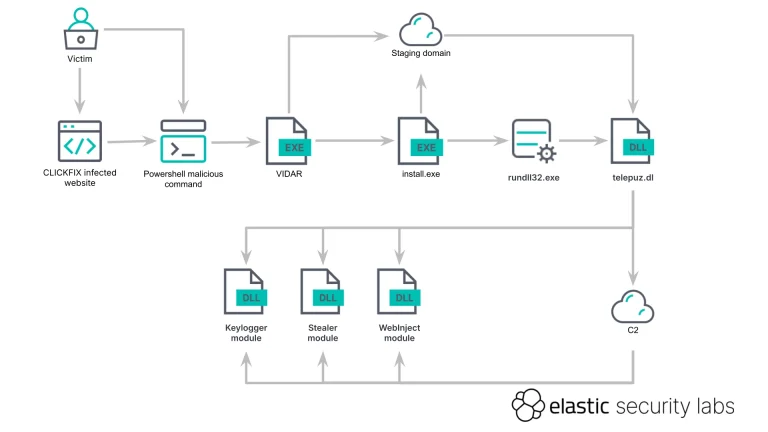
Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.
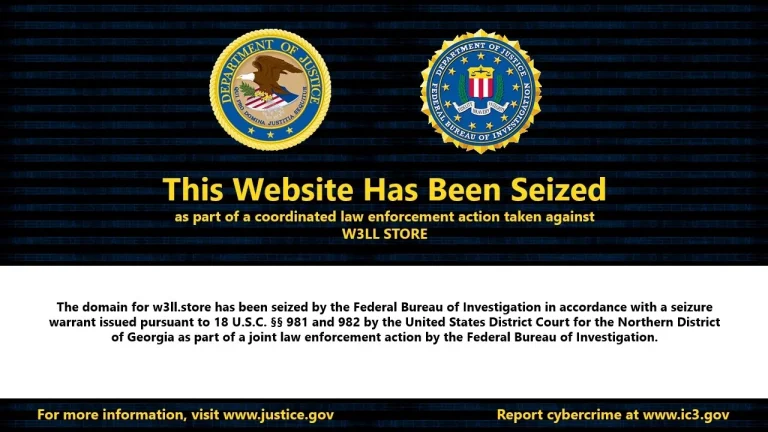
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.
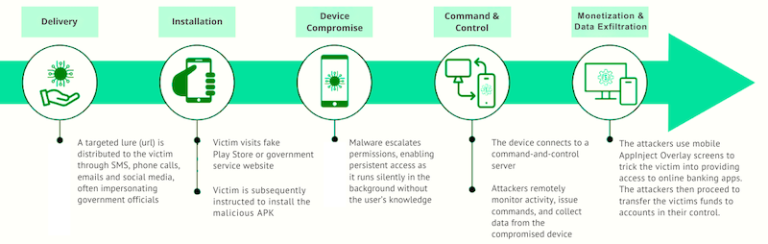
Infoblox uncovers the K99 compound: a brutal MaaS operation using human trafficking to power biometric hijacking and global Android banking fraud.
Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.
Storm malware bypasses Chrome security by shipping encrypted files for server-side decryption. Learn how it steals session cookies to defeat MFA in 2026.
Venom Stealer is a new C++ MaaS targeting crypto wallets like Tonkeeper. It features silent UAC elevation and Chrome encryption bypass. Learn how to defend.
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!
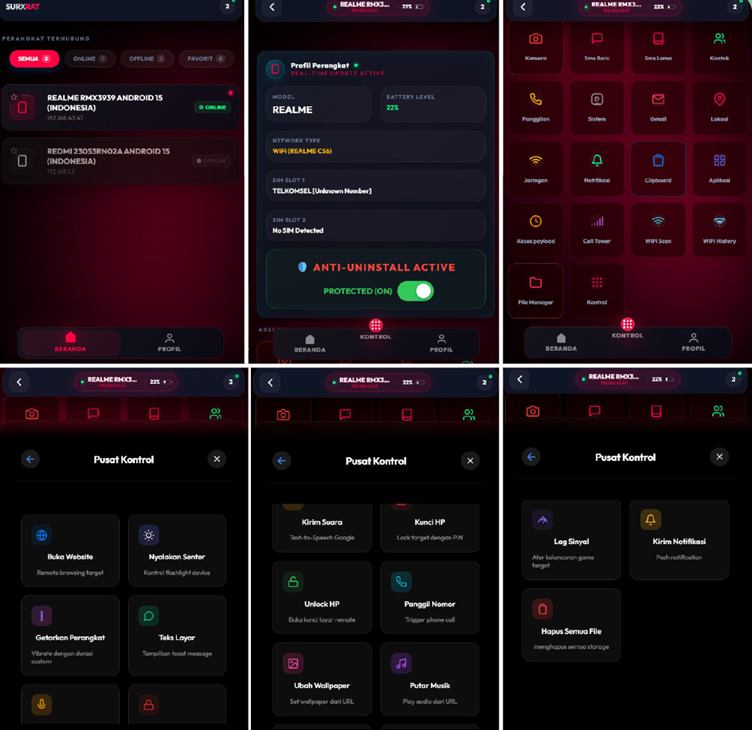
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
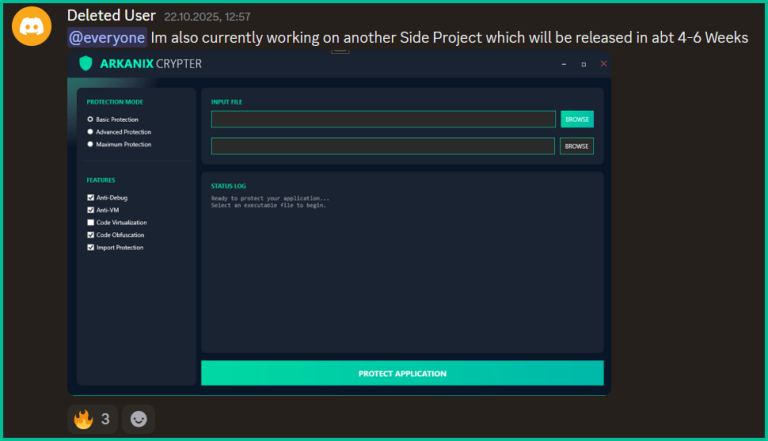
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
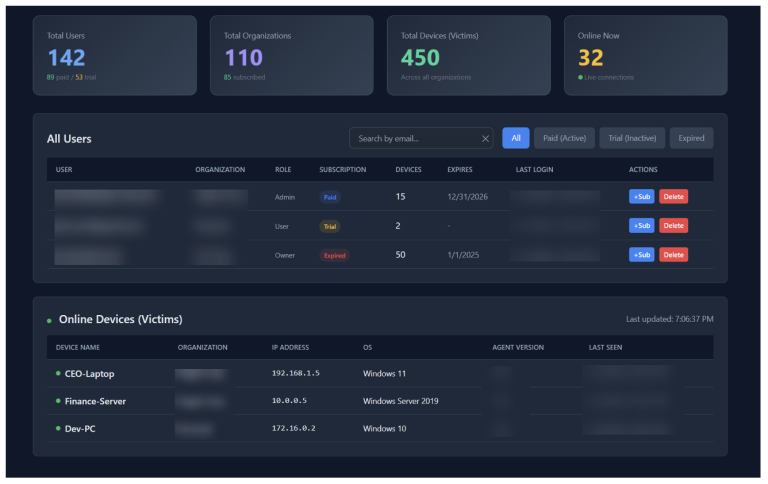
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

SantaStealer, a new MaaS info-stealer, is being aggressively marketed on the dark web. It's a BluelineStealer rebrand that uses C code and open-source libraries to steal crypto wallets and credentials, despite having amateur anti-analysis features.

Frogblight, a new Android banking Trojan, is targeting Turkey via smishing with fake e-government apps. It uses WebView to steal credentials and is linked to the Coper MaaS family. It is being actively developed.

GrayBravo MaaS uses CastleRAT to target logistics/hospitality. The RAT hides its C2 by using Steam Community profiles as Dead Drop Resolvers, bypassing network monitoring.

Zscaler exposed Matanbuchus v3.0, a MaaS downloader pivoting to ransomware. The stealthy C++ malware uses Protobufs for C2, QuickAssist for access, and time-wasting loops to bypass sandboxes.

Meet Albiriox, a new Russian Android banking Trojan sold as a service. Learn how its "AcVNC" tech enables on-device fraud against 400+ global apps.

Darktrace exposed TAG-150, a new MaaS operator compromising 469+ US devices in months. The group uses ClickFix to trick victims into running malicious PowerShell that deploys the CastleLoader/CastleRAT backdoor.

Zimperium exposed Fantasy Hub, a Russian MaaS Android RAT. It uses a Telegram bot for subscriptions and WebRTC to covertly stream live video and audio, targeting Russian banks with dynamic overlays.

Sekoia exposed a campaign exploiting compromised Booking.com/Expedia accounts to deliver PureRAT malware via a ClickFix lure. Attackers use authentic reservation details to steal guest credentials.

A sophisticated Lumma Infostealer MaaS campaign targets users with pirated software installers. It uses NSIS/AutoIt scripts, Process Hollowing, and MEGA cloud to steal credentials from browsers and crypto wallets.