 Do Son
PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.
macOS security
Discover why Apple is restricting Full Disk Access for macOS AI agents like Meta Muse to protect user privacy and secure the operating system sandbox.

Learn about the critical OpenVPN Connect macOS vulnerability (CVE-2026-9560) that allows local privilege escalation, and how to patch it now.

OpenAI rotates code signing certificates following the TanStack npm breach. macOS users must update ChatGPT and Codex manually before June 12, 2026.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
OpenAI revokes legacy macOS certificates after a malicious @Axios library incursion. Update ChatGPT and Codex by May 8, 2026, to avoid software failure.

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.
Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
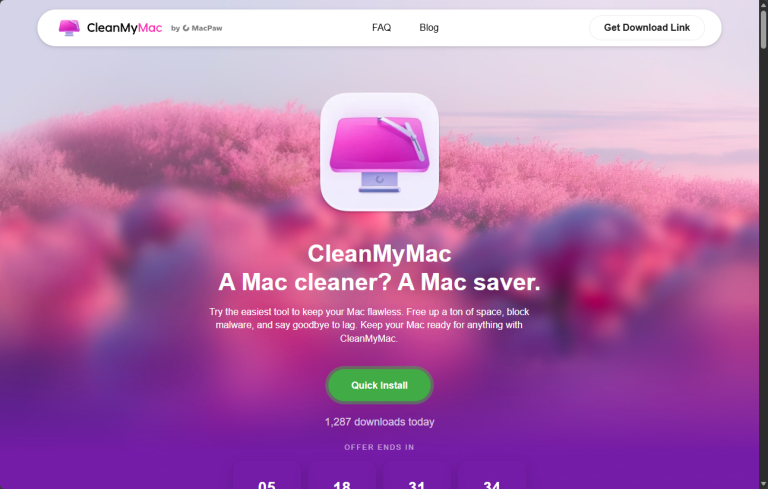
A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.

GlassWorm Wave 4 targets macOS developers via VS Code, using encrypted payloads and a 15-minute fuse to trojanize Ledger and Trezor wallet apps.

A flaw (CVE-2025-4232) in GlobalProtect for macOS allows local users to escalate to root. Public PoC code exists. Update now!