 Do Son
Google restructures its Chrome VRP rewards, raising baseline payouts for memory corruption bugs to $2,000 and offering up to $20,000 for critical exploits.
memory corruption
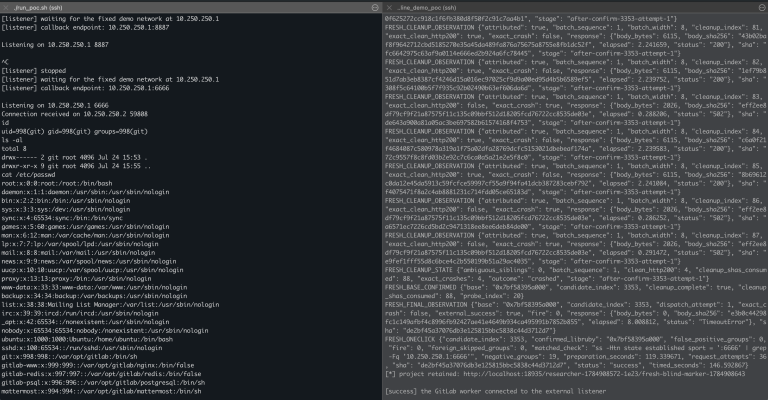
Public PoC exploits a GitLab RCE built from two Oj memory corruption bugs. See affected versions and patched GitLab releases to install now.
MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.

SAP Security Patch Day July 2026 fixes CVE-2026-44747 (CVSS 9.9), a memory corruption flaw in NetWeaver AS ABAP, plus two more critical bugs.

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.
Install the new Google Chrome security update today. This release delivers 151 critical security fixes to patch severe memory bugs.

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Redis releases critical patches for 5 vulnerabilities, including RCE via the RESTORE command (CVSS 7.7). Secure your self-managed Redis instances immediately!
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.

Google warns that CVE-2026-5281 is currently being exploited in the wild. Update Chrome to version 146.0.7680.177 immediately to fix this high-severity flaw.

Researchers reveal critical RCE and ARM-specific flaws in libpng (CVE-2026-33636 & 33416). Affecting decades of apps, these bugs require an immediate update.

Google patches Chrome zero-day CVE-2026-2441, an actively exploited memory flaw. With PoC exploit code now publicly disclosed, update to v145 immediately.

CVE-2025-13151: A one-byte overflow in GNU libtasn1 risks memory corruption during cert parsing. Patch now to secure your cryptographic applications.

MediaTek's Jan 2026 bulletin reveals critical modem flaws and memory corruption risks across dozens of chipsets. Update your device to stay safe!

Apache NuttX patches a moderate Use After Free (CVE-2025-48769) and a DoS flaw in its filesystem. Network-exposed devices must upgrade to v12.11.0.

NIST warns of a critical Exim 4.99 flaw. A failed SQLi patch allows attackers to poison SQLite records and trigger a 1.5MB heap buffer overflow.

WatchGuard warns of an active CVSS 9.3 zero-day (CVE-2025-14733). Attackers are exploiting IKEv2 VPNs for root RCE. Patch and rotate secrets now!

Google released an urgent Chrome update to patch High-severity flaws in WebGPU and V8. Fixes include a Use-After-Free and Memory Corruption. Update to v143.0.7499.146+ now.