
 Do Son
Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.
Microsoft Entra ID
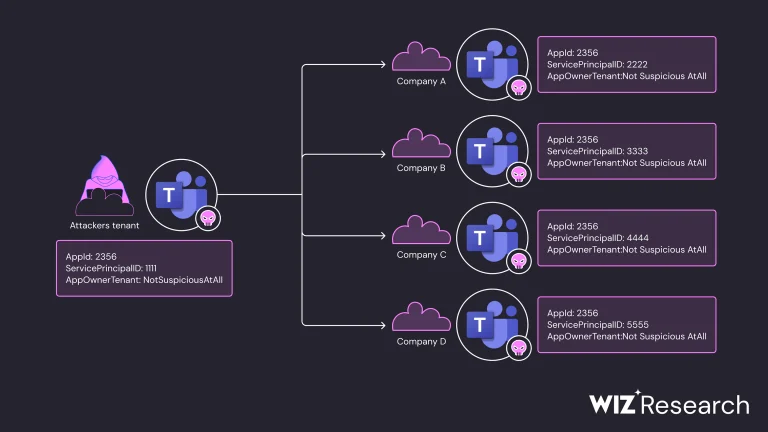
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
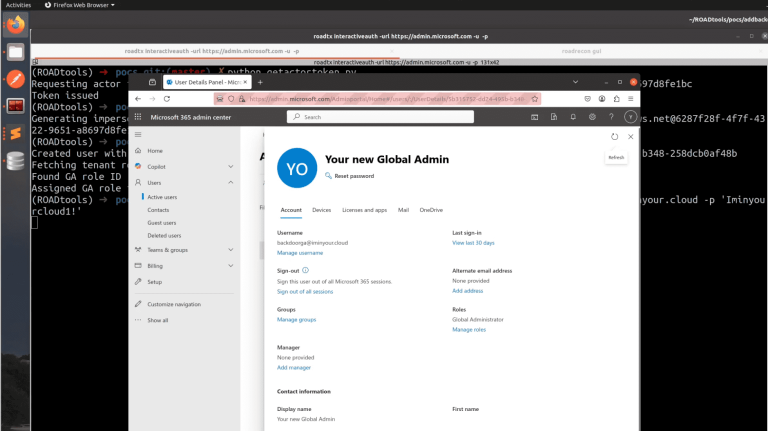
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."

TeamFiltration is being actively exploited in UNK_SneakyStrike, targeting over 80,000 Microsoft Entra ID accounts with password spraying and data exfiltration.

Discover the risks of Microsoft Entra ID's cross-tenant synchronization feature and how threat actors are using it for lateral movement attacks.

Learn about a potential security risk in Microsoft Entra ID and how malicious actors can establish persistent backdoor access within a compromised tenant.