 Do Son
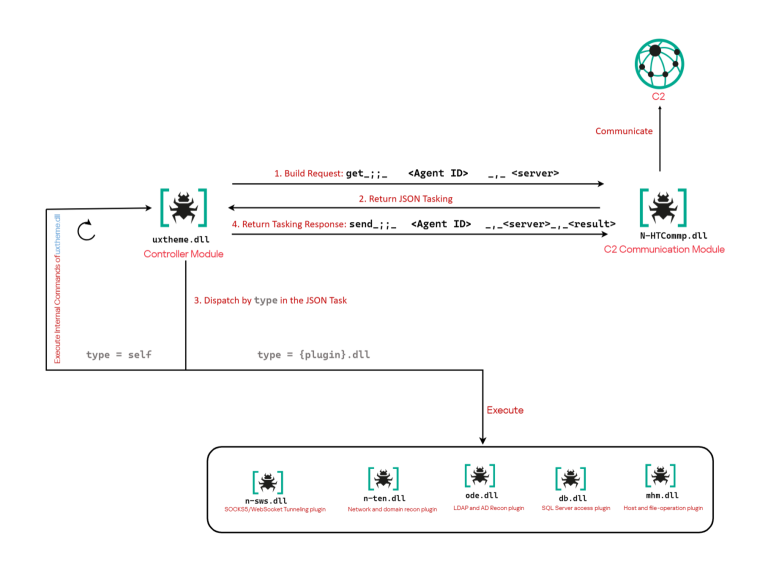
Kaspersky details Project CAV3RN, an OilRig-linked cyberespionage framework. Its new module hides C2 in Outlook calendar events, with DNS AAAA fallback.
Microsoft Graph
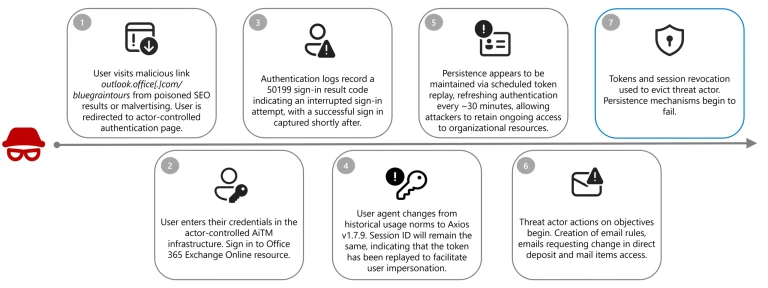
The active Payroll Pirate campaign uses AiTM session hijacking and token replay to target corporate payroll and HR personnel across multiple industries.
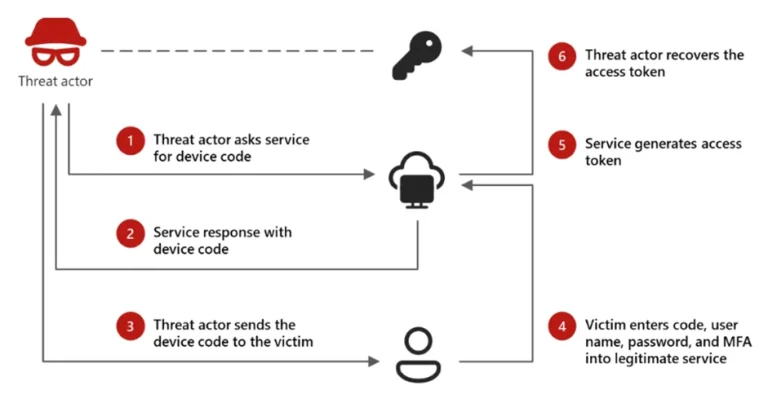
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!

Lab52 exposed Lazarus Group using DreamLoader malware via fake job lures. The modular tool chain abuses DLL sideloading and the Microsoft Graph API for stealthy C2 communications.

A new report reveals a dangerous misconfiguration: exposed appsettings.json files can contain Azure AD credentials, giving attackers full access to a company's cloud kingdom.

Over 50,000 Microsoft Azure AD user records from the aviation industry were exposed due to a misconfigured, unauthenticated API, revealing sensitive data and posing major risks.