 Do Son
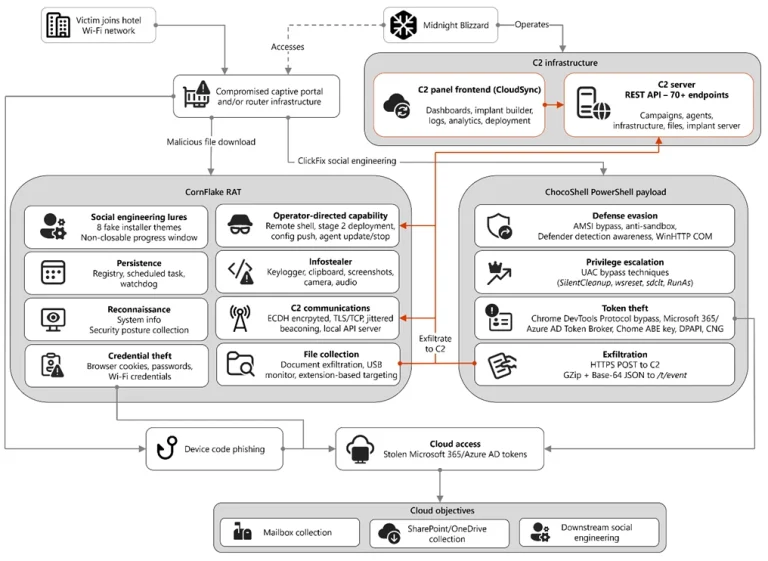
CaptiveCrunch malware campaign hijacks hotel Wi-Fi captive portals worldwide. Microsoft ties Storm-2945 to Midnight Blizzard, Russia SVR-linked group.
Midnight Blizzard

Amazon has disrupted a watering hole campaign by Russia's APT29. The hackers used compromised sites to trick users into authorizing attacker-controlled devices via Microsoft.

Explore the risks of Device Code Authentication phishing targeted at Microsoft 365 users by Russian threat actors.

Beware of the latest RDP phishing attack orchestrated by a Russian state-sponsored threat actor. Learn how to protect yourself from this targeted spear-phishing campaign.

Stay informed and protected from Russian cyber operations with this Joint Cybersecurity Advisory released by the NSA, FBI, CNMF, and NCSC.

TeamViewer, a remote control tool trusted by millions of users globally, has disclosed a significant cyberattack.

The French National Cybersecurity Agency (ANSSI) has issued a warning about the continued activity of the Nobelium intrusion set

Using info mined from the stolen data, Midnight Blizzard gained access to Microsoft's internal systems, including sensitive source code

Midnight Blizzard employed a password spray attack to breach a legacy non-production test tenant account within Microsoft's corporate systems

APT29 orchestrated a malicious campaign employing counterfeit BMW advertisements, the Ngrok tool, and exploiting a vulnerability in WinRAR