
 Do Son
GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.
mimikatz
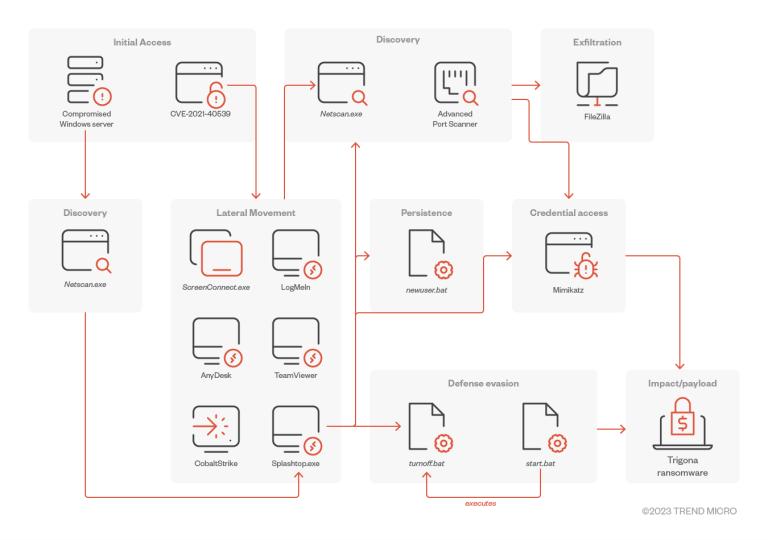
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.
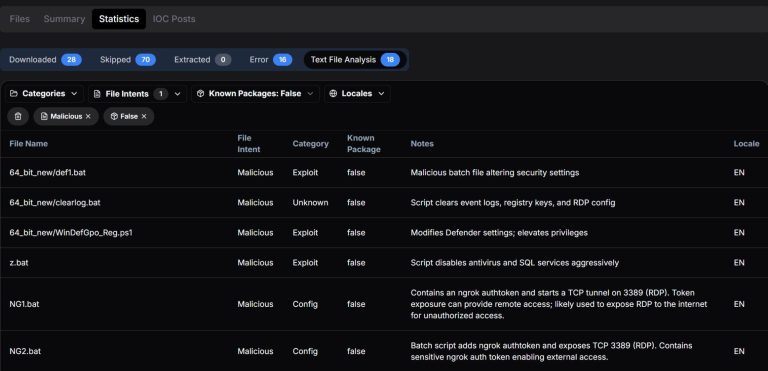
Hunt.io uncovers a Gentlemen ransomware toolkit on a bulletproof host. Learn how the z1.bat script destroys defenses and backups before encryption.

A six-day RansomHub attack exploited RDP, used Atera/Splashtop RMM, Mimikatz, and Rclone to breach an enterprise, exfiltrate data, and deploy ransomware.

Explore the new Betruger backdoor used by RansomHub affiliates in ransomware attacks. Discover its unique functionalities.

Learn about the recent campaign by Helldown ransomware group targeting Zyxel devices and the vulnerabilities exploited.

Learn about the collaboration of Play ransomware with the Andariel group. Explore the tactics used in this sophisticated cyber attack.
Learn about OilRig, also known as APT34 or Helix Kitten, and its sophisticated cyber espionage activities in the Middle East.

Discover the cybercrime group Ignoble Scorpius and their sophisticated ransomware campaign, BlackSuit, targeting industries worldwide.

Discover the alarming collaboration between North Korean hackers and ransomware gangs. Learn how Jumpy Pisces is involved in a Play ransomware attack.

Learn about Crypt Ghouls, a cybercriminal group behind ransomware attacks. Find out how they operate and how to defend against them.