 Do Son
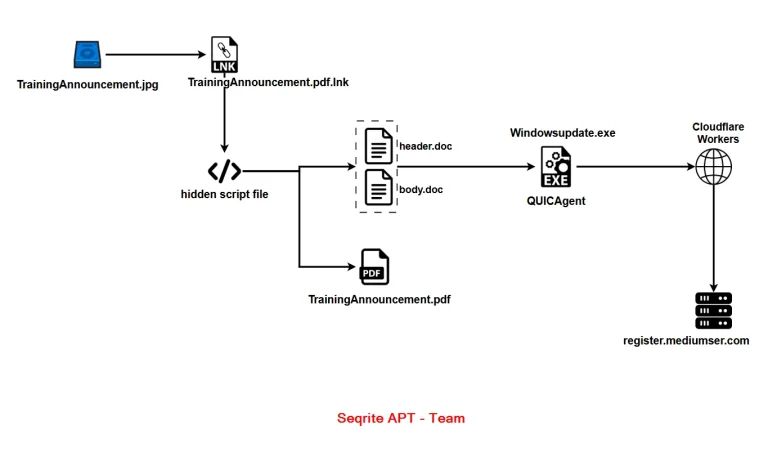
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
Myanmar

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

APT SideWinder launched Operation SouthNet, targeting South Asia with over 50 malicious phishing portals hosted on Netlify and pages.dev to steal government and military credentials.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.