
 Do Son
A fake Zoom installer delivers Overlord RAT on macOS via a .NET downloader. Jamf Threat Labs details the infection chain and defenses.
.NET malware
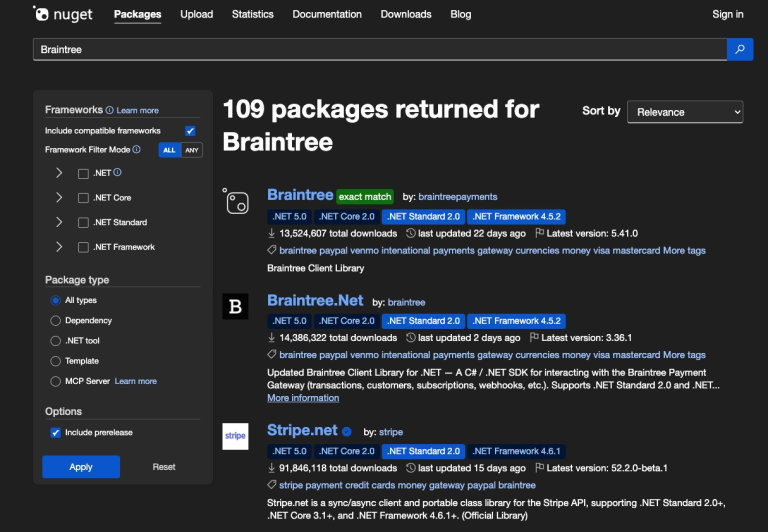
A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.
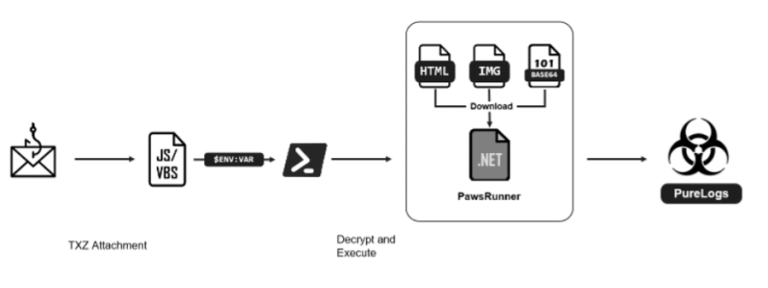
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
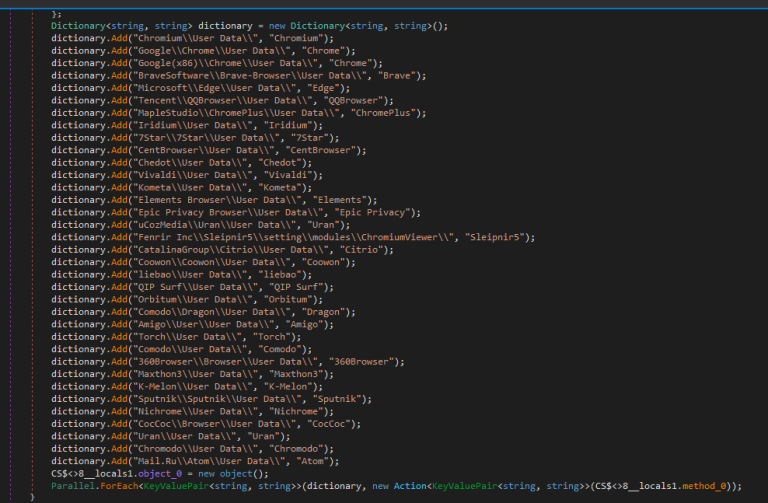
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

Ashen Lepus (Hamas-APT) significantly evolved during the conflict, deploying the AshTag modular .NET malware suite. It uses in-memory execution and Rclone for stealthy cyber-espionage against diplomatic targets in the Middle East.

Chihuahua Stealer uses stealthy PowerShell loaders, CNG AES-GCM encryption, and .NET memory injection to exfiltrate browser and crypto wallet data.