 Do Son
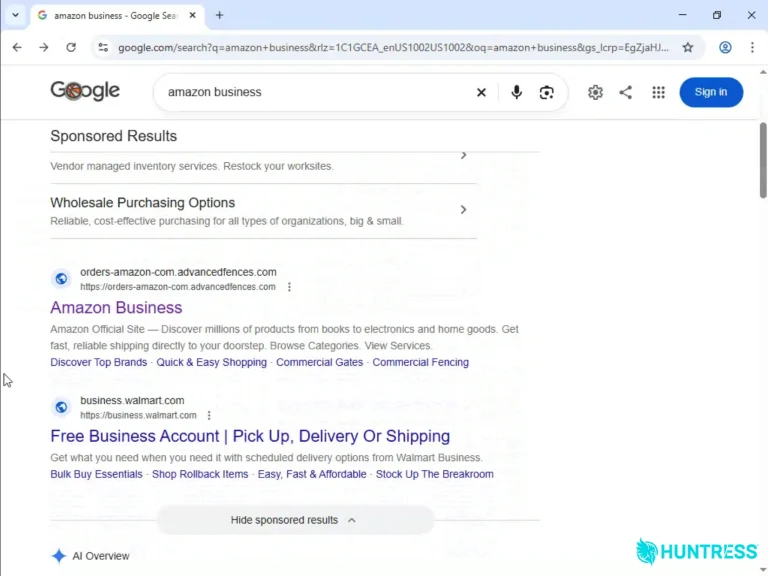
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
NetSupport RAT

CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.
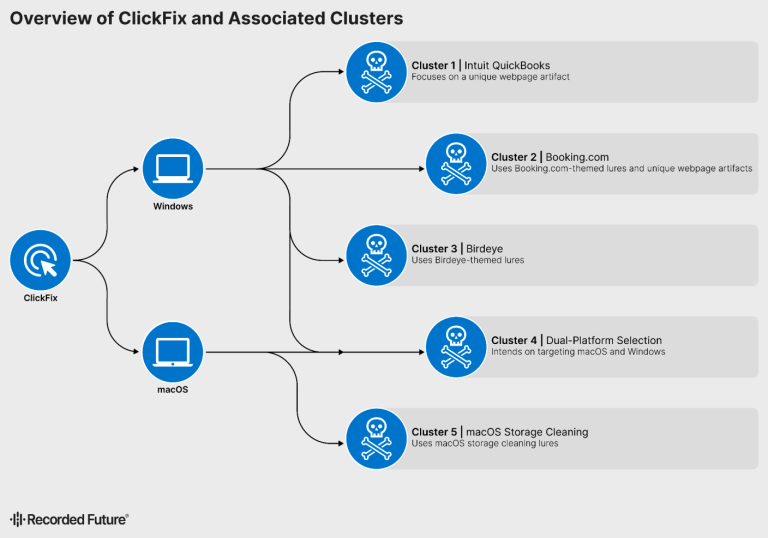
ClickFix has evolved into a high-ROI malware template used by APT28. Learn how this social engineering trick bypasses security by mimicking system errors.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

Sophos CTU reveals how the ClickFix tactic led to a Qilin ransomware attack via NetSupport RAT and StealC V2 using stolen VPN credentials.

The JS#SMUGGLER campaign uses "Junk Code" JavaScript and fileless PowerShell executed via mshta.exe to bypass EDR. This multi-stage attack silently installs the NetSupport RAT.

Bloody Wolf APT is targeting Central Asia using custom Java droppers to deploy the NetSupport RAT. The group uses geo-fencing and fake Ministry of Justice lures to achieve stealthy, persistent access for espionage.

eSentire exposed the Amatera Stealer campaign using ClickFix social engineering to deliver multi-stage PowerShell. The malware patches AMSI in memory and deploys NetSupport RAT for remote access.
NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access

NetSupport RAT Campaign Abuses ClickFix to Infect Hosts; 3 Threat Clusters Use RMM for Covert Access
eSentire exposed a surge in NetSupport RAT campaigns using the ClickFix social engineering tactic. Three threat clusters leverage a PowerShell loader to bypass AV and gain full remote access via the RMM tool.
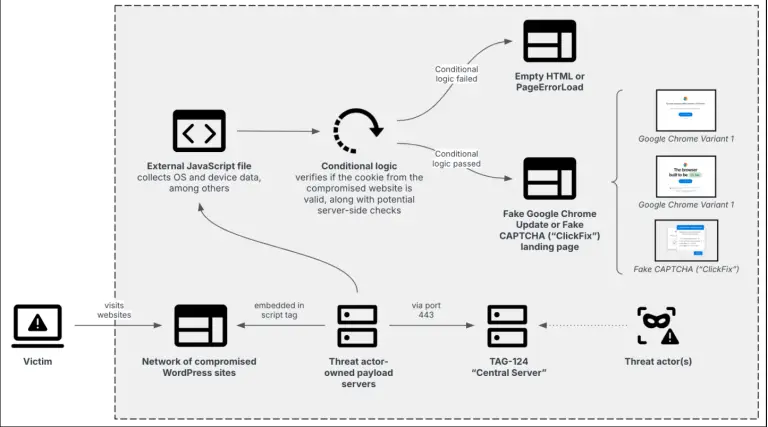
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.
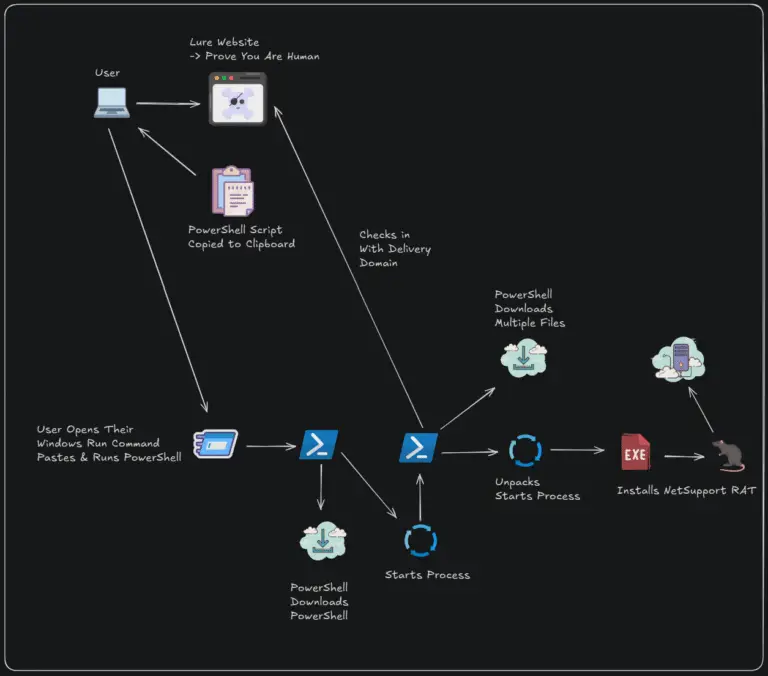
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

Stay informed about Booking Phishing schemes. Discover how attackers use social engineering to steal credentials in this campaign.

Beware of a new malvertising campaign using fake Cisco AnyConnect installers. Learn how attackers are distributing the NetSupport RAT Trojan.

Uncover the intricate web of the SmartApeSG FakeUpdate campaign and its connections to NetSupport RAT and other malicious threats.

Explore the BurnsRAT and NetSupport RAT used in the Horns&Hooves campaign. Dive into the details of this cybercriminal operation targeting individuals and businesses

Forensic investigations by Rapid7 have linked these activities to the Black Basta ransomware group, known for its disruptive cyber attacks

A sophisticated new malware campaign dubbed "PhantomBlu" is on the prowl, preying on US-based organizations

NetSupport RAT most commonly infiltrates a victim’s system through deceptive websites and bogus browser updates.