 Do Son
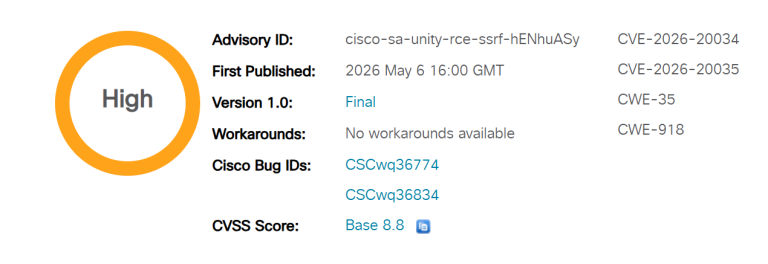
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
network-security

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

SonicWall discloses critical SonicOS flaws (CVE-2026-0204) hitting Gen6 to Gen8 hardware. Apply the 2026 firmware patch now to prevent unauthorized access.

Apache MINA (CVE-2026-41635) suffers a critical 9.8 CVSS RCE flaw. Learn how a deserialization filter bypass puts servers at risk and how to patch today.

Unpatched CVE-2026-5756 in DRC INSIGHT allows unauthenticated hijacking of student exam responses and traffic manipulation. Secure your school's network now.

OVN reveals two critical heap over-read flaws in ICMP and DHCPv6 processing. Learn how crafted packets can siphon sensitive memory and find the patch versions.

Industry stakeholders submit the IPv8 draft to the IETF. Discover how its 64-bit address space and 100% IPv4 backward compatibility aim to end address exhaustion.

Microsoft hardens RDP in the April 2026 update. Discover how new default isolation policies and security warnings stop malicious servers from stealing your data.
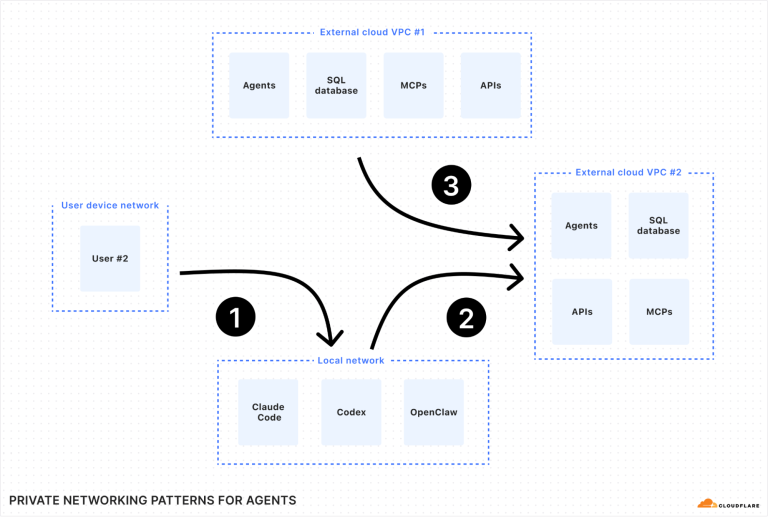
Cloudflare Mesh is here. Discover how this post-quantum encrypted network secures AI agents and infrastructure, offering a 50-node free tier to rival Tailscale.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
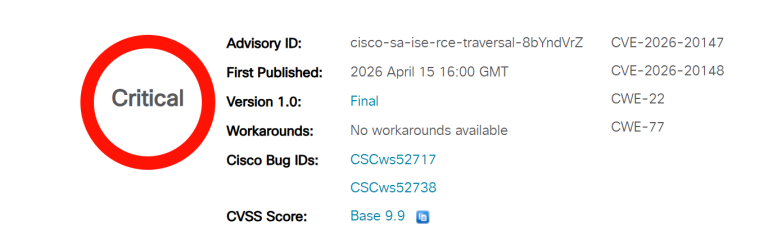
Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
Ubiquiti fixes critical 9.8 CVSS RCE flaws in UniFi Play PowerAmp and Audio Port. Don't let attackers control your sound—update your firmware immediately.

Juniper warns of a critical 9.8 CVSS flaw in JSI vLWC. A default password allows unauthenticated attackers to take full device control. Update to 3.0.94 now!

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

ASUS issues an emergency 8.5 CVSS patch for routers (CVE-2025-15101). A CSRF flaw lets attackers hijack sessions and change settings. Update your firmware today!

strongSwan fixes a high-severity DoS flaw (CVE-2026-25075) in eap-ttls. Unauthenticated actors can crash VPN gateways. Patch now to stay protected!

Cisco alerts of public flaws in IOS XE. Authenticated users can trigger a network-wide DoS or escalate privileges via the Lobby Ambassador API. Patch now.

Cisco alerts of public flaws in IOx app hosting. Unauthenticated actors can manipulate logs (CVE-2026-20113), plus a stored XSS risk (CVE-2026-20112). Patch now!
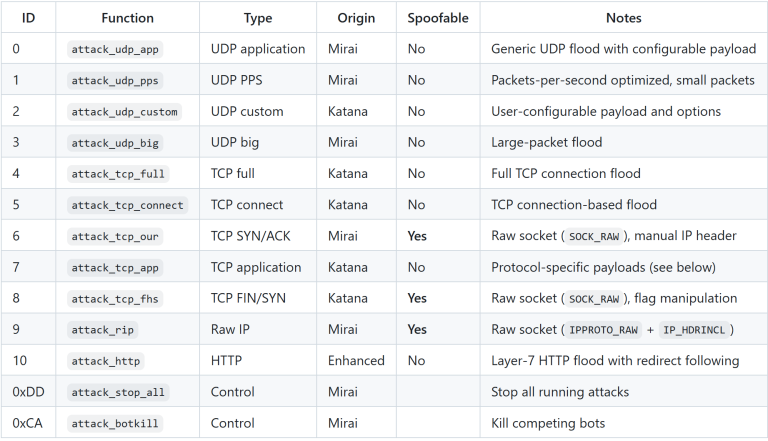
Nokia researchers uncover the Katana botnet, a Mirai variant using custom rootkits to hijack unmanaged Android TV boxes in a massive IoT turf war.

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.

Arctic Wolf warns that hackers are actively exploiting a critical Quest KACE vulnerability (CVE-2025-32975) to completely take over enterprise networks.
Ubiquiti warns of a critical 10.0 CVSS Path Traversal flaw (CVE-2026-22557) in UniFi Network Applications allowing total system takeover. Patch immediately.