
 Do Son
SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.
network-security
A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.
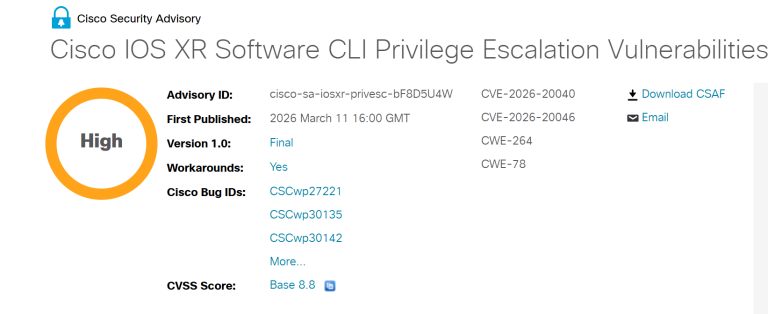
Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

Cisco warns that two vulnerabilities (CVE-2026-20122 and CVE-2026-20128) in its Catalyst SD-WAN Manager are being actively exploited. Update immediately.

Centreon issues urgent patches for a 9.9 CVSS path traversal and a 9.1 RCE vulnerability in CLAPI. Secure your monitoring infrastructure—update now!

NVIDIA warns of three high-severity vulnerabilities (CVE-2025-33179, 33180, 33181) in Cumulus Linux. Low-privileged users can escalate to admin control.

Juniper Networks warns of a critical 9.8 CVSS root vulnerability (CVE-2026-21902) in PTX Series routers. Unauthenticated attackers can gain complete control.

Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!

Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

HPE Aruba patches critical Private 5G Core flaws. CVE-2026-23595 allows unauthenticated admin creation. Update to v1.25.1.0 now to prevent takeover.

GnuTLS v3.8.12 fixes high-severity DoS flaws (CVE-2026-1584). Malicious TLS 1.3 handshakes can crash servers. Update now to prevent outages.

WatchGuard patches two flaws: a VPN privilege escalation (NCPVE-2025-0626) and Fireware LDAP injection (CVE-2026-1498). Update Firebox and VPN clients now.
Hikvision patches high-severity command injection (CVE-2026-0709) in DS-3WAP access points. Authenticated attackers can execute code. Update now.

TP-Link fixes critical IDOR (CVE-2025-9520) in Omada Controller allowing admins to hijack Owner accounts. Update now to prevent total network takeover.
HPE patches critical RCE (CVE-2026-23592) in Fabric Composer. Authenticated attackers can seize the OS via backup tools. Update to v7.3.0 immediately.

Fortinet warns of critical flaw CVE-2026-24858 exploited in the wild. Attackers use FortiCloud SSO to bypass auth on FortiOS/Manager. Patch now.
TP-Link patches CVE-2025-14756 (CVSS 8.5) in Archer MR600 routers. This command injection flaw allows full device takeover. Update firmware now.

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

Cisco warns CVE-2026-20045 is being exploited. This critical RCE allows unauthenticated root access on Unified CM. Patch immediately to secure your network.

Arctic Wolf warns of automated FortiGate SSO attacks stealing configs and creating backdoors. Disable admin-forticloud-sso-login immediately.