 Do Son
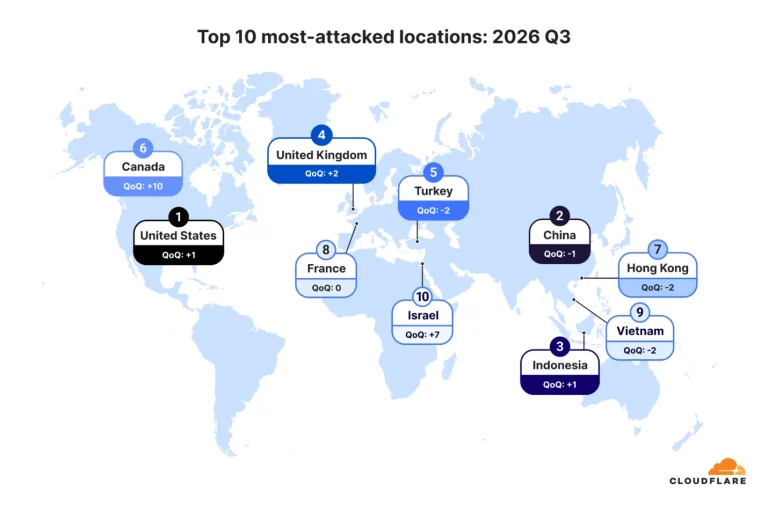
The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks.
network-security
Juniper security bulletin fixes 18 Session Smart Router vulnerabilities, including CVSS 9.8 flaws CVE-2026-103406 and CVE-2026-103409. Update now.
WatchGuard fixes 18 Fireware OS vulnerabilities on the Firebox firewall, including critical CVE-2026-103594 (CVSS 9.5). Upgrade to 2026.4 now.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
Nine HPE AOS-Switch vulnerabilities, including unauthenticated RCE flaw CVE-2026-76744 (CVSS 9.8), are fixed. Upgrade to AOS-S 16.11.0032.
Critical Arista CloudVision CUE vulnerability CVE-2026-102159 (CVSS 9.8) and five more flaws hit CV-CUE. Update to WiFi 2026.2.1 now.
Critical HPE ALE vulnerabilities threaten enterprise networks. Update HPE ALE vulnerabilities now to prevent unauthorized access and remote code execution.
An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
CISA warned of an exploited Zyxel switch vulnerability in GS1900 devices. Patch the Zyxel switch vulnerability now to prevent network compromise.
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
CVE-2026-73749, a critical HPE AOS-CX vulnerability, enables unauthenticated remote code execution at CVSS 9.8. HPE patched 31 flaws across its switches.
Ubiquiti patched 22 UniFi flaws. Three hit CVSS 10.0, including command injection CVE-2026-77537. Update UniFi Protect, OS, and Talk now.

Cisco SD-WAN vulnerability CVE-2026-20303 and CVE-2026-20304 reach CVSS 9.9. Cisco urges Catalyst SD-WAN customers to patch now.

Cisco IOS XE vulnerability CVE-2026-20272 hits CVSS 9.8 and CVE-2026-20267 scores 9.0. Cisco urges customers to patch now.

CVE-2026-18574 is a Check Point authentication bypass rated CVSS 9.3, letting attackers run commands as admin. Patch via the latest Jumbo Hotfix.

Read our weekly threat intelligence briefing. This vulnerability management report covers active exploits in Cisco, Ivanti, and Chrome for June 2026.

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.
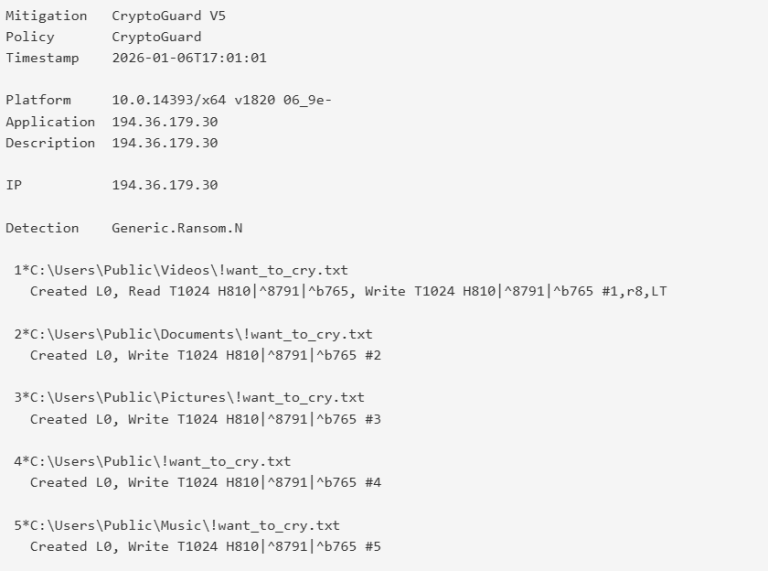
Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.

Cisco fixes a critical 8.6 CVSS XXE flaw (CVE-2026-20224) in Catalyst SD-WAN Manager. Unauthenticated attackers can read arbitrary files. Patch now!

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!
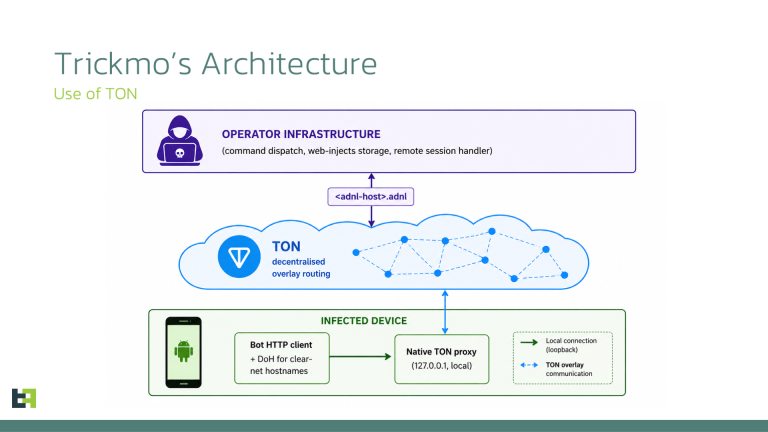
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.