 Do Son
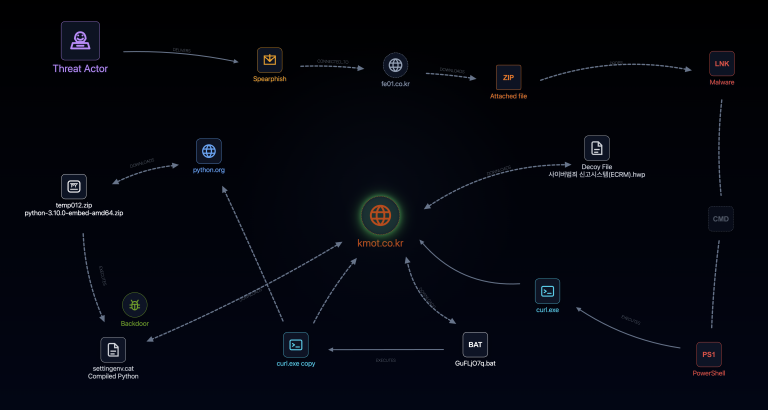
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
North Korea APT
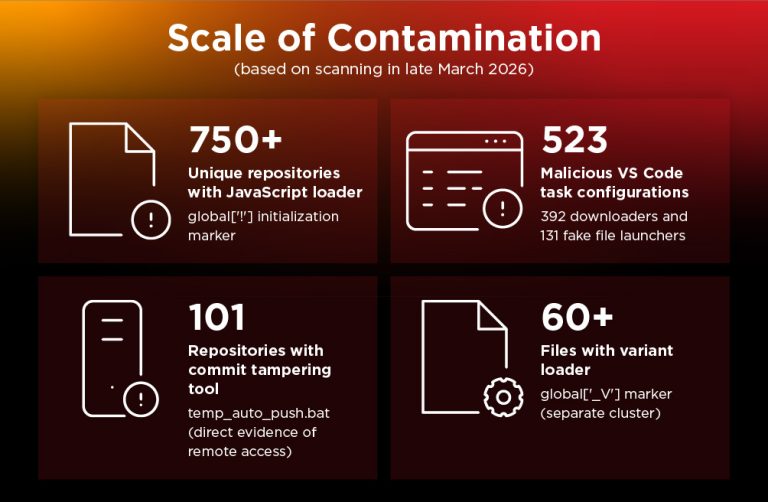
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.
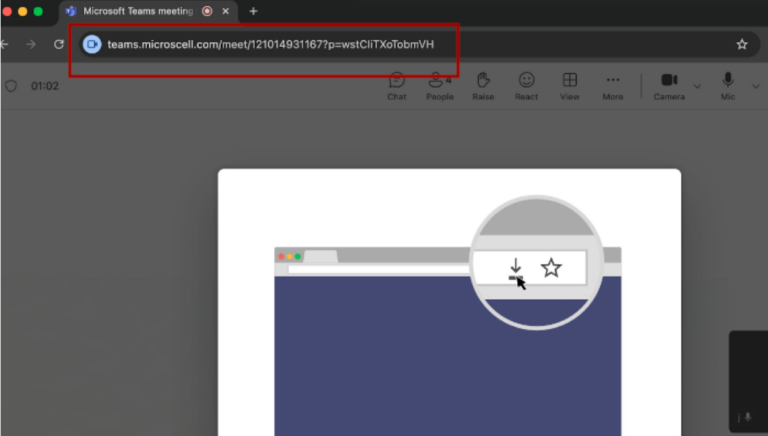
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

North Korean APTs added 197 malicious npm packages to the "Contagious Interview" campaign. The operation uses fake crypto job assignments to deploy the OtterCookie/BeaverTail hybrid to steal credentials cross-platform.

Gen Labs exposed Kimsuky deploying HttpTroy via fake VPN lures and Lazarus using an upgraded BLINDINGCAN RAT. Both North Korean APTs use DLL sideloading and custom crypto to evade analysis.

NTT exposed WaterPlum APT's multi-platform OtterCandy RAT (v2), which uses Node.js for remote control, targets 7 browser extensions, and now includes anti-forensic trace deletion.

Google exposed UNC5342 (DPRK APT) using EtherHiding—hiding JADESNOW/INVISIBLEFERRET malware in BNB/Ethereum smart contracts—for a resilient, nation-state C2 infrastructure.
Cisco Talos exposed Famous Chollima using fake job offers and a trojanized Node.js app (Chessfi) to infect developers. The OtterCookie RAT steals crypto wallets, credentials, and source code.
OtterCookie malware by North Korea-linked WaterPlum group evolves to target Chrome, MetaMask, and system files on both Windows and macOS platforms.