 Do Son
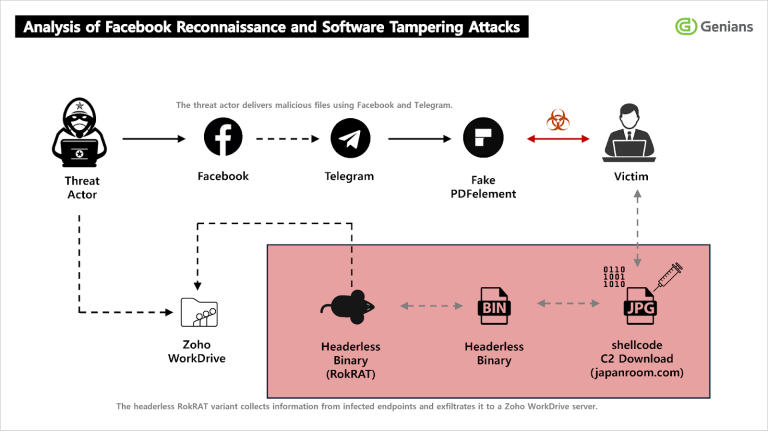
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.
North Korean APT
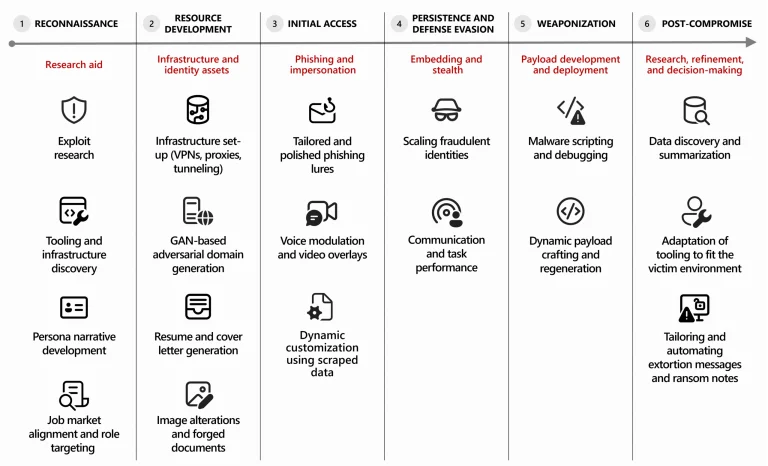
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
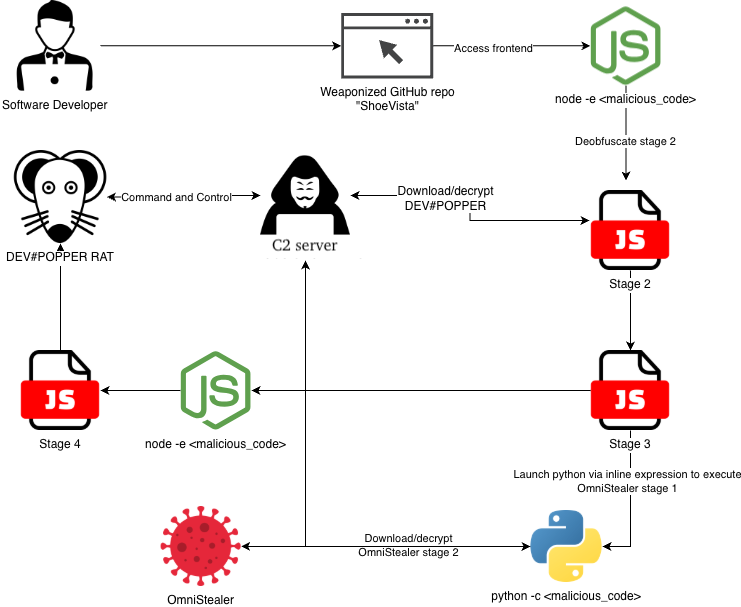
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.

Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

Uncover the tactics used by the North Korean APT group Kimsuky in their cyber espionage operations, including the use of the RDP Wrapper for persistent access.

Learn about the risks of DMARC misconfigurations and how they can be exploited by cybercriminals in spear-phishing campaigns.

Discover the latest cybersecurity threat: Citrine Sleet. Learn how this North Korean actor exploited a zero-day vulnerability in Chromium browsers.

QiAnXin Threat Intelligence Center's detailed analysis linked the binary involved in this operation to a North Korean APT