 Do Son
GitHub now expires npm trusted publishing setups that miss a first publish within 48 hours, closing a repo name reuse flaw in 1,500+ packages.
OIDC
A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.
CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.
CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.
A critical Poweradmin host header injection flaw (CVE-2026-54588) lets attackers hijack DNS admin accounts. Update to 4.2.4 or 4.3.3 now.
CVE-2026-48558, a SimpleHelp authentication bypass, is exploited in the wild to deploy TaskWeaver and Djinn Stealer. CISA added it to KEV. Patch now.
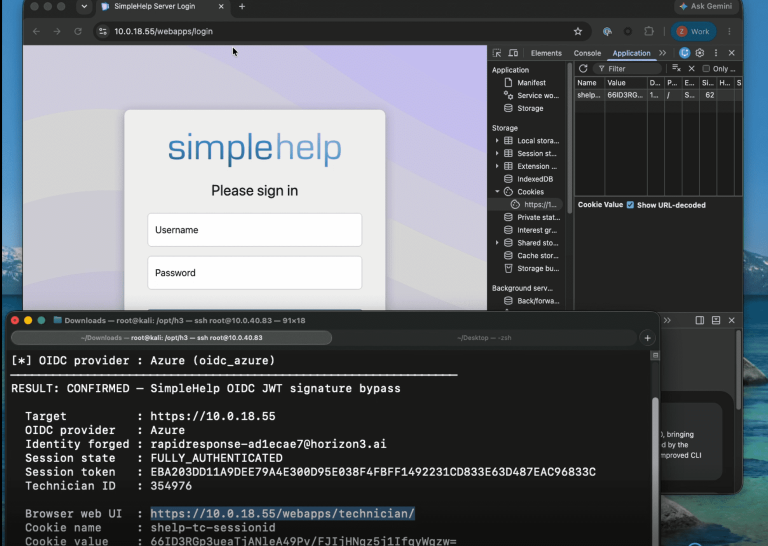
A critical SimpleHelp authentication bypass flaw leaves servers open. Attackers exploit the OIDC authentication flow to gain technician control.

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!
OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.