 Do Son
The cURL vulnerability reporting policy now routes low and medium severity bugs to public GitHub issues to alleviate maintainer triage burdens.
Open Source Security
Apache fixes 12 Apache Kylin vulnerabilities, including critical CVE-2026-64959, plus Apache Airflow SSH flaws. Upgrade Kylin to 5.0.5 now.
Fifteen Wazuh vulnerabilities, including two CVSS 9.4 flaws that allow remote code execution as root, are fixed in 4.14.8. Upgrade managers and agents now.
Twenty CRM vulnerability CVE-2026-105763 (CVSS 9.6) enables plaintext password disclosure of IMAP and SMTP accounts. Upgrade to 2.7.0.
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.
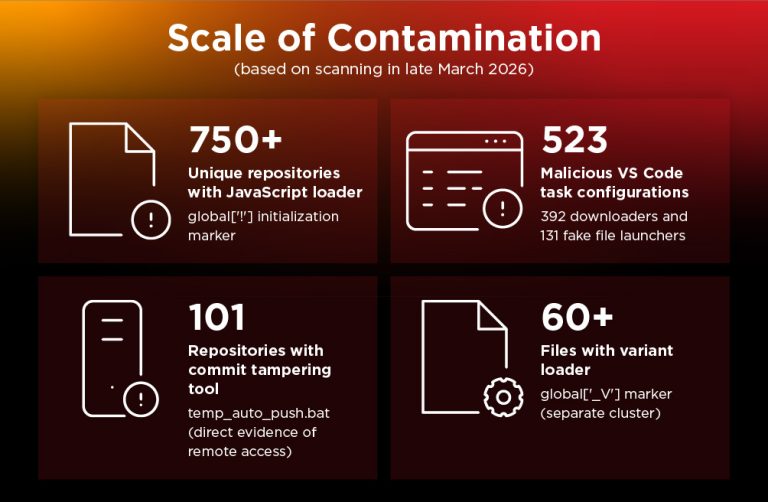
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!
Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!
A developer's "human error" leaked sensitive GitHub tokens in an Apache HTTP Server update. Learn how GitHub's safety nets prevented a major security breach.
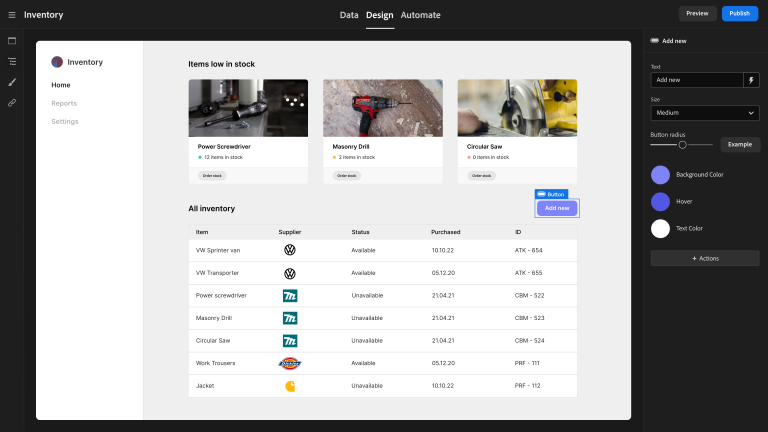
Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.
Keycloak 26.5.7 fixes an MFA bypass that could let attackers skip two-factor checks. Upgrade your identity server to close the gap.

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.

Squid Proxy patches critical 9.2 CVSS DoS and memory leak flaws in ICP. Standard access rules won't block the attack—upgrade to version 7.5 now.
MariaDB patches a high-severity buffer overflow (CVE-2026-32710) in its JSON validation function. Upgrade to 11.4.10 or 11.8.6 to prevent server crashes.
Tech giants pledge $12.5M to help open-source maintainers survive a "tempest" of AI-generated bug reports. Discover the 2026 plan to fortify the global supply chain.
OpenAI launches Codex Security, an advanced AI agent that uses reasoning to find and fix complex vulnerabilities without the noise of false positives.
A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.
AVideo patches two critical flaws (CVE-2026-28501 & 28502) allowing unauthenticated SQL injection and remote code execution. Update to version 23 now.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.
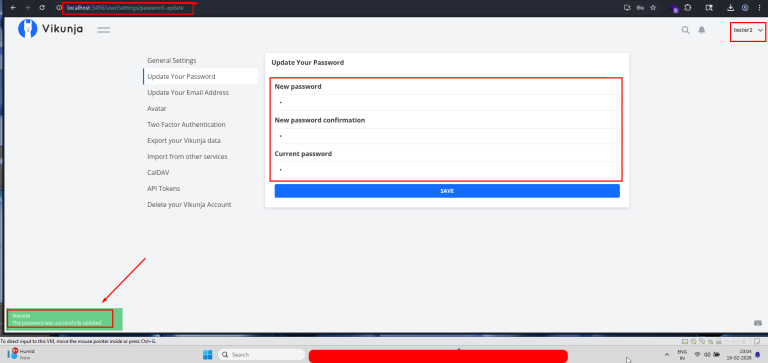
Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.
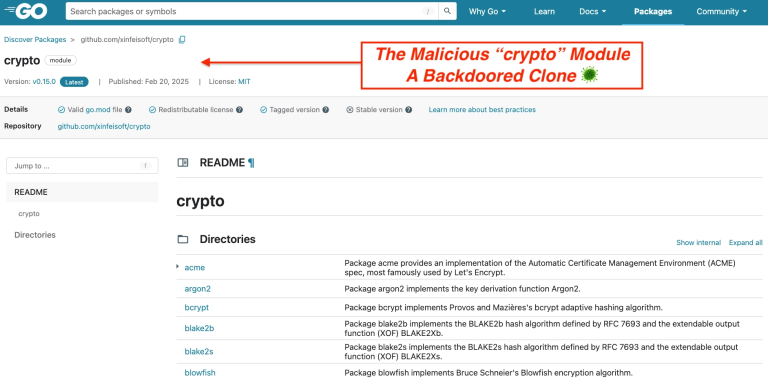
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.