
 Do Son
Threat actor uses React2Shell to deploy Sliver C2 on FortiWeb devices, using a Bangladesh Airforce decoy to target govt and financial sectors.
Pakistan

Qianxin exposed Bitter APT using a WinRAR path traversal flaw and malicious Office macros to deploy a C# backdoor against military/FinTech targets in Asia. The attack sets up scheduled persistence.

Kaspersky exposed the Mysterious Elephant APT targeting South Asia. The group uses MemLoader and custom tools (BabShell) to steal sensitive WhatsApp desktop data and exfiltrate documents.

The Confucius APT group is evolving, abandoning WooperStealer for the sophisticated AnonDoor Python backdoor to maintain stealthy, long-term espionage in South Asia.

Pakistan's critical sectors have been hit by the Blue Locker ransomware. This sophisticated campaign is linked to the Proton malware family and exploits a recent holiday.
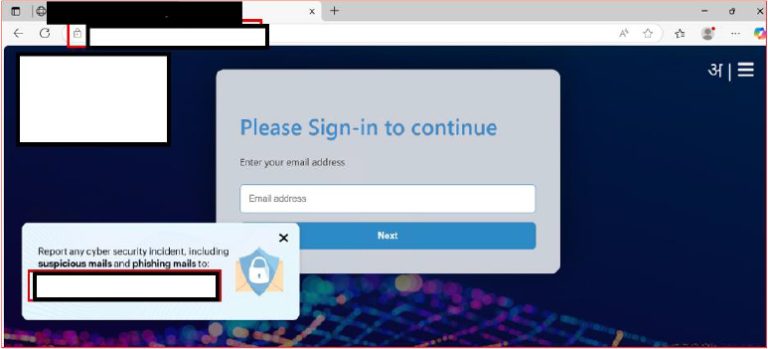
APT36, a Pakistan-linked threat actor, is targeting Indian government officials with phishing campaigns that mimic official websites to harvest credentials and Kavach MFA OTPs in real time.

A new report reveals APT36 (Transparent Tribe) is escalating cyber-espionage against India, using phishing and .desktop files to deploy the Poseidon backdoor for long-term access.

Seqrite Labs uncovers UNG0002, a South Asian APT group using advanced social engineering and new malware like Shadow RAT to target various sectors across Asia.

Amidst India-Pakistan tensions, Bitter APT launched a spear phishing campaign against Pakistan Telecommunication Company, using WmRAT for espionage.
The Central Bank of India announced on Friday that it would prohibit any link between banks and...