 Do Son
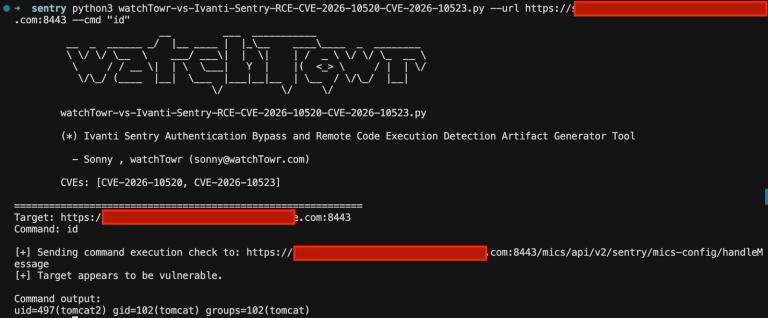
Critical Ivanti Sentry RCE details and a publicly disclosed PoC exploit are out. Patch the CVSS 10 and 9.9 flaws immediately to secure your network.
Patch Update

Fix critical Kemp LoadMaster flaws today. Learn how a command injection remote execution vulnerability leaves application networks exposed.

ABB addresses critical ABB T-MAC Plus vulnerabilities. Learn how these terminal system flaws allow authentication bypass and file disclosure.

Fix dangerous Apache MINA flaws immediately. Learn how a critical deserialization bypass and a DoS vulnerability leave Java applications exposed.

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.

New Broadcom security updates fix critical VMware stored XSS bugs. Learn how these vulnerabilities affect Cloud Foundation and how to patch now.
A critical Shopper Laravel flaw has emerged. This Shopper Laravel flaw exploit allows complete admin takeover, so update your store immediately.

A critical Langflow RCE vulnerability impacts the Shareable Playground feature. Learn about the new security patches available.

Learn about the new Notepad++ security flaws. Public Notepad++ exploit code triggers arbitrary code execution. Update to version v8.9.6.1 now.

The Samba Team dropped fixes for critical Samba vulnerabilities. Read about the remote code execution flaws carrying perfect 10.0 CVSS scores.

CVE-2026-9277 (CVSS 9.2) lets attackers inject commands via the shell-quote npm package. Check your dependencies and upgrade now.

NLnet Labs patches a critical Unbound DNSSEC validation vulnerability allowing unauthenticated remote code execution. Update to 1.25.1.

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Zimbra patches a high-severity LFI (CVE-2025-68645) allowing unauthenticated file access and a Flickr Zimlet credential leak. Upgrade to v10.1.13!

M-Files patches a high-severity flaw (CVE-2025-13008) that allows insiders to steal session tokens and impersonate users. Update to v25.12.15491.7!

n8n warns of a CVSS 10.0 RCE (CVE-2025-68613) in its expression system. Attackers can seize total server control. Upgrade to v1.122.0 immediately.

Apache NiFi patches a High-severity flaw (CVE-2025-66524) in the GetAsanaObject processor. Unfiltered deserialization risks system compromise. Update now!

Elastic patches a High-severity XSS flaw (CVE-2025-68385) in Kibana. Attackers can weaponize Vega visualizations to hijack sessions. Update now!

A Headlamp flaw allows unauthenticated users to reuse cached credentials to hijack Kubernetes Helm operations. Update to v0.39.0!

SonicWall warns of zero-day attacks chaining CVE-2025-40602 and CVE-2025-23006 to gain unauthenticated root access on SMA1000 appliances. Patch now!

A critical RCE flaw (CVSS 9.8) in Apache Commons Text mirrors Log4Shell, allowing server takeover. FileMaker Server users must update to v22.0.4 now.

Arista patches CVE-2025-0505, a CVSS 10 flaw in CloudVision ZTP that allows admin privilege escalation—on-premise users urged to upgrade.