 Do Son
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!
persistence
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
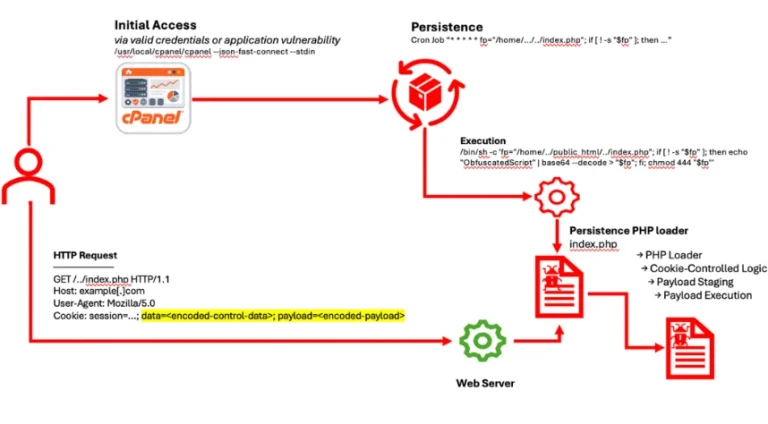
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

Hackers are weaponizing AWS termination protection to lock defenders out while they mine crypto on hijacked ECS/EC2 resources using a malicious Docker image.

CISA/NSA exposed BRICKSTORM, a Chinese state-sponsored backdoor targeting VMware vCenter/ESXi and ADFS servers. The self-restarting malware used DoH and nested TLS for 18 months of persistent espionage.

Patchwork APT deployed StreamSpy, a new trojan that uses WebSocket for covert C2 and HTTP for file transfer, blending malicious activity with web traffic to evade detection during espionage operations.

Broadcom exposed a group deploying multiple RMM tools (ScreenConnect, LogMeIn, Naverisk) weeks apart to achieve redundant persistence. The likely Initial Access Broker (IAB) prepares systems for resale.

A new campaign is using Bitcoin wallet lures to distribute DarkComet RAT. The UPX-packed trojan gains persistence via a fake explorer.exe binary and uses keylogging and remote control to steal data.

Cybereason exposed Tangerine Turkey, a VBScript worm that spreads via USB drives. It uses LOLBins (printui.exe) and Windows Defender exclusions to deploy the XMRig cryptominer for profit.

BitSight uncovered a Lampion banking Trojan campaign using ClickFix lures and a 700MB bloatware DLL to evade AV. The VBScript loader establishes persistence via the Windows Startup folder.

ReliaQuest exposed Flax Typhoon for a year-long breach, where the China-backed APT turned a legitimate ArcGIS Java SOE into a web shell and embedded it in backups to ensure persistence.

Point Wild uncovered Shuyal Stealer, a sophisticated infostealer targeting 19 browsers. It disables Windows Task Manager via a registry key and exfiltrates data via Telegram Bot API.

WARMCOOKIE has resurfaced post-Operation Endgame with new execution handlers, a MaaS model, and evasive techniques like disguised scheduled tasks using company names.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.

CYFIRMA's new report reveals REVENANT, a malware-free attack framework that can achieve long-term persistence by hiding in AI models and document fonts.

Netskope uncovers XWorm 6.0, a new variant using VBScript droppers, AMSI bypass, and critical process marking to evade detection and force system reboots if terminated.

AMOS malware just leveled up—now a backdoor, it poses a serious threat to macOS with persistent access and remote command execution.

IBM X-Force reveals Azure Arc can be exploited for RCE and privilege escalation via hardcoded secrets, recoverable credentials, and overscoped roles, turning it into a stealthy threat vector.

North Korean APTs are using "NimDoor," a new Nim-based macOS malware, to target Web3/crypto startups via fake Zoom meetings, stealing browser, Keychain, and Telegram data with novel persistence.

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.