 Do Son
Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.
PhaaS
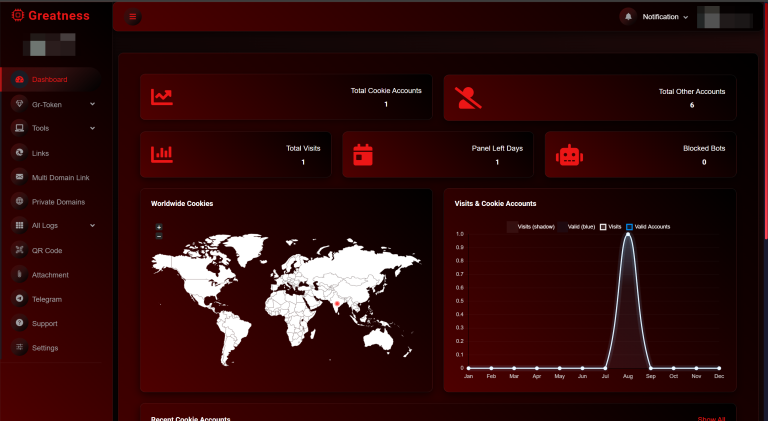
Researchers expose the Greatness PhaaS platform, an AiTM phishing kit sold on Telegram that steals Microsoft 365 tokens past MFA.
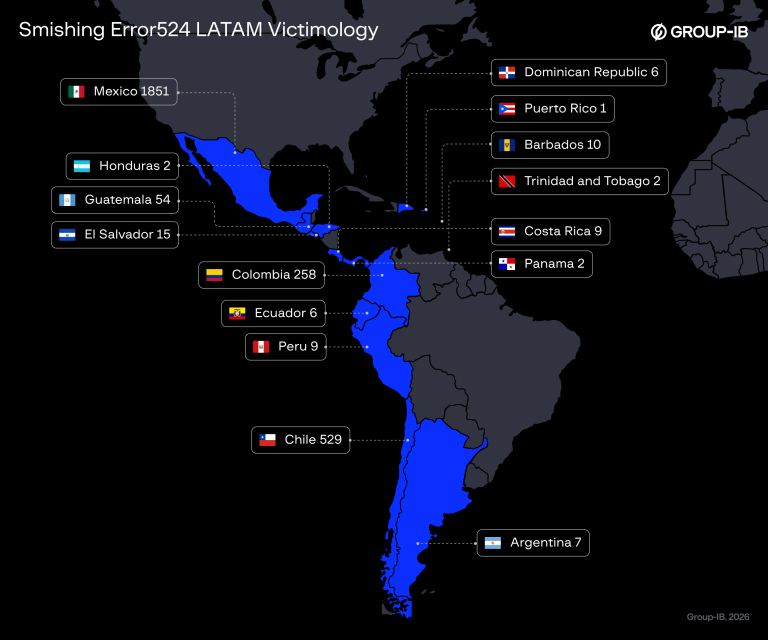
Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.
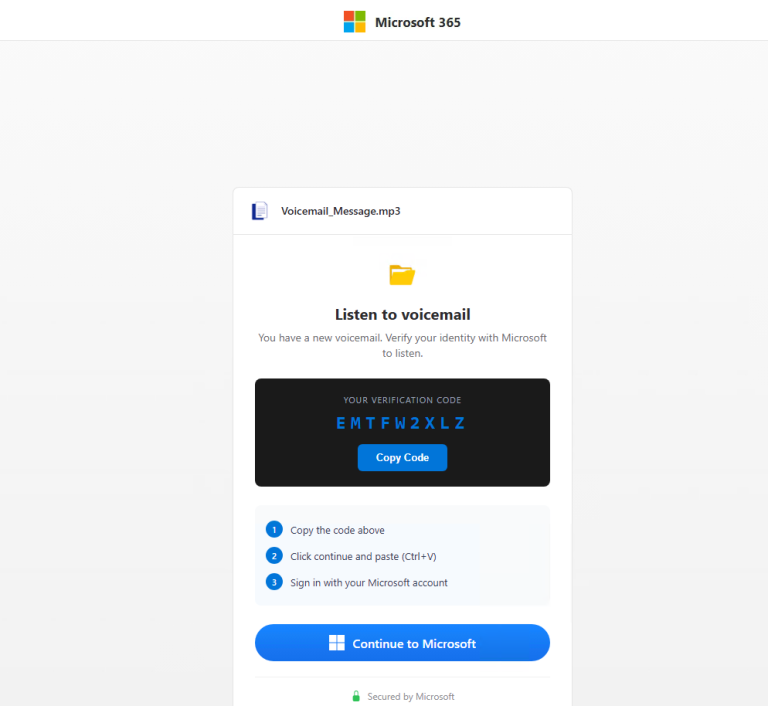
Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.
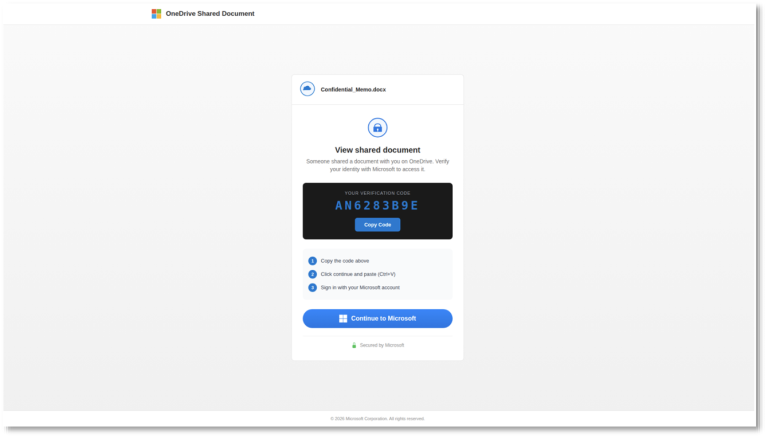
AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!
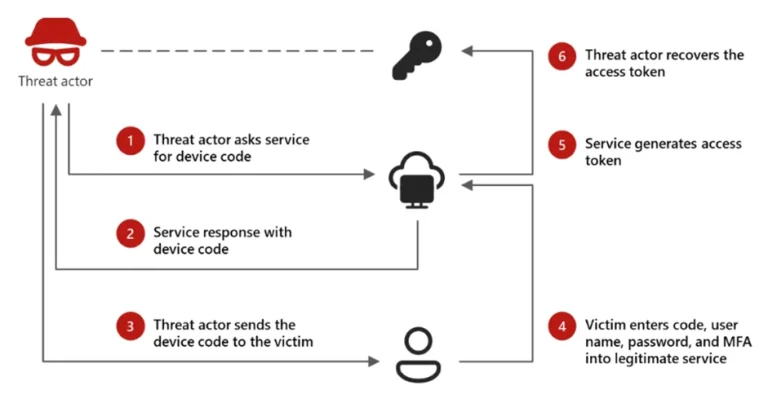
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
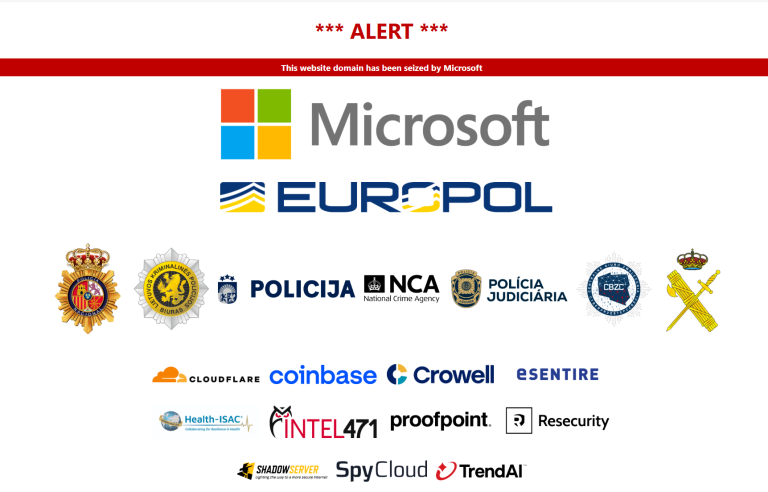
Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.

BlackForce, a new PhaaS kit, is being sold for €300, using React/React Router to disguise its code. It utilizes stateful sessions and MitB to bypass MFA in real time. Update to V5 shows rapid evolution.

Group-IB exposed an automated PhaaS kit that impersonates Aruba S.p.A. to steal credentials, credit card details, and OTPs. The multi-stage scam uses a CAPTCHA filter and Telegram for real-time exfiltration.

Unit 42 exposed the Smishing Triad, a PhaaS network that registered 194K+ malicious domains for global smishing. The group impersonates postal/banking services and uses Telegram for its underground market.

A new report reveals Chinese-speaking smishing syndicates are using phishing-as-a-service, MFA bypass, and stolen cards to conduct a multi-billion dollar fraud campaign targeting digital wallets.
Evalian uncovers a phishing campaign spoofing Red Bull job offers using legitimate services, low-cost VPS, and "slow kill" tactics to steal credentials via fake Facebook logins.

A new Sekoia report reveals a surge in AitM phishing, leveraging industrialized PhaaS kits to bypass MFA and compromise Microsoft 365 and Google accounts.

Haozi, a Chinese Phishing-as-a-Service platform, is back, offering no-code phishing kits and full support. Learn how this service enables easy cybercrime.
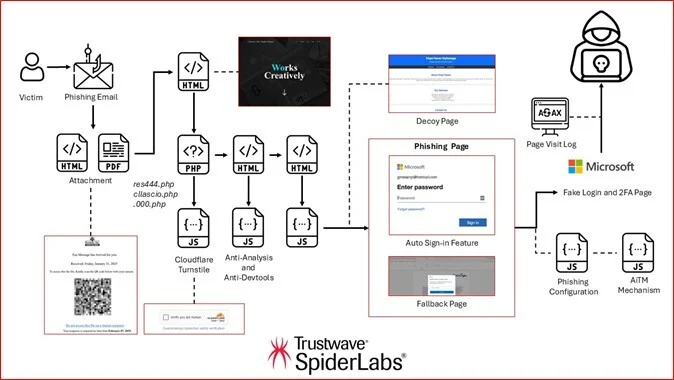
Trustwave uncovers Dadsec and Tycoon2FA, new Phishing-as-a-Service kits bypassing MFA to target Microsoft 365 users with advanced AiTM tactics.

mnemonic exposes Darcula, a global phishing-as-a-service network using the Magic Cat toolkit to target mobile users with encrypted, real-time scam dashboards.
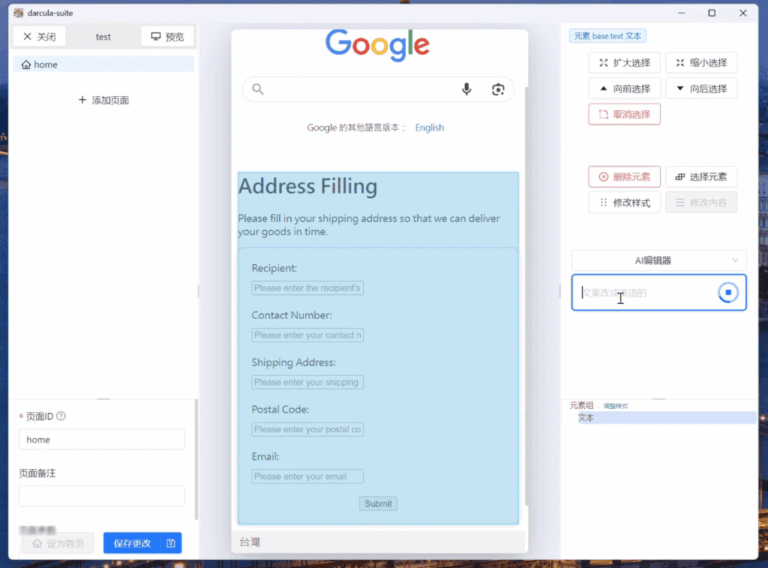
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.

Phishing attacks using SVG files surged 1800%, exploiting JavaScript and PhaaS kits to bypass MFA and steal credentials, Trustwave warns.