
 Do Son
Huntress exposed a covert campaign using log poisoning on exposed phpMyAdmin to deploy a web shell and the Nezha monitoring tool, ultimately delivering the Ghost RAT backdoor to 100+ victims in Asia.
phpmyadmin

Pro-Iranian group Cyber Fattah leaked thousands of sensitive Saudi Games participant records, including PII and bank data, in a political information operation targeting Saudi Arabia.

Learn about the recent XSS vulnerabilities in phpMyAdmin and how the latest release version 5.2.2 provides patches to address these security risks.
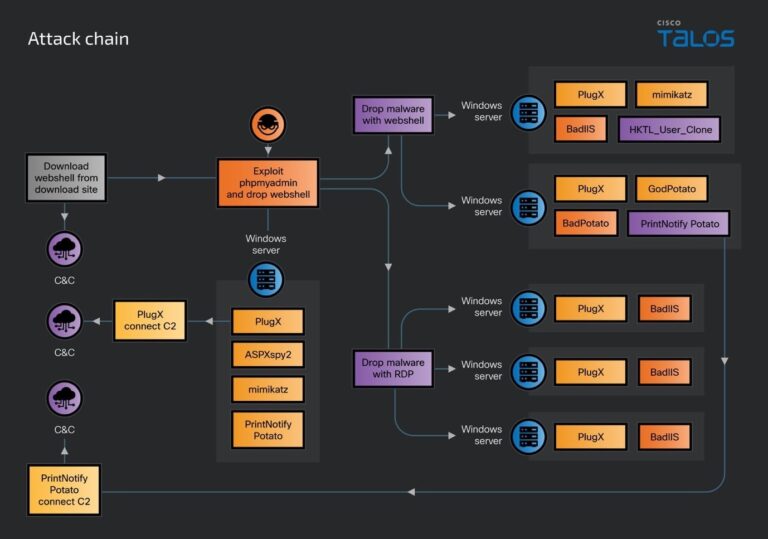
Learn about DragonRank, a Chinese threat actor specializing in SEO manipulation and cyberattacks. Find out how this group compromises websites and manipulates search engine rankings.
Discovered by the security researcher, Erol Guven, CVE-2023-25727 is an XSS attack and affects phpMyAdmin versions prior to 4.9.11 and 5.2.1
Recently, a new version of phpMyAdmin has been released to fix CSRF vulnerability that affects phpMyAdmin versions 4.7.x (prior to 4.7.7). By deceiving a user to click on a crafted URL, it is possible to perform harmful database operations such as deleting records, dropping/truncating tables etc.