 Do Son
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
Plugin Vulnerability
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!
Hackers are actively exploiting a 9.8 CVSS RCE flaw in Kali Forms (CVE-2026-3584). Over 10,000 WordPress sites are at risk. Update to version 2.4.10 now!
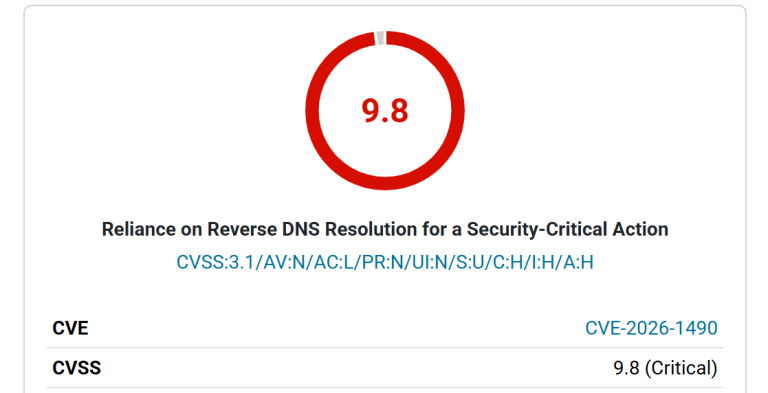
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.

Critical WPvivid Backup flaw CVE-2026-1357 (CVSS 9.8) allows unauthenticated file upload via null byte key. Update to v0.9.124 to prevent RCE.

Critical ACF Extended flaw CVE-2025-14533 (CVSS 9.8) lets attackers seize admin control. 100k sites at risk. Update to version 0.9.2.2 immediately.

Urgent patch for Post SMTP plugin. A CVSS 9.8 flaw lets unauthenticated attackers read email logs and steal password reset links to take over accounts.

Jenkins warned of a Critical SAML Plugin flaw (CVE-2025-64131) that allows session replay/hijacking due to a missing cache. Multiple plugins also expose API tokens in plaintext.

Urgent patch for WP Freeio plugin (v.< 1.2.22). Unauthenticated attackers can gain admin control instantly via a registration flaw. Update immediately to v.1.2.22.

LiteSpeed Cache for WordPress (LSCWP) versions 7.5.0.1 are vulnerable to a Reflected XSS flaw, exposing 7M sites to account takeover. Update to 7.6 now.
A critical vulnerability (CVE-2025-30911) in the RomethemeKit For Elementor WordPress plugin allows authenticated users to achieve RCE.