
 Do Son
Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.
PoC Exploit

Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.
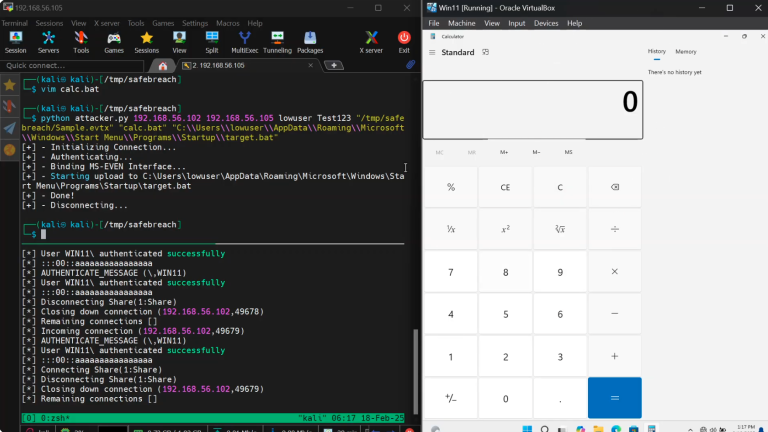
SafeBreach Labs releases PoC exploit code for EventLogin (CVE-2025-29969), a TOCTOU flaw in Windows MS-EVEN RPC allowing remote file writes. Patch now.

Public PoC released for Windows Storage flaw CVE-2026-21508. Attackers can gain SYSTEM privileges via WUDFHost.exe. Patch Windows 11 immediately.

Public PoC exploit released for critical Firefox WebRTC flaw CVE-2025-14321 (CVSS 9.8). AI-discovered bug allows remote code execution. Update now.
Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

A failed patch created Windows kernel flaw CVE-2025-53136. With reliable PoC exploit code now public, KASLR is bypassed. Update your systems now.

PoC exploit code released for critical FortiSIEM flaw CVE-2025-64155 (CVSS 9.4). Unauthenticated RCE allows root access. Upgrade to v7.4.1 now.

Critical CVSS 9.8 RCE in Netflix Conductor lets attackers gain remote shell via JavaScript injection. Exploit PoC available. Patch now!

CVE-2025-49144 lets attackers gain NT AUTHORITY\SYSTEM via Notepad++ v8.8.1 installer flaw. PoC available—secure paths and signatures urged.

A flaw (CVE-2025-4232) in GlobalProtect for macOS allows local users to escalate to root. Public PoC code exists. Update now!

CVE-2025-4318 (CVSS 9.5) hits AWS Amplify Codegen UI with PoC exploit. RCE flaw puts CI/CD pipelines and developer environments at high risk.

A new PoC shows how BitLocker can be bypassed in minutes using Bitpixie (CVE-2023-21563). No hardware needed—just a PXE boot and memory scan.

Branch Privilege Injection breaks Intel’s Spectre defenses via race conditions. ETH Zürich reveals PoC leaking memory on fully patched systems.

To extract the victim's session, researchers release a Ruby proof-of-concept (PoC) exploit code for CVE-2024-53704 , which is available here.

Dubbed "Leaked Wallpaper" by Michael Zhmaylo, CVE-2024-38100 vulnerability enables the leakage of a user's NetNTLM hash from any session