
 Do Son
A new security update for PostgreSQL fixes three vulnerabilities, including two critical flaws that could lead to remote code execution.
PostgreSQL

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.

PHP patches two flaws: CVE-2025-1735 allows SQL injection/crashes in pgsql, and CVE-2025-6491 enables DoS in SOAP via oversized XML. Update immediately!

DataEase has critical flaws in database connection handling, allowing remote RCE and JDBC parameter bypasses for H2, Redshift, and PostgreSQL. Update to v2.10.11 now!

A flaw (CVE-2025-49146) in PostgreSQL JDBC Driver allows MITM attacks even with channel binding enabled. Upgrade to v42.7.7 or use sslMode=verify-full.

Bitnami Pgpool flaw (CVE-2025-22248) exposes PostgreSQL to unauthenticated access. Update to Pgpool 4.6.0-1 or Helm chart 16.0.0 to fix.

Uncover the dangers of fileless cryptominers that exploit PostgreSQL servers. Learn how JINX-0126 stealthily operates.

Learn about CVE-2024-55963, a critical vulnerability in Appsmith that allows remote code execution due to PostgreSQL misconfiguration.

Explore the evolving threat of Albabat ransomware targeting Windows, Linux, and macOS systems with new, undetected variants.

Learn about CVE-2025-26701, a critical security vulnerability in PMM that allows unauthorized root access to database environments.
Explore CVE-2025-1094, a high-severity SQL injection vulnerability in PostgreSQL's psql tool that can execute arbitrary code.

Stay protected from PostgreSQL vulnerability with the latest important security update. Learn about the risks and how to mitigate them.
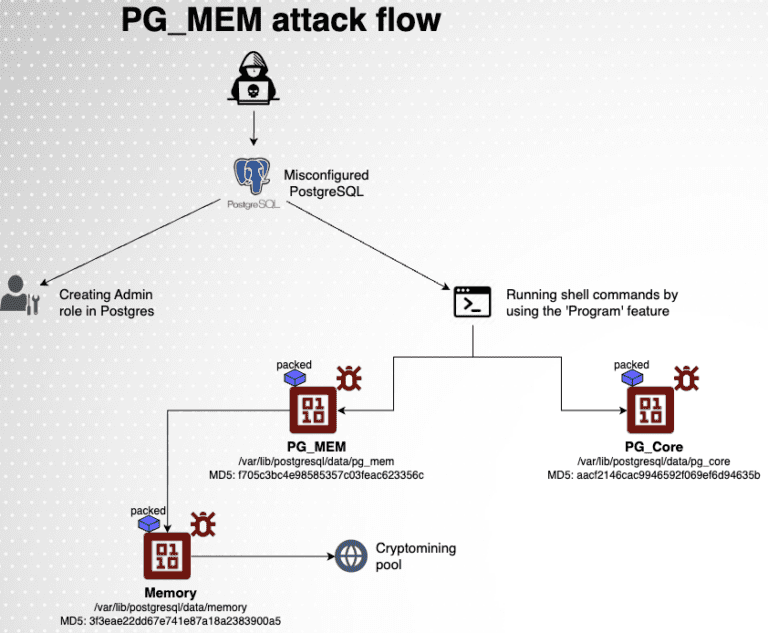
Beware of PG_MEM: a new malware targeting PostgreSQL. Learn how this sophisticated threat exploits and mines cryptocurrency.

Learn about the critical PostgreSQL security advisory (CVE-2024-7348) and how it exposes users to the risk of arbitrary SQL execution.

A high-severity security vulnerability (CVE-2024-32655) has been discovered in Npgsql, a widely used open-source data provider

CVE-2024-2044 in pgAdmin 4 could have allowed a remote, authenticated attacker to execute arbitrary code on affected systems
A recently discovered vulnerability (CVE-2024-1597, CVSS 10) highlights the importance of vigilance and proactive security measures

This vulnerability, designated CVE-2024-0985 (CVSS 8.0), could allow attackers to execute malicious code with elevated privileges

A Linux-based malware family, DreamBus has been quietly evolving, honing its capabilities to exploit vulnerabilities in business applications

Identified as CVE-2023-49954, this security loophole is an SQL Injection flaw found in 3CX CRM Integration.
CVE-2023-5869, is a buffer overrun vulnerability that could allow attackers to execute arbitrary code on the PostgreSQL server

CVE-2023-5002 vulnerability has been discovered in pgAdmin, a popular graphical user interface (GUI) management tool for PostgreSQL databases