
 Do Son
Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.
PowerShell Malware

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
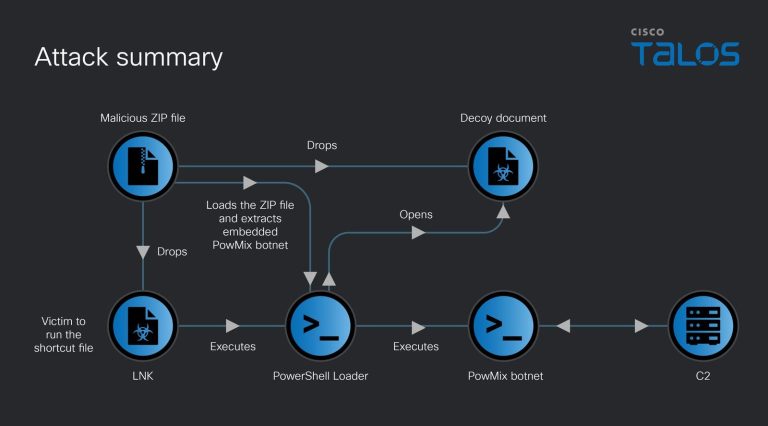
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.
CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.

Remcos RAT campaign evades antivirus using PowerShell-based in-memory execution. Steals data, bypasses UAC, and avoids detection with stealthy tactics.

Chihuahua Stealer uses stealthy PowerShell loaders, CNG AES-GCM encryption, and .NET memory injection to exfiltrate browser and crypto wallet data.

ThreatLabz reveals StealC V2—an evolving info-stealer with encrypted C2, MSI and PowerShell payloads, and a rule-driven control panel for targeted attacks.