
 Do Son
Axis Communications releases critical patches for AXIS OS vulnerabilities, including privilege escalation flaws. Update your devices to stay protected.
privilege escalation
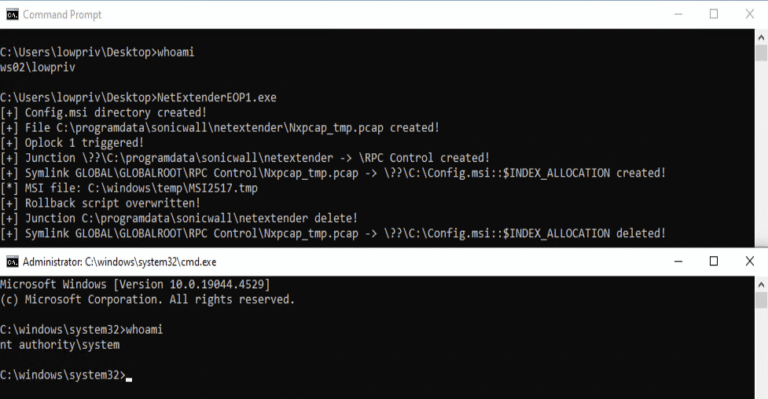
High-risk LPE vulnerabilities in SonicWall NetExtender for Windows (CVE-2025-23009, CVE-2025-23010) allow SYSTEM access or DoS. Patch immediately to version 10.3.2.

Hitachi Energy's Asset Suite, used in power gen, faces severe vulnerabilities including XSS, plaintext passwords, & RCE. Immediate action advised to secure systems.

ISC uncovers security flaws in its Kea DHCP server, including privilege escalation and data leakage. Update to Kea 2.4.2, 2.6.3, or 2.7.9 immediately.
A critical Cyrus IMAP vulnerability (CVSS 9.8) on openSUSE allows unprivileged users to gain root access, risking full system compromise.

Lenze VPN Client for x500 IoT gateways has critical flaws allowing arbitrary code execution via local privilege escalation.

Exploit BadSuccessor to take over domains with PoC code. No patch, full AD compromise via dMSAs in Windows Server 2025.

ABB's ASPECT BMS has 32 security flaws, with some critical RCE and privilege escalation vulnerabilities having no planned fixes for legacy systems.
Cisco patches two privilege escalation flaws in Unified Intelligence Center that could expose sensitive data. Users urged to upgrade immediately.

CVE-2025-22157 is a CVSS 7.2 Jira vulnerability allowing privilege escalation. Update Jira Data Center now to prevent unauthorized access.

A critical flaw in Broadcom's Automic Automation Agent for Unix exposes systems to privilege escalation. Check your version and update to stay secure.

Critical vulnerability (CVSS 9.8) in the Motors WordPress theme! This flaw puts over 22,000 websites at risk of full takeover. Update now!

Over 10,000 WordPress sites at risk from Eventin plugin flaw CVE-2025-47539. Attackers can gain admin access via unauthenticated API exploit.

PoC for CVE-2023-41992 reveals iOS kernel flaw enabling local privilege escalation. Apple patched it, but risks persist for outdated devices.
Zoom fixes critical CVE-2025-30663 flaw allowing local privilege escalation. Users urged to update Workplace apps and SDKs to version 6.4.0 or newer.

May 2025 Patch Tuesday fixes 83 Microsoft flaws, including 5 zero-days actively exploited. Critical updates address RCE and SYSTEM privilege bugs.

A security audit reveals critical flaws in GNU Screen, including a root exploit. The flaws impact both Screen 5.0.0 and 4.9.x, posing a major risk to Linux/UNIX systems.

Arista patches CVE-2025-0505, a CVSS 10 flaw in CloudVision ZTP that allows admin privilege escalation—on-premise users urged to upgrade.

Critical CVE-2024-11186 in Arista CloudVision Portal allows authenticated users broader network actions. Patch or mitigate now.

Microsoft patched critical Azure & Power Apps security flaws before exploitation. No user action needed. Stay informed on cloud security.

A zero-day privilege escalation vulnerability (CVE-2025-29824) in Microsoft CLFS was exploited by Balloonfly (Play ransomware) before the official patch.

MediaTek’s May 2025 bulletin reveals high-severity modem flaw CVE-2025-20666 & Android bugs risking denial of service & local privilege escalation