 Do Son
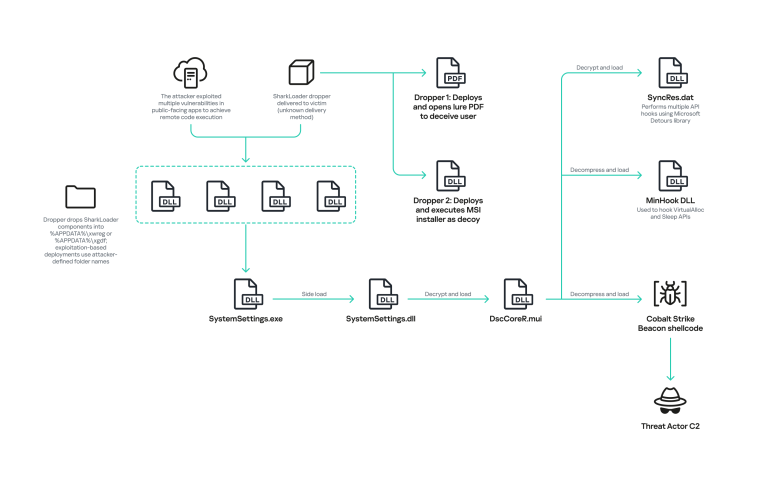
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.
ProxyLogon
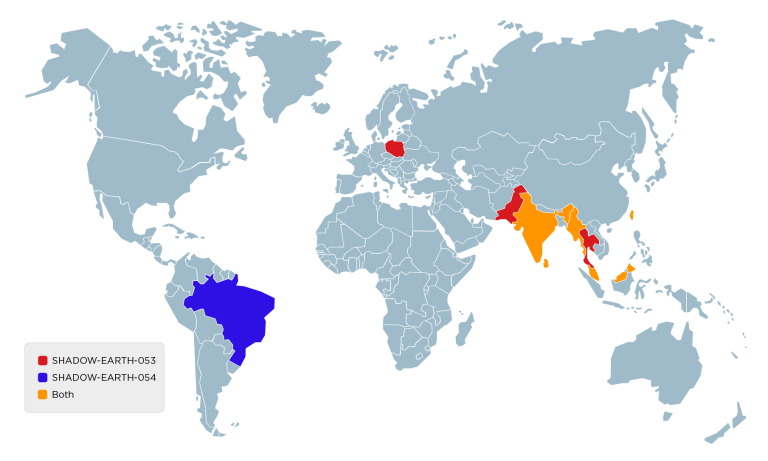
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.

Explore the latest revelations on Head Mare's cyber tactics and their collaboration with Twelve in recent attacks on Russian companies.

Learn about the Earth Estries APT group, a significant cyber espionage actor targeting critical sectors and industries worldwide.

Nearly three years after the notorious ProxyLogon and ProxyShell vulnerabilities caused widespread havoc on Microsoft Exchange servers